
Oracle Critical Patch Update July 2013
Released July 2013 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, June 2013 · Critical Patch Update, October 2013 →
89 CVEs in this release, one square each
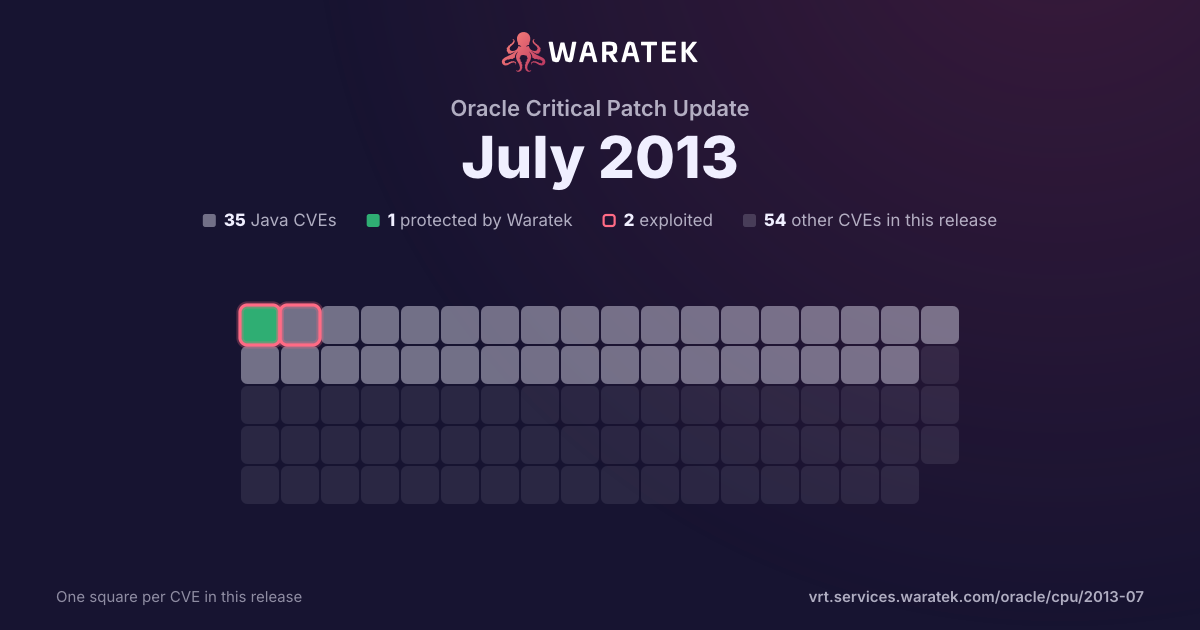
By status
1Protected by Waratek3Mitigation candidate31No exploit published8Outside Waratek scope46Not applicable
2Exploited, marked by the ring
No exploit published. For 31 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 35 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
35matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
2public PoC5.7%
2EPSS ≥ 0.55.7%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
35
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
35
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
2
5.7%
Proof of concept only
0
0.0%
Forecast only
2
5.7%
No public exploit
31
88.6%
split by
peak 26 / year
20051
Not applicable1
Medium1
not blocked1
Forecast only1
20060
20073
Not applicable3
Medium3
not blocked3
No public exploit3
20082
Not applicable2
Medium2
not blocked2
Forecast only1
No public exploit1
20090
20102
Not applicable2
Medium2
not blocked2
No public exploit2
20111
Not applicable1
Medium1
not blocked1
Working exploit published1
20120
201326
Not applicable26
Medium26
not blocked26
Working exploit published1
No public exploit25
200520062007200820092010201120122013
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-3813 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows remote attackers to affect confidentiality and integrity via vectors related to Libraries/PAM-Unix. |
| CVE-2013-3809 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.31 and earlier and 5.6.11 and earlier allows remote authenticated users to affect integrity via unknown vectors related to Audit Log. |
| CVE-2013-3808 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.1.68 and earlier, 5.5.30 and earlier, and 5.6.10 allows remote authenticated users to affect availability via unknown vectors related to Server Options. |
| CVE-2013-3807 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.11 and earlier allows remote attackers to affect confidentiality and integrity via unknown vectors related to Server Privileges. |
| CVE-2013-3806 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.11 and earlier allows remote authenticated users to affect availability via unknown vectors related to InnoDB, a different vulnerability than CVE-2013-3811. |
| CVE-2013-3805 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.30 and earlier and 5.6.10 allows remote authenticated users to affect availability via unknown vectors related to Prepared Statements. |
| CVE-2013-3804 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.1.69 and earlier, 5.5.31 and earlier, and 5.6.11 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server Optimizer. |
| CVE-2013-3802 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.1.69 and earlier, 5.5.31 and earlier, and 5.6.11 and earlier allows remote authenticated users to affect availability via unknown vectors related to Full Text Search. |
| CVE-2013-3801 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.30 and earlier and 5.6.10 allows remote authenticated users to affect availability via unknown vectors related to Server Options. |
| CVE-2013-3799 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11, when running on AMD64, allows local users to affect availability via unknown vectors related to Kernel. |
| CVE-2013-3798 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.11 and earlier allows remote attackers to affect integrity and availability via unknown vectors related to MemCached. |
| CVE-2013-3797 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 allows local users to affect availability via unknown vectors related to Filesystem/DevFS. |
| CVE-2013-3796 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.11 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server Optimizer. |
| CVE-2013-3795 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.11 and earlier allows remote authenticated users to affect availability via unknown vectors related to Data Manipulation Language. |
| CVE-2013-3794 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.30 and earlier and 5.6.10 allows remote authenticated users to affect availability via unknown vectors related to Server Partition. |
| CVE-2013-3793 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.31 and earlier and 5.6.11 and earlier allows remote authenticated users to affect availability via unknown vectors related to Data Manipulation Language. |
| CVE-2013-3787 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 allows remote attackers to affect availability via unknown vectors related to Kernel. |
| CVE-2013-3786 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 9, 10, and 11 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Kernel. |
| CVE-2013-3783 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.31 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server Parser. |
| CVE-2013-3782 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Secure Global Desktop component in Oracle Virtualization 4.6 prior to 4.63 and 4.7 prior to 4.71 allows remote attackers to affect integrity via unknown vectors related to Web UI. |
| CVE-2013-3773 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the SPARC Enterprise M Series Servers component in Oracle and Sun Systems Products Suite XCP 1114 and earlier allows remote attackers to affect availability via vectors related to XSCF Control Package (XCP). |
| CVE-2013-3765 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 allows local users to affect availability via unknown vectors related to Kernel/VM. |
| CVE-2013-3757 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, 10, and 11 allows remote attackers to affect integrity and availability via vectors related to SMF/File Locking Services. |
| CVE-2013-3752 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 allows remote attackers to affect integrity via vectors related to Service Management Facility (SMF). |
| CVE-2013-0398 | Medium | 2013-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, 10, and 11 allows remote attackers to affect confidentiality via unknown vectors related to Utility/Remote Execution Server (in.rexecd). |
| CVE-2013-1861 | Medium | 2013-03-28 | Not applicable | Working exploit published | MariaDB 5.5.x before 5.5.30, 5.3.x before 5.3.13, 5.2.x before 5.2.15, and 5.1.x before 5.1.68, and Oracle MySQL 5.1.69 and earlier, 5.5.31 and earlier, and 5.6.11 and earlier allows remote attackers to cause a denial of service (crash) via a crafted geometry feature that specifies a large number of points, which is not properly handled when processing the binary representation of this feature, related to a numeric calculation error. |
| CVE-2011-0419 | Medium | 2011-05-16 | Not applicable | Working exploit published | Stack consumption vulnerability in the fnmatch implementation in apr_fnmatch.c in the Apache Portable Runtime (APR) library before 1.4.3 and the Apache HTTP Server before 2.2.18, and in fnmatch.c in libc in NetBSD 5.1, OpenBSD 4.8, FreeBSD, Apple Mac OS X 10.6, Oracle Solaris 10, and Android, allows context-dependent attackers to cause a denial of service (CPU and memory consumption) via *? sequences in the first argument, as demonstrated by attacks against mod_autoindex in httpd. |
| CVE-2010-2068 | Medium | 2010-06-18 | Not applicable | No public exploit | mod_proxy_http.c in mod_proxy_http in the Apache HTTP Server 2.2.9 through 2.2.15, 2.3.4-alpha, and 2.3.5-alpha on Windows, NetWare, and OS/2, in certain configurations involving proxy worker pools, does not properly detect timeouts, which allows remote attackers to obtain a potentially sensitive response intended for a different client in opportunistic circumstances via a normal HTTP request. |
| CVE-2010-0434 | Medium | 2010-03-05 | Not applicable | No public exploit | The ap_read_request function in server/protocol.c in the Apache HTTP Server 2.2.x before 2.2.15, when a multithreaded MPM is used, does not properly handle headers in subrequests in certain circumstances involving a parent request that has a body, which might allow remote attackers to obtain sensitive information via a crafted request that triggers access to memory locations associated with an earlier request. |
| CVE-2008-2364 | Medium | 2008-06-13 | Not applicable | No public exploit | The ap_proxy_http_process_response function in mod_proxy_http.c in the mod_proxy module in the Apache HTTP Server 2.0.63 and 2.2.8 does not limit the number of forwarded interim responses, which allows remote HTTP servers to cause a denial of service (memory consumption) via a large number of interim responses. |
| CVE-2007-6388 | Medium | 2008-01-08 | Not applicable | Forecast only | Cross-site scripting (XSS) vulnerability in mod_status in the Apache HTTP Server 2.2.0 through 2.2.6, 2.0.35 through 2.0.61, and 1.3.2 through 1.3.39, when the server-status page is enabled, allows remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2007-5000 | Medium | 2007-12-13 | Not applicable | No public exploit | Cross-site scripting (XSS) vulnerability in the (1) mod_imap module in the Apache HTTP Server 1.3.0 through 1.3.39 and 2.0.35 through 2.0.61 and the (2) mod_imagemap module in the Apache HTTP Server 2.2.0 through 2.2.6 allows remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2007-3847 | Medium | 2007-08-23 | Not applicable | No public exploit | The date handling code in modules/proxy/proxy_util.c (mod_proxy) in Apache 2.3.0, when using a threaded MPM, allows remote origin servers to cause a denial of service (caching forward proxy process crash) via crafted date headers that trigger a buffer over-read. |
| CVE-2006-5752 | Medium | 2007-06-27 | Not applicable | No public exploit | Cross-site scripting (XSS) vulnerability in mod_status.c in the mod_status module in Apache HTTP Server (httpd), when ExtendedStatus is enabled and a public server-status page is used, allows remote attackers to inject arbitrary web script or HTML via unspecified vectors involving charsets with browsers that perform "charset detection" when the content-type is not specified. |
| CVE-2005-3352 | Medium | 2005-12-13 | Not applicable | Forecast only | Cross-site scripting (XSS) vulnerability in the mod_imap module of Apache httpd before 1.3.35-dev and Apache httpd 2.0.x before 2.0.56-dev allows remote attackers to inject arbitrary web script or HTML via the Referer when using image maps. |