
Oracle Critical Patch Update April 2011
Released April 2011 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, February 2011 · Java SE Critical Patch Update, June 2011 →
72 CVEs in this release, one square each
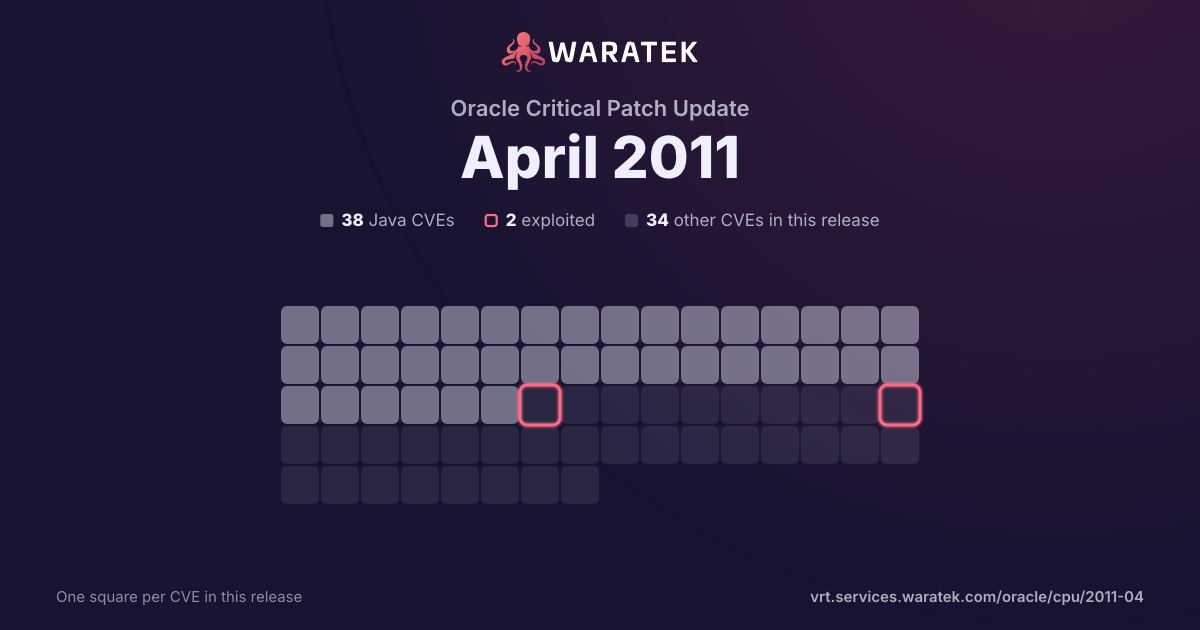
By status
3Mitigation candidate35No exploit published9Outside Waratek scope25Not applicable
2Exploited, marked by the ring
No exploit published. For 35 of them, Oracle's security advisory is the source of public detail.
Overview 5 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
5matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
5
100.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
5
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
5
100.0%
split by
peak 5 / month
Apr 11
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2011-0808 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.3.2.0 and 8.3.5.0 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Outside In Filters. NOTE: the previous information was obtained from the April 2011 CPU. Oracle has not commented on claims from a reliable third party that this issue is in (a) vswk6.dll or (b) libvs_wk6.so in Outside In 8.1.0.4037 through 8.3.5.5684, involving the Lotus 123 parser. |
| CVE-2011-0798 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Portal component in Oracle Fusion Middleware 10.1.2.3 and 11.1.1.2.0 allows remote attackers to affect integrity via unknown vectors related to Midtier Infrastructure. |
| CVE-2011-0795 | Low | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Single Sign On component in Oracle Fusion Middleware 10.1.2.3 allows remote authenticated users to affect integrity via unknown vectors related to Administration and Monitoring. |
| CVE-2011-0794 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.3.5.0 allows local users to affect confidentiality, integrity, and availability, related to File ID SDK. NOTE: the previous information was obtained from the April 2011 CPU. Oracle has not commented on claims from a reliable third party that this issue is in (a) sccut.dll or (b) libsc_ut.so in Outside In 8.3.5.x through 8.3.5.5684, as used when using the CAB file identification functionality to parse OneNote (.onepkg) files and other formats. |
| CVE-2011-0789 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 10.1.2.3 allows remote attackers to affect integrity via unknown vectors. |