
Overview 54 matches · 3 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 5 public PoC · 1 EPSS ≥ 0.5
54matches
3in Waratek scope5.6%
1protected1.9%
0exploited0.0%
0CISA KEV0.0%
5public PoC9.3%
1EPSS ≥ 0.51.9%
Protected by Waratek
1
1.9%
Rule in development
0
0.0%
Mitigation candidate
1
1.9%
No exploit published
1
1.9%
Outside Waratek scope
0
0.0%
Not applicable
51
94.4%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
1.9%
partly blocked
0
0.0%
not blocked
53
98.1%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
54
100.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 22 / year
20191
Protected by Waratek1
Critical1
blocked by ARMR today1
Proof of concept only1
20200
20211
Not applicable1
Medium1
not blocked1
Proof of concept only1
20224
Mitigation candidate1
No exploit published1
Not applicable2
Critical2
High1
Medium1
not blocked4
Proof of concept only4
202312
Not applicable12
Critical2
High3
Medium7
not blocked12
Proof of concept only12
20248
Not applicable8
High4
Medium4
not blocked8
Proof of concept only8
20256
Not applicable6
Critical3
High2
Medium1
not blocked6
Proof of concept only6
202622
Not applicable22
High7
Medium13
Low2
not blocked22
Proof of concept only22
20192020202120222023202420252026
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2026-7023 | Low | 2026-04-26 | Not applicable | Proof of concept only | A vulnerability was detected in ByteDance coze-studio up to 0.5.1. Affected by this vulnerability is the function ExecuteSQL of the file backend/domain/memory/database/service/database_impl.go of the component databaseTool. Performing a manipulation results in sql injection. The attack can be initiated remotely. The exploit is now public and may be used. The vendor was contacted early about this disclosure but did not respond in any way. |
| CVE-2019-25655 | Medium | 2026-03-30 | Not applicable | Proof of concept only | Device Monitoring Studio 8.10.00.8925 contains a denial of service vulnerability that allows local attackers to crash the application by supplying an excessively long string to the server connection dialog. Attackers can trigger the crash by entering a malformed server name or address containing repeated characters through the Tools menu Connect to New Server interface. |
| CVE-2018-25227 | Medium | 2026-03-30 | Not applicable | Proof of concept only | Valentina Studio 9.0.4 contains a denial of service vulnerability that allows local attackers to crash the application by supplying an excessively long string in the Host field. Attackers can trigger the crash by pasting a 256-byte buffer of repeated characters into the Host parameter during server connection attempts. |
| CVE-2019-25625 | Medium | 2026-03-23 | Not applicable | Proof of concept only | Blob Studio 2.17 contains a denial of service vulnerability that allows local attackers to crash the application by providing malformed input through the key entry mechanism. Attackers can create a text file with a large buffer of repeated characters and trigger the application to read it, causing the application to crash or become unresponsive. |
| CVE-2019-25624 | Medium | 2026-03-23 | Not applicable | Proof of concept only | Liquid Studio 2.17 contains a denial of service vulnerability that allows local attackers to crash the application by providing malformed input through the keyboard interface. Attackers can trigger the vulnerability by entering arbitrary characters during application runtime, causing the application to become unresponsive or terminate abnormally. |
| CVE-2019-25623 | Medium | 2026-03-23 | Not applicable | Proof of concept only | Luminance Studio 2.17 contains a denial of service vulnerability that allows local attackers to crash the application by providing malformed input through the keyboard interface. Attackers can create a text file with arbitrary character sequences and trigger the application to process the input, causing the application to become unresponsive or terminate abnormally. |
| CVE-2019-25621 | Medium | 2026-03-23 | Not applicable | Proof of concept only | Pixel Studio 2.17 contains a denial of service vulnerability that allows local attackers to crash the application by providing malformed input through the keyboard interface. Attackers can trigger the vulnerability by entering arbitrary characters, causing the application to become unresponsive or terminate abnormally. |
| CVE-2019-25620 | Medium | 2026-03-23 | Not applicable | Proof of concept only | Tree Studio 2.17 contains a denial of service vulnerability that allows local attackers to crash the application by providing malformed input through the keyboard interface. Attackers can trigger the vulnerability by entering arbitrary characters during application runtime, causing the application to become unresponsive or terminate abnormally. |
| CVE-2019-25567 | Medium | 2026-03-21 | Not applicable | Proof of concept only | Valentina Studio 9.0.5 Linux contains a buffer overflow vulnerability in the Host field of the connection dialog that allows local attackers to crash the application by supplying an oversized input string. Attackers can trigger the vulnerability by pasting a crafted buffer exceeding 264 bytes into the Host field during server connection attempts, causing a denial of service. |
| CVE-2019-25557 | Medium | 2026-03-21 | Not applicable | Proof of concept only | TwistedBrush Pro Studio 24.06 contains a denial of service vulnerability that allows local attackers to crash the application by importing a malformed .srp script file. Attackers can create a .srp file containing an excessively large buffer and import it through the Script Player interface to trigger an application crash. |
| CVE-2019-25556 | Medium | 2026-03-21 | Not applicable | Proof of concept only | TwistedBrush Pro Studio 24.06 contains a denial of service vulnerability in the Resize Image function that allows local attackers to crash the application by supplying an excessively long buffer. Attackers can paste a malicious string into the New Width or New Height field to trigger a buffer overflow that causes the application to crash. |
| CVE-2019-25555 | Medium | 2026-03-21 | Not applicable | Proof of concept only | TwistedBrush Pro Studio 24.06 contains a denial of service vulnerability in the Script Recorder component that allows local attackers to crash the application by supplying an excessively large buffer. Attackers can paste a malicious string containing 500,000 characters into the Description field of the Script Recorder dialog to trigger an application crash. |
| CVE-2026-32638 | Low | 2026-03-18 | Not applicable | Proof of concept only | StudioCMS is a server-side-rendered, Astro native, headless content management system. Prior to 0.4.4, the REST API `getUsers` endpoint in StudioCMS uses the attacker-controlled `rank` query parameter to decide whether owner accounts should be filtered from the result set. As a result, an admin token can request `rank=owner` and receive owner account records, including IDs, usernames, display names, and email addresses, even though the adjacent `getUser` endpoint correctly blocks admins from viewing owner users. This is an authorization inconsistency inside the same user-management surface. Version 0.4.4 fixes the issue. |
| CVE-2026-32106 | High | 2026-03-11 | Not applicable | Proof of concept only | StudioCMS is a server-side-rendered, Astro native, headless content management system. Prior to 0.4.3, the REST API createUser endpoint uses string-based rank checks that only block creating owner accounts, while the Dashboard API uses indexOf-based rank comparison that prevents creating users at or above your own rank. This inconsistency allows an admin to create additional admin accounts via the REST API, enabling privilege proliferation and persistence. This vulnerability is fixed in 0.4.3. |
| CVE-2026-32104 | Medium | 2026-03-11 | Not applicable | Proof of concept only | StudioCMS is a server-side-rendered, Astro native, headless content management system. Prior to 0.4.3, the updateUserNotifications endpoint accepts a user ID from the request payload and uses it to update that user's notification preferences. It checks that the caller is logged in but never verifies that the caller owns the target account (id !== userData.user.id). Any authenticated visitor can modify notification preferences for any user, including disabling admin notifications to suppress detection of malicious activity. This vulnerability is fixed in 0.4.3. |
| CVE-2026-32103 | High | 2026-03-11 | Not applicable | Proof of concept only | StudioCMS is a server-side-rendered, Astro native, headless content management system. Prior to 0.4.3, the POST /studiocms_api/dashboard/create-reset-link endpoint allows any authenticated user with admin privileges to generate a password reset token for any other user, including the owner account. The handler verifies that the caller is an admin but does not enforce role hierarchy, nor does it validate that the target userId matches the caller's identity. Combined with the POST /studiocms_api/dashboard/reset-password endpoint, this allows a complete account takeover of the highest-privileged account in the system. This vulnerability is fixed in 0.4.3. |
| CVE-2026-32101 | High | 2026-03-11 | Not applicable | Proof of concept only | StudioCMS is a server-side-rendered, Astro native, headless content management system. Prior to 0.3.1, the S3 storage manager's isAuthorized() function is declared async (returns Promise<boolean>) but is called without await in both the POST and PUT handlers. Since a Promise object is always truthy in JavaScript, !isAuthorized(type) always evaluates to false, completely bypassing the authorization check. Any authenticated user with the lowest visitor role can upload, delete, rename, and list all files in the S3 bucket. This vulnerability is fixed in 0.3.1. |
| CVE-2026-30944 | High | 2026-03-10 | Not applicable | Proof of concept only | StudioCMS is a server-side-rendered, Astro native, headless content management system. Prior to 0.4.0, the /studiocms_api/dashboard/api-tokens endpoint allows any authenticated user (at least Editor) to generate API tokens for any other user, including owner and admin accounts. The endpoint fails to validate whether the requesting user is authorized to create tokens on behalf of the target user ID, resulting in a full privilege escalation. This vulnerability is fixed in 0.4.0. |
| CVE-2020-37162 | High | 2026-02-07 | Not applicable | Proof of concept only | Wedding Slideshow Studio 1.36 contains a buffer overflow vulnerability in the registration key input that allows attackers to execute arbitrary code by overwriting memory. Attackers can craft a malicious payload of 1608 bytes to trigger a stack-based buffer overflow and execute commands through the registration key field. |
| CVE-2020-37161 | High | 2026-02-07 | Not applicable | Proof of concept only | Wedding Slideshow Studio 1.36 contains a buffer overflow vulnerability that allows attackers to execute arbitrary code by overwriting the registration name field with malicious payload. Attackers can craft a specially designed payload to trigger remote code execution, demonstrating the ability to run system commands like launching the calculator. |
| CVE-2026-24134 | Medium | 2026-01-28 | Not applicable | Proof of concept only | StudioCMS is a server-side-rendered, Astro native, headless content management system. Versions prior to 0.2.0 contain a Broken Object Level Authorization (BOLA) vulnerability in the Content Management feature that allows users with the "Visitor" role to access draft content created by Editor/Admin/Owner users. Version 0.2.0 patches the issue. |
| CVE-2026-22033 | High | 2026-01-12 | Not applicable | Proof of concept only | Label Studio is a multi-type data labeling and annotation tool. In 1.22.0 and earlier, a persistent stored cross-site scripting (XSS) vulnerability exists in the custom_hotkeys functionality of the application. An authenticated attacker (or one who can trick a user/administrator into updating their custom_hotkeys) can inject JavaScript code that executes in other users’ browsers when those users load any page using the templates/base.html template. Because the application exposes an API token endpoint (/api/current-user/token) to the browser and lacks robust CSRF protection on some API endpoints, the injected script may fetch the victim’s API token or call token reset endpoints — enabling full account takeover and unauthorized API access. |
| CVE-2025-61929 | Critical | 2025-10-10 | Not applicable | Proof of concept only | Cherry Studio is a desktop client that supports for multiple LLM providers. Cherry Studio registers a custom protocol called `cherrystudio://`. When handling the MCP installation URL, it parses the base64-encoded configuration data and directly executes the command within it. In the files `src/main/services/ProtocolClient.ts` and `src/main/services/urlschema/mcp-install.ts`, when receiving a URL of the `cherrystudio://mcp` type, the `handleMcpProtocolUrl` function is called for processing. If an attacker crafts malicious content and posts it on a website or elsewhere (there are many exploitation methods, such as creating a malicious website with a button containing this malicious content), when the user clicks it, since the pop-up window contains normal content, the direct click is considered a scene action, and the malicious command is directly triggered, leading to the user being compromised. As of time of publication, no known patched versions exist. |
| CVE-2025-54382 | Critical | 2025-08-13 | Not applicable | Proof of concept only | Cherry Studio is a desktop client that supports for multiple LLM providers. In version 1.5.1, a remote code execution (RCE) vulnerability exists in the Cherry Studio platform when connecting to streamableHttp MCP servers. The issue arises from the server’s implicit trust in the oauth auth redirection endpoints and failure to properly sanitize the URL. This issue has been patched in version 1.5.2. |
| CVE-2025-54074 | High | 2025-08-13 | Not applicable | Proof of concept only | Cherry Studio is a desktop client that supports for multiple LLM providers. From versions 1.2.5 to 1.5.1, Cherry Studio is vulnerable to OS Command Injection during a connection with a malicious MCP server in HTTP Streamable mode. Attackers can setup a malicious MCP server with compatible OAuth authorization server endpoints and trick victims into connecting it, leading to OS command injection in vulnerable clients. This issue has been patched in version 1.5.2. |
| CVE-2025-54063 | Critical | 2025-08-11 | Not applicable | Proof of concept only | Cherry Studio is a desktop client that supports for multiple LLM providers. From versions 1.4.8 to 1.5.0, there is a one-click remote code execution vulnerability through the custom URL handling. An attacker can exploit this by hosting a malicious website or embedding a specially crafted URL on any website. If a victim clicks the exploit link in their browser, the app’s custom URL handler is triggered, leading to remote code execution on the victim’s machine. This issue has been patched in version 1.5.1. |
| CVE-2024-6712 | Medium | 2025-05-15 | Not applicable | Proof of concept only | The MapFig Studio WordPress plugin through 0.2.1 does not have CSRF check in some places, and is missing sanitisation as well as escaping, which could allow attackers to make logged in admin add Stored XSS payloads via a CSRF attack |
| CVE-2025-25297 | High | 2025-02-14 | Not applicable | Proof of concept only | Label Studio is an open source data labeling tool. Prior to version 1.16.0, Label Studio's S3 storage integration feature contains a Server-Side Request Forgery (SSRF) vulnerability in its endpoint configuration. When creating an S3 storage connection, the application allows users to specify a custom S3 endpoint URL via the s3_endpoint parameter. This endpoint URL is passed directly to the boto3 AWS SDK without proper validation or restrictions on the protocol or destination. The vulnerability allows an attacker to make the application send HTTP requests to arbitrary internal services by specifying them as the S3 endpoint. When the storage sync operation is triggered, the application attempts to make S3 API calls to the specified endpoint, effectively making HTTP requests to the target service and returning the response in error messages. This SSRF vulnerability enables attackers to bypass network segmentation and access internal services that should not be accessible from the external network. The vulnerability is particularly severe because error messages from failed requests contain the full response body, allowing data exfiltration from internal services. Version 1.16.0 contains a patch for the issue. |
| CVE-2024-30052 | Medium | 2024-06-11 | Not applicable | Proof of concept only | Visual Studio Remote Code Execution Vulnerability |
| CVE-2024-28938 | High | 2024-04-09 | Not applicable | Proof of concept only | Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability |
| CVE-2024-21392 | High | 2024-03-12 | Not applicable | Proof of concept only | .NET and Visual Studio Denial of Service Vulnerability |
| CVE-2024-26152 | Medium | 2024-02-22 | Not applicable | Proof of concept only | ### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 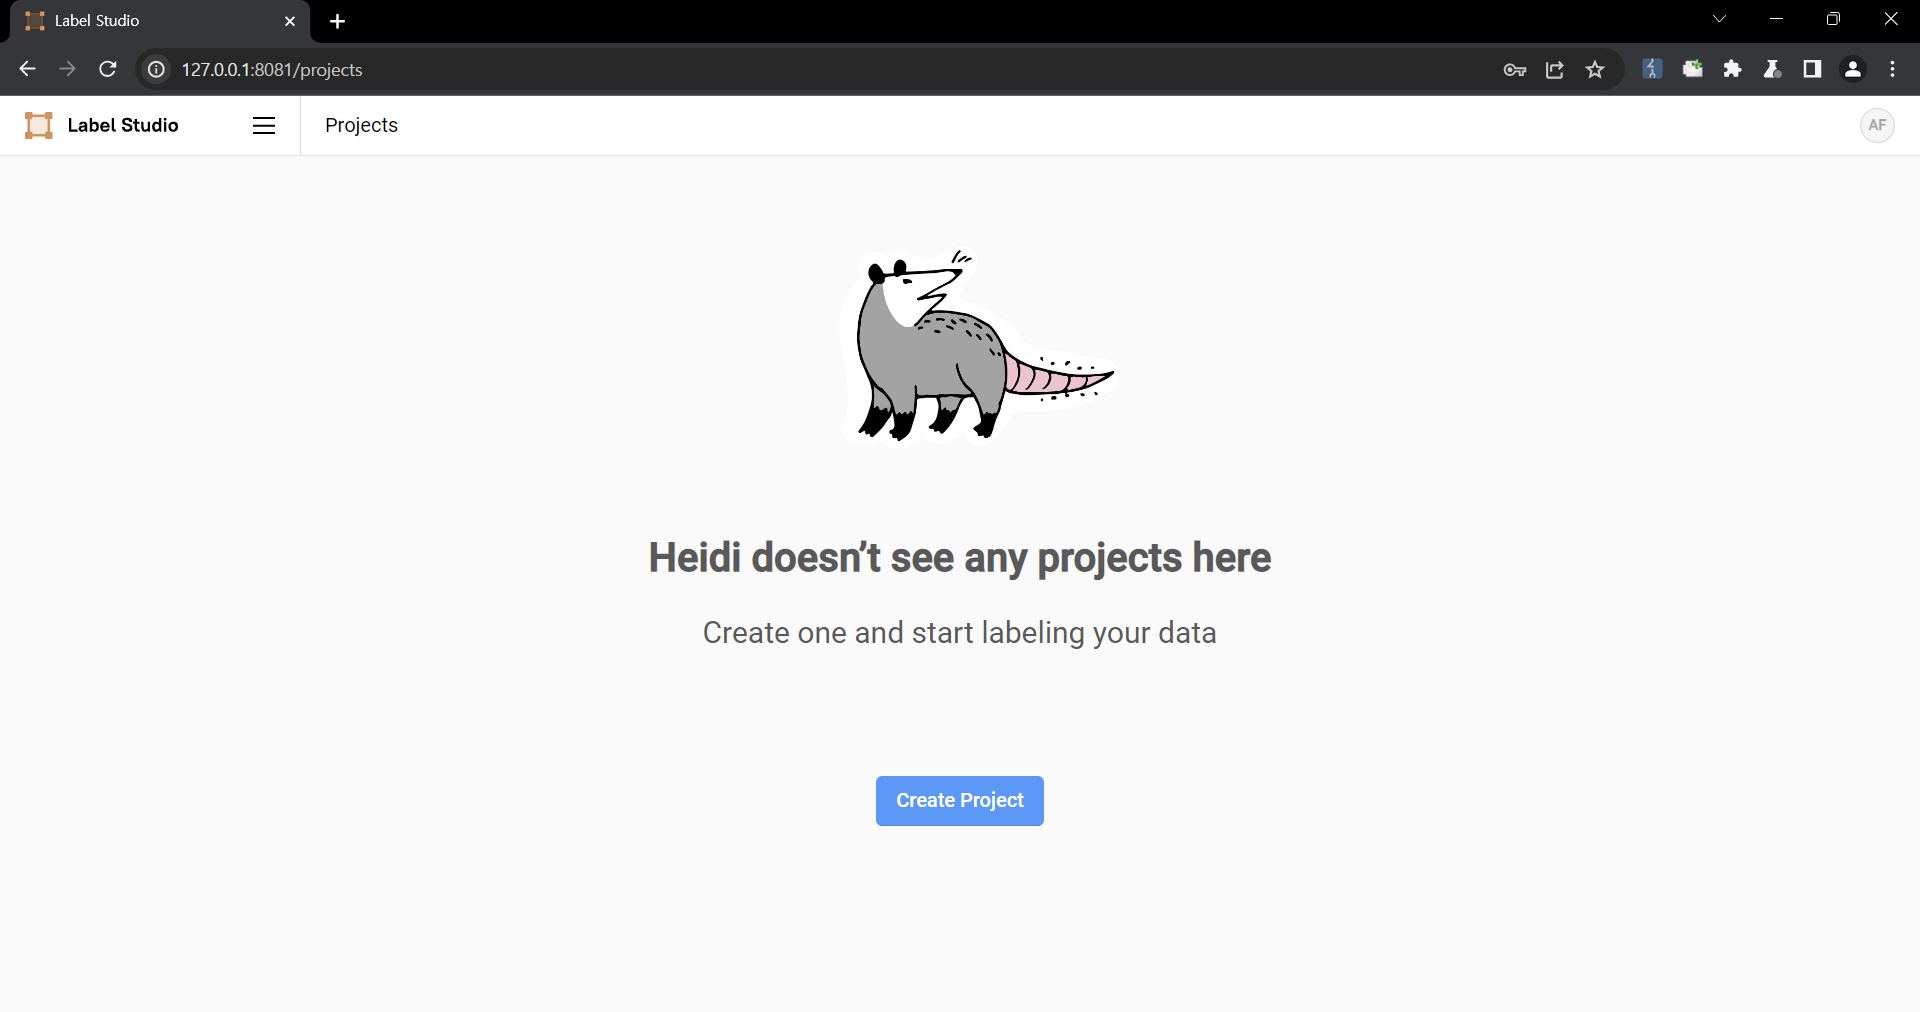 2. Upload a file containing the payload using the "Upload Files" function. 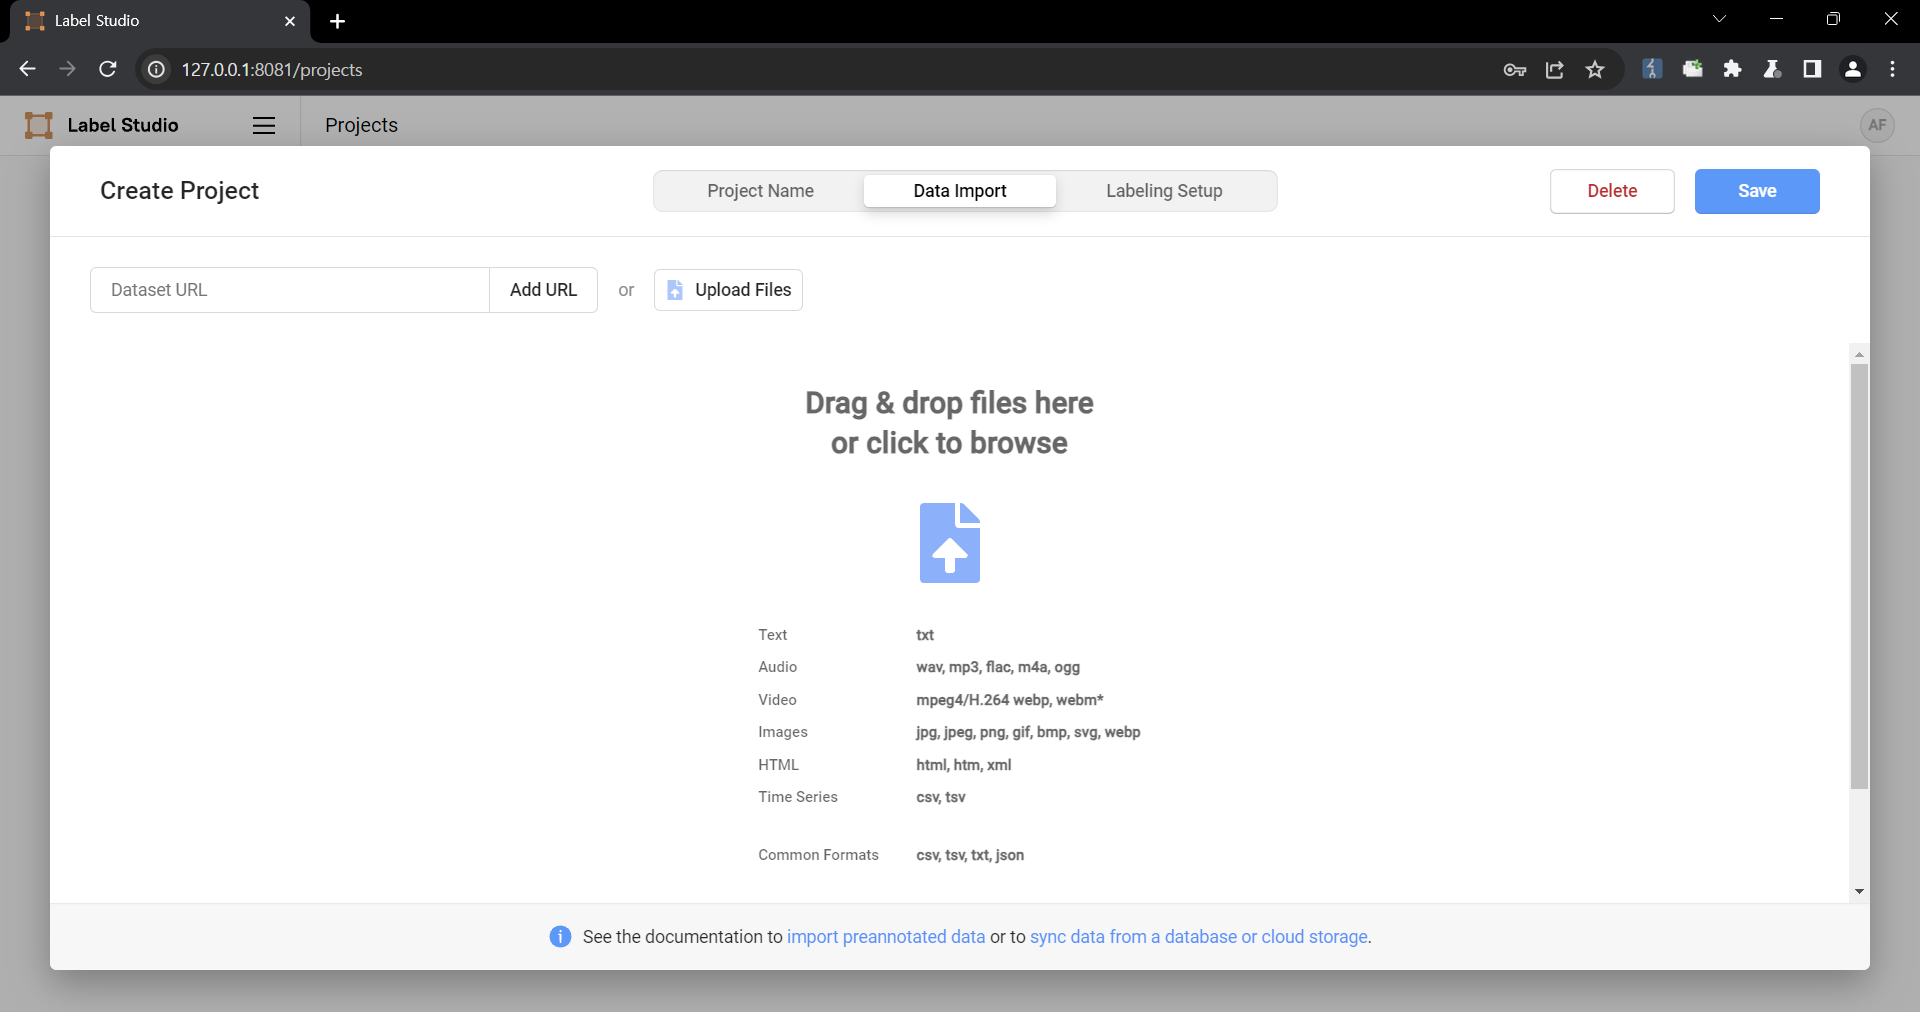 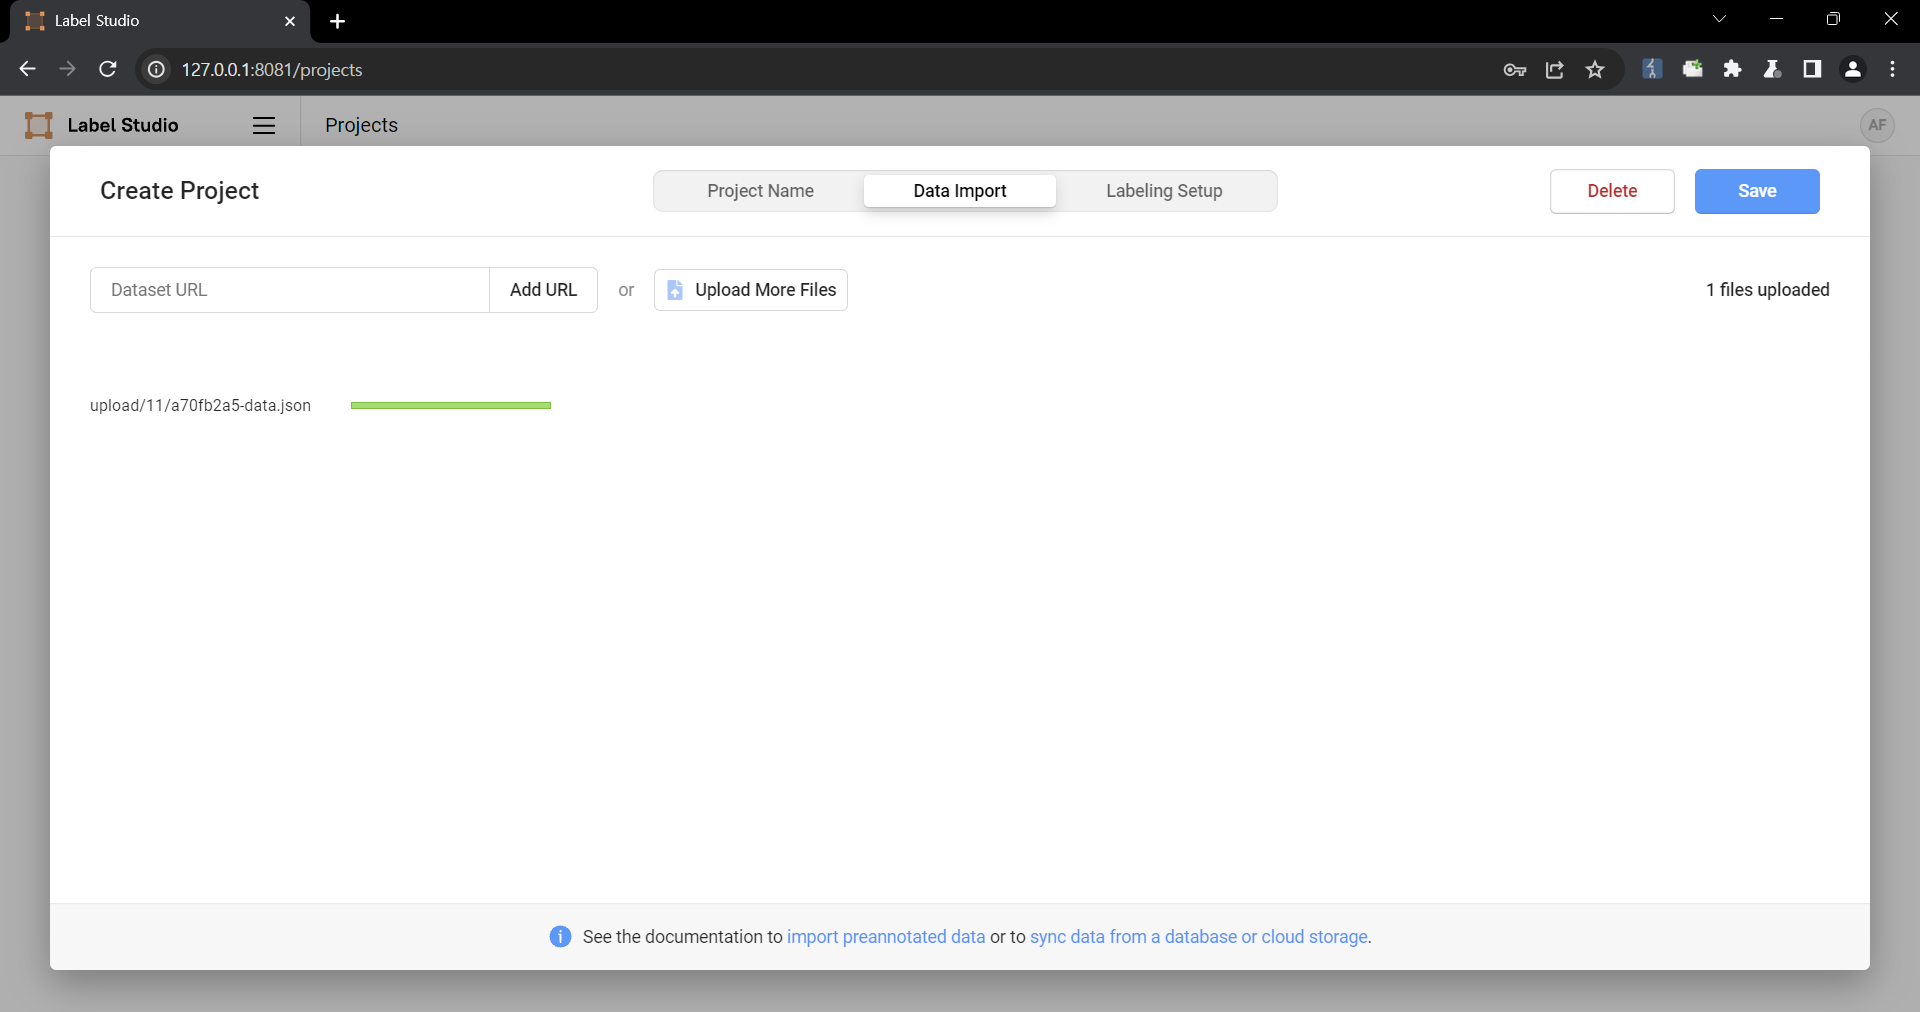 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 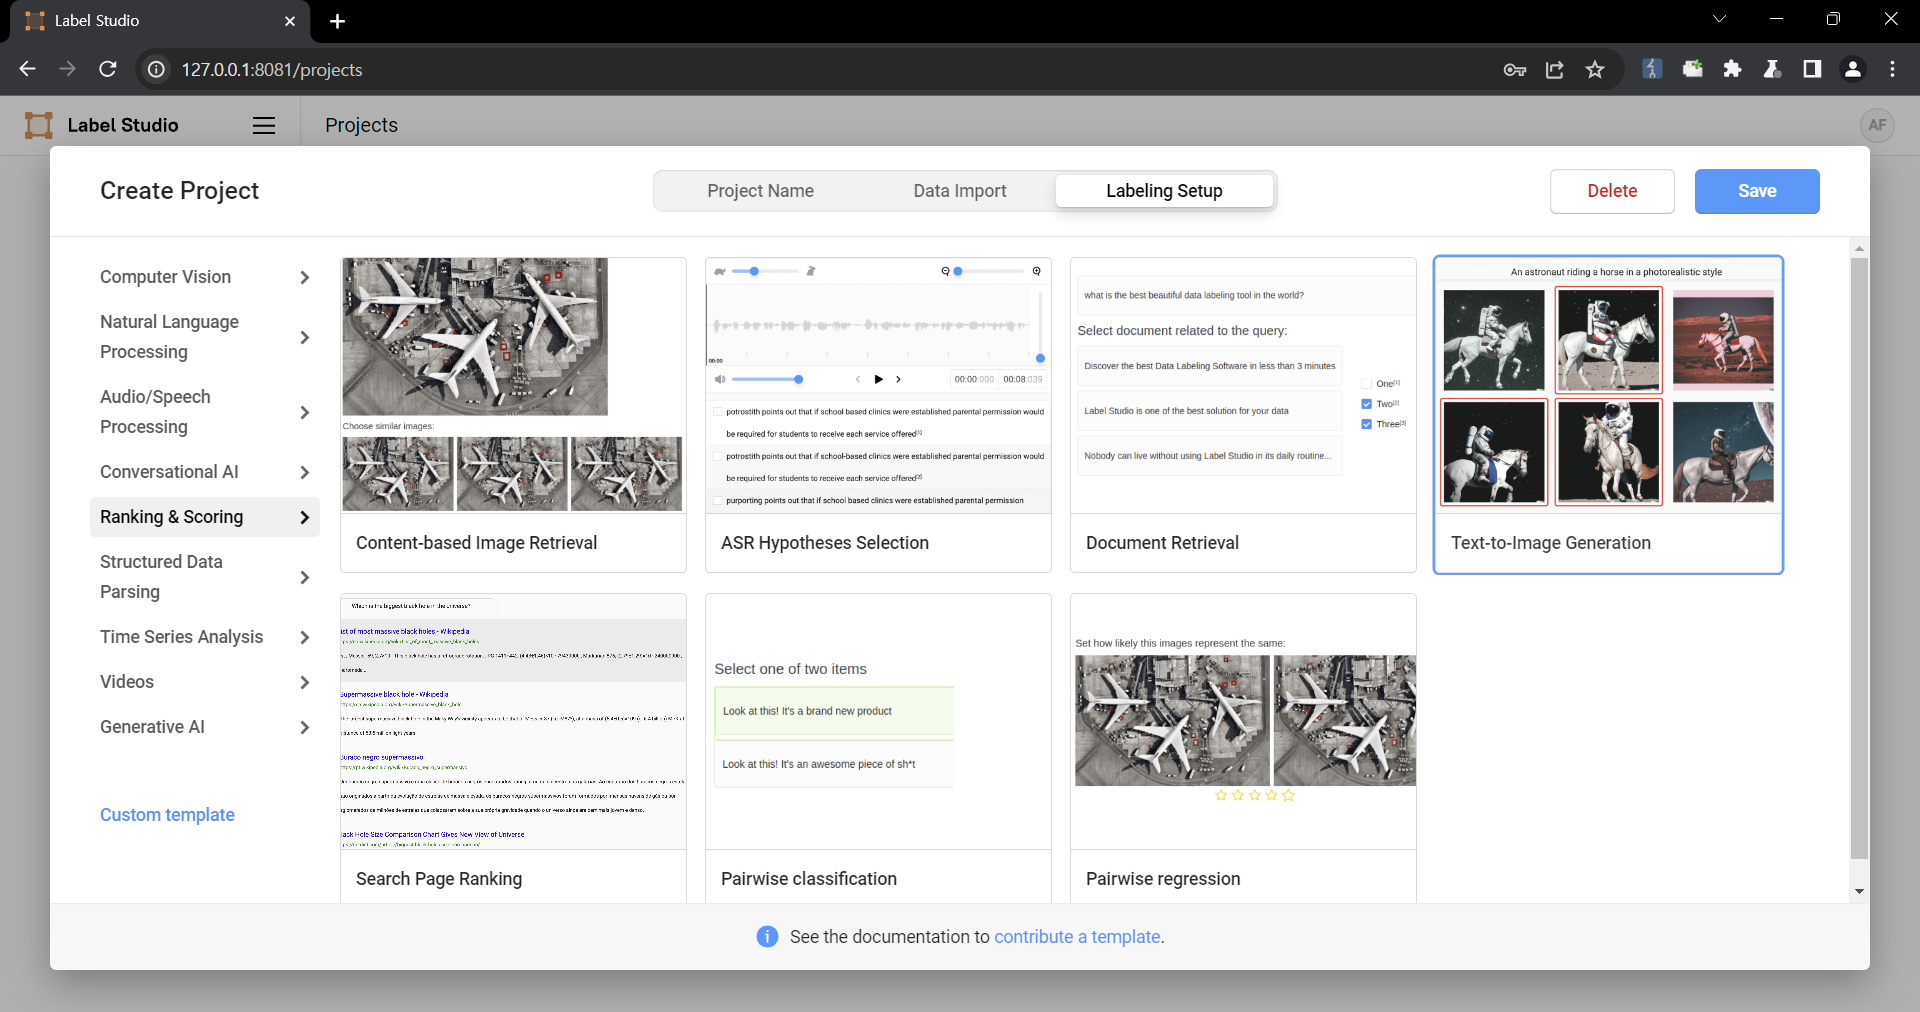 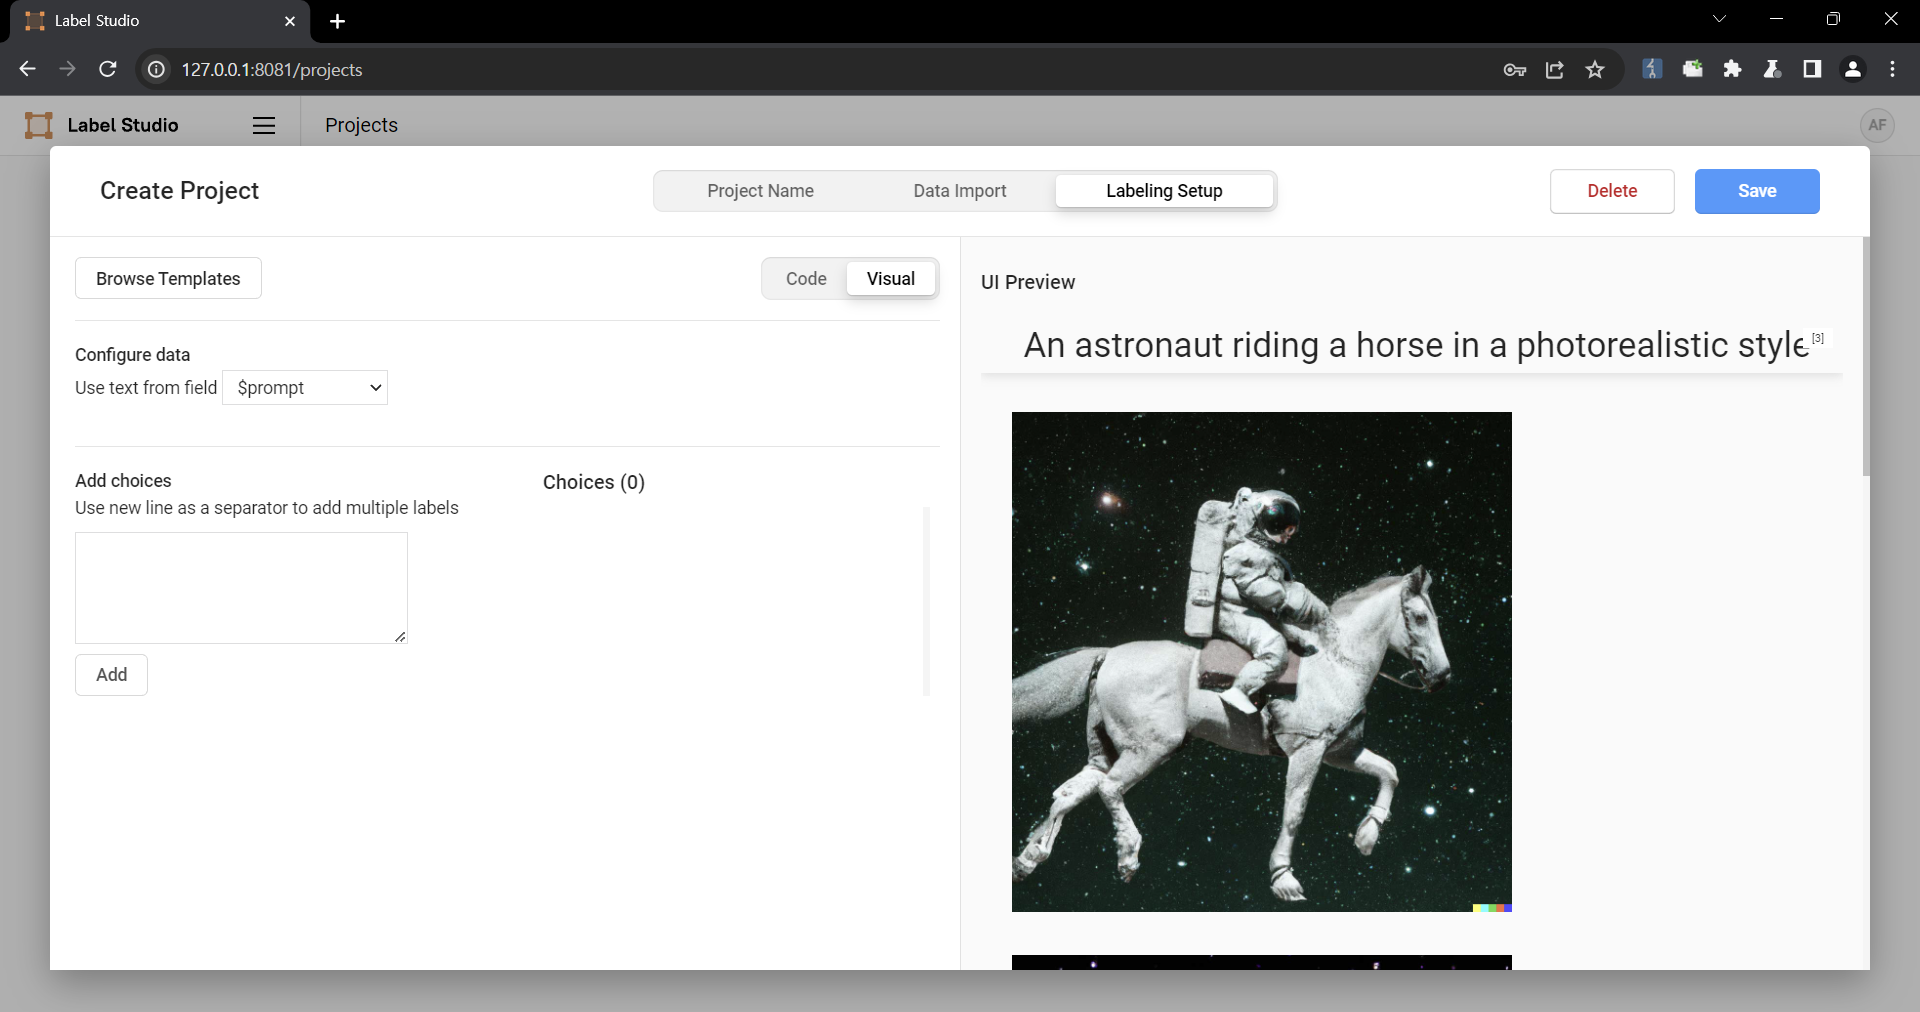 4. Select a task 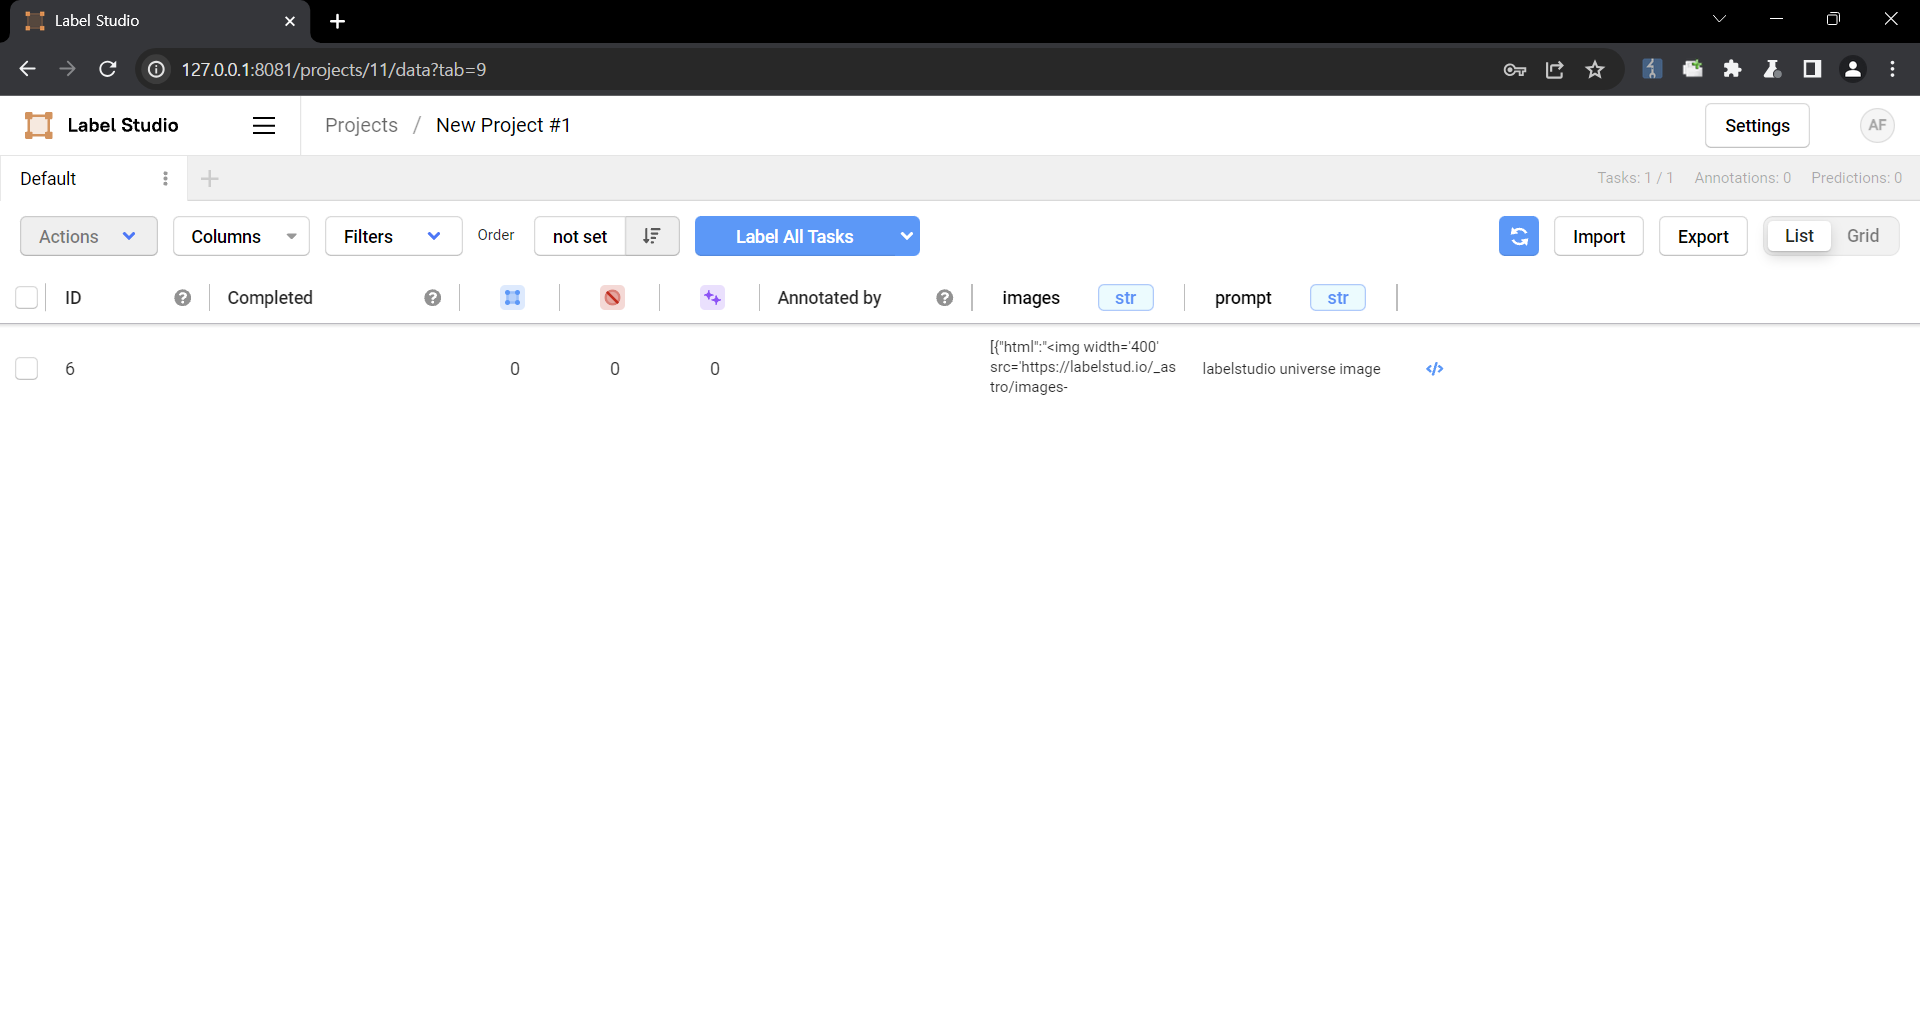 5. Check that the script is running 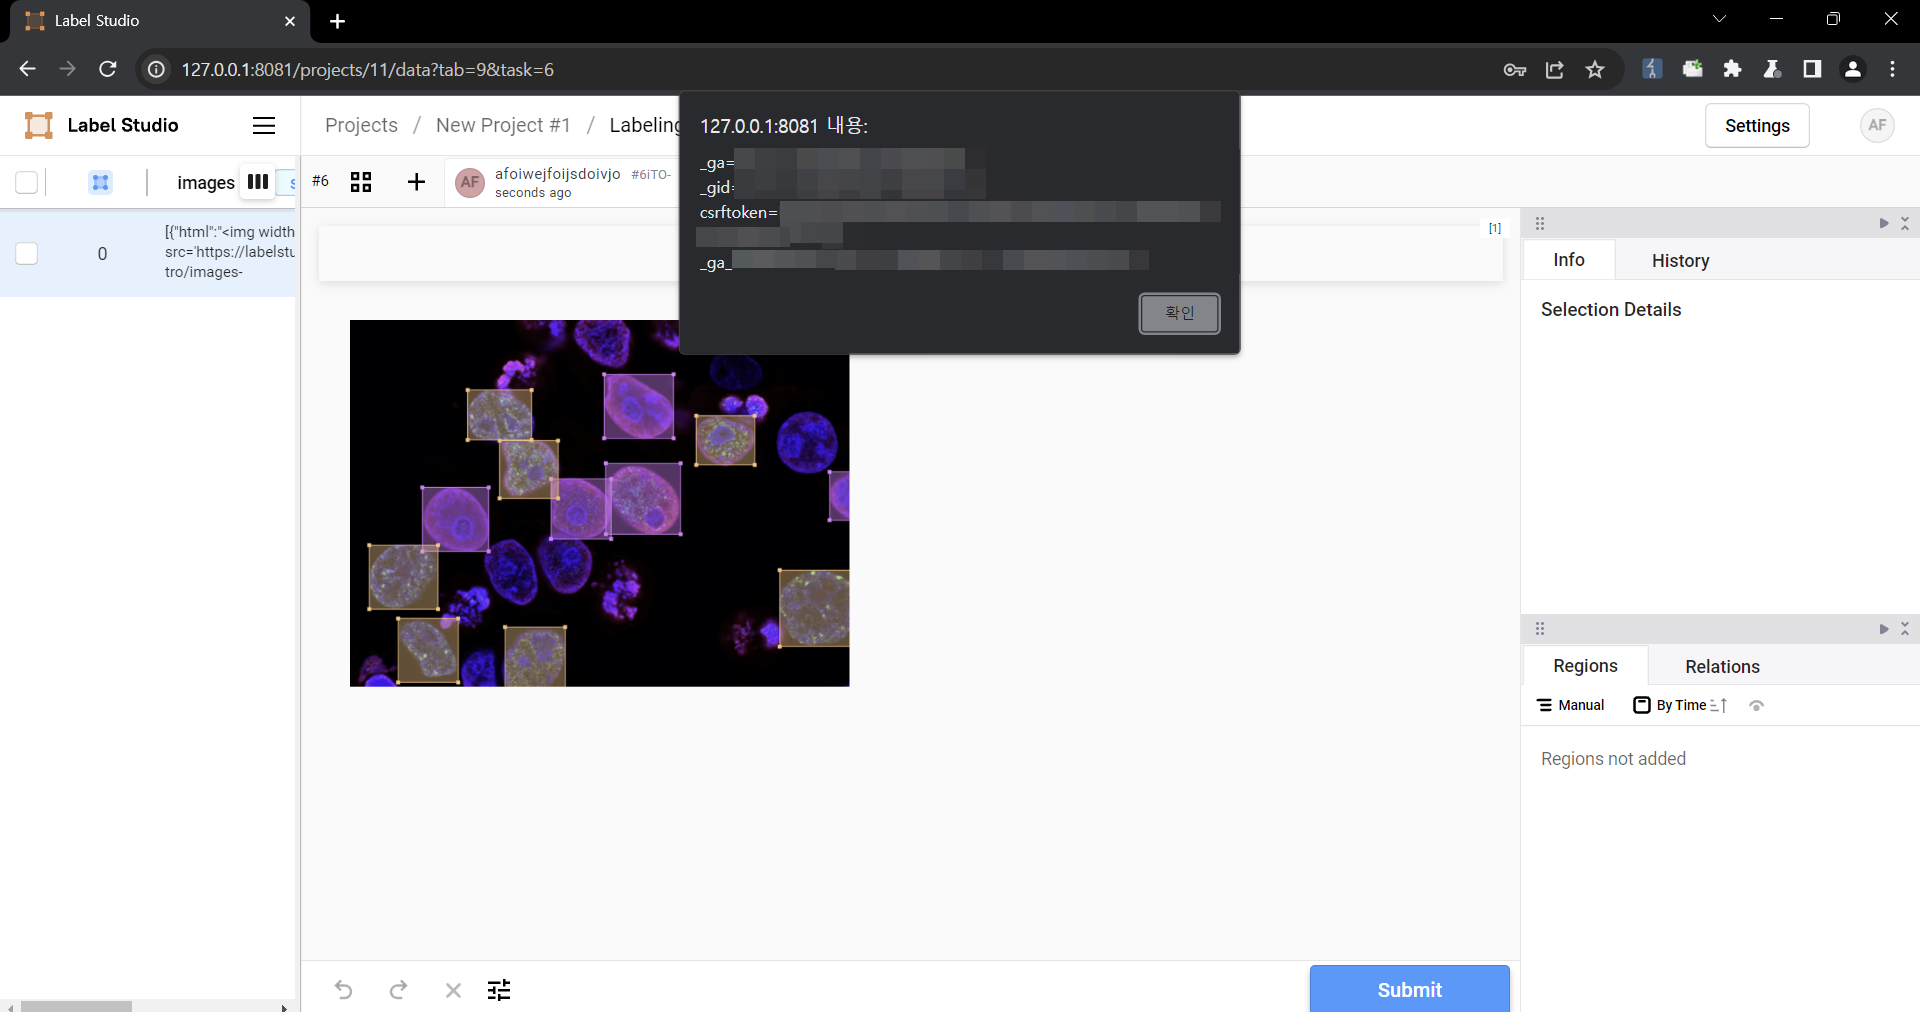 ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering. |
| CVE-2024-21404 | High | 2024-02-13 | Not applicable | Proof of concept only | .NET Denial of Service Vulnerability |
| CVE-2023-47116 | Medium | 2024-01-31 | Not applicable | Proof of concept only | Label Studio is a popular open source data labeling tool. The vulnerability affects all versions of Label Studio prior to 1.11.0 and was tested on version 1.8.2. Label Studio's SSRF protections that can be enabled by setting the `SSRF_PROTECTION_ENABLED` environment variable can be bypassed to access internal web servers. This is because the current SSRF validation is done by executing a single DNS lookup to verify that the IP address is not in an excluded subnet range. This protection can be bypassed by either using HTTP redirection or performing a DNS rebinding attack. |
| CVE-2024-23633 | Medium | 2024-01-24 | Not applicable | Proof of concept only | Label Studio, an open source data labeling tool had a remote import feature allowed users to import data from a remote web source, that was downloaded and could be viewed on the website. Prior to version 1.10.1, this feature could had been abused to download a HTML file that executed malicious JavaScript code in the context of the Label Studio website. Executing arbitrary JavaScript could result in an attacker performing malicious actions on Label Studio users if they visit the crafted avatar image. For an example, an attacker can craft a JavaScript payload that adds a new Django Super Administrator user if a Django administrator visits the image. `data_import/uploader.py` lines 125C5 through 146 showed that if a URL passed the server side request forgery verification checks, the contents of the file would be downloaded using the filename in the URL. The downloaded file path could then be retrieved by sending a request to `/api/projects/{project_id}/file-uploads?ids=[{download_id}]` where `{project_id}` was the ID of the project and `{download_id}` was the ID of the downloaded file. Once the downloaded file path was retrieved by the previous API endpoint, `data_import/api.py`lines 595C1 through 616C62 demonstrated that the `Content-Type` of the response was determined by the file extension, since `mimetypes.guess_type` guesses the `Content-Type` based on the file extension. Since the `Content-Type` was determined by the file extension of the downloaded file, an attacker could import in a `.html` file that would execute JavaScript when visited. Version 1.10.1 contains a patch for this issue. Other remediation strategies are also available. For all user provided files that are downloaded by Label Studio, set the `Content-Security-Policy: sandbox;` response header when viewed on the site. The `sandbox` directive restricts a page's actions to prevent popups, execution of plugins and scripts and enforces a `same-origin` policy. Alternatively, restrict the allowed file extensions that may be downloaded. |
| CVE-2024-20656 | High | 2024-01-09 | Not applicable | Proof of concept only | Visual Studio Elevation of Privilege Vulnerability |
| CVE-2023-41613 | High | 2023-12-04 | Not applicable | Proof of concept only | EzViz Studio v2.2.0 is vulnerable to DLL hijacking. |
| CVE-2023-36558 | Medium | 2023-11-14 | Not applicable | Proof of concept only | ASP.NET Core Security Feature Bypass Vulnerability |
| CVE-2023-36038 | High | 2023-11-14 | Not applicable | Proof of concept only | ASP.NET Core Denial of Service Vulnerability |
| CVE-2023-43791 | Critical | 2023-11-09 | Not applicable | Proof of concept only | Label Studio is a multi-type data labeling and annotation tool with standardized output format. There is a vulnerability that can be chained within the ORM Leak vulnerability to impersonate any account on Label Studio. An attacker could exploit these vulnerabilities to escalate their privileges from a low privilege user to a Django Super Administrator user. The vulnerability was found to affect versions before `1.8.2`, where a patch was introduced. |
| CVE-2023-39967 | Critical | 2023-09-06 | Not applicable | Proof of concept only | WireMock is a tool for mocking HTTP services. When certain request URLs like “@127.0.0.1:1234" are used in WireMock Studio configuration fields, the request might be forwarded to an arbitrary service reachable from WireMock’s instance. There are 3 identified potential attack vectors: via “TestRequester” functionality, webhooks and the proxy mode. As we can control HTTP Method, HTTP Headers, HTTP Data, it allows sending requests with the default level of credentials for the WireMock instance. The vendor has discontinued the affected Wiremock studio product and there will be no fix. Users are advised to find alternatives. |
| CVE-2023-36088 | High | 2023-09-01 | Not applicable | Proof of concept only | Server Side Request Forgery (SSRF) vulnerability in NebulaGraph Studio version 3.7.0, allows remote attackers to gain sensitive information. |
| CVE-2023-38335 | Medium | 2023-07-20 | Not applicable | Proof of concept only | Omnis Studio 10.22.00 has incorrect access control. It advertises a feature for making Omnis libraries "always private" - this is supposed to be an irreversible operation. However, due to implementation issues, "always private" Omnis libraries can be opened by the Omnis Studio browser by bypassing specific checks. This violates the expected behavior of an "irreversible operation". |
| CVE-2023-38334 | Medium | 2023-07-20 | Not applicable | Proof of concept only | Omnis Studio 10.22.00 has incorrect access control. It advertises an irreversible feature for locking classes within Omnis libraries: it should be no longer possible to delete, view, change, copy, rename, duplicate, or print a locked class. Due to implementation issues, locked classes in Omnis libraries can be unlocked, and thus further analyzed and modified by Omnis Studio. This allows for further analyzing and also deleting, viewing, changing, copying, renaming, duplicating, or printing previously locked Omnis classes. This violates the expected behavior of an "irreversible operation." |
| CVE-2023-32032 | Medium | 2023-06-14 | Not applicable | Proof of concept only | .NET and Visual Studio Elevation of Privilege Vulnerability |
| CVE-2023-29338 | Medium | 2023-05-09 | Not applicable | Proof of concept only | Visual Studio Code Spoofing Vulnerability |
| CVE-2023-0500 | Medium | 2023-03-27 | Not applicable | Proof of concept only | The WP Film Studio WordPress plugin before 1.3.5 does not have CSRF check when activating plugins, which could allow attackers to make logged in admins activate arbitrary plugins present on the blog via a CSRF attack |
| CVE-2023-24045 | Medium | 2023-03-01 | Not applicable | Proof of concept only | In Dataiku DSS 11.2.1, an attacker can download other Dataiku files that were uploaded to the myfiles section by specifying the target username in a download request. |
| CVE-2022-43143 | Critical | 2022-11-21 | Not applicable | Proof of concept only | A cross-site scripting (XSS) vulnerability in Beekeeper Studio v3.6.6 allows attackers to execute arbitrary web scripts or HTML via a crafted payload injected into the error modal container. |
| CVE-2022-35825 | High | 2022-08-09 | Not applicable | Proof of concept only | Visual Studio Remote Code Execution Vulnerability |
| CVE-2022-22978 | Critical | 2022-05-19 | Mitigation candidate | Proof of concept only | In spring security versions prior to 5.4.11+, 5.5.7+ , 5.6.4+ and older unsupported versions, RegexRequestMatcher can easily be misconfigured to be bypassed on some servlet containers. Applications using RegexRequestMatcher with `.` in the regular expression are possibly vulnerable to an authorization bypass. |
| CVE-2022-24823 | Medium | 2022-05-06 | No exploit published | Proof of concept only | Netty is an open-source, asynchronous event-driven network application framework. The package `io.netty:netty-codec-http` prior to version 4.1.77.Final contains an insufficient fix for CVE-2021-21290. When Netty's multipart decoders are used local information disclosure can occur via the local system temporary directory if temporary storing uploads on the disk is enabled. This only impacts applications running on Java version 6 and lower. Additionally, this vulnerability impacts code running on Unix-like systems, and very old versions of Mac OSX and Windows as they all share the system temporary directory between all users. Version 4.1.77.Final contains a patch for this vulnerability. As a workaround, specify one's own `java.io.tmpdir` when starting the JVM or use DefaultHttpDataFactory.setBaseDir(...) to set the directory to something that is only readable by the current user. |
| CVE-2021-43908 | Medium | 2021-12-15 | Not applicable | Proof of concept only | Visual Studio Code Spoofing Vulnerability |
| CVE-2019-17571 | Critical | 2019-12-20 | Protected by Waratek | Proof of concept only | Included in Log4j 1.2 is a SocketServer class that is vulnerable to deserialization of untrusted data which can be exploited to remotely execute arbitrary code when combined with a deserialization gadget when listening to untrusted network traffic for log data. This affects Log4j versions up to 1.2 up to 1.2.17. |