
Java SE CPU Mar 2010
Released March 2010 · Oracle's advisory ↗ · ← Critical Patch Update, January 2010 · Critical Patch Update, April 2010 →
27 CVEs in this release, one square each
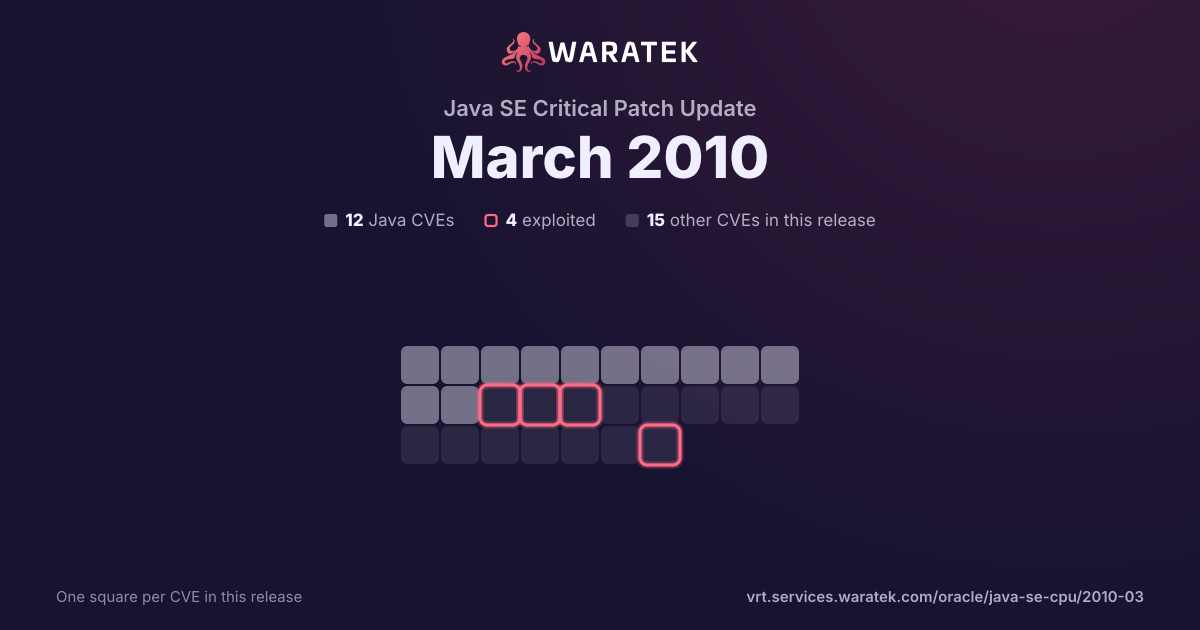
By status
1Mitigation candidate11No exploit published14Outside Waratek scope1Not applicable
4Exploited, marked by the ring
No exploit published. For 7 of them, Oracle's security advisory is the source of public detail.
Overview 5 matches · 1 in Waratek scope · 0 protected · 4 exploited · 1 CISA KEV · 4 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
1
20.0%
No exploit published
0
0.0%
Outside Waratek scope
3
60.0%
Not applicable
1
20.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
5
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
4
80.0%
Working exploit published
1
20.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 4 / month
Nov 09Dec 09Jan 10Feb 10Mar 10Apr 10
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2010-0842 | High | 2010-04-01 | Outside Waratek scope | Exploited | Unspecified vulnerability in the Sound component in Oracle Java SE and Java for Business 6 Update 18, 5.0 Update 23, 1.4.2_25, and 1.3.1_27 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the March 2010 CPU. Oracle has not commented on claims from a reliable researcher that this is an uncontrolled array index that allows remote attackers to execute arbitrary code via a MIDI file with a crafted MixerSequencer object, related to the GM_Song structure. |
| CVE-2010-0840 | Critical | 2010-04-01 | Outside Waratek scope | Exploited | Unspecified vulnerability in the Java Runtime Environment component in Oracle Java SE and Java for Business 6 Update 18, 5.0 Update 23, and 1.4.2_25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the March 2010 CPU. Oracle has not commented on claims from a reliable researcher that this is related to improper checks when executing privileged methods in the Java Runtime Environment (JRE), which allows attackers to execute arbitrary code via (1) an untrusted object that extends the trusted class but has not modified a certain method, or (2) "a similar trust issue with interfaces," aka "Trusted Methods Chaining Remote Code Execution Vulnerability." |
| CVE-2010-0838 | High | 2010-04-01 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Java 2D component in Oracle Java SE and Java for Business 6 Update 18, 5.0, Update, and 23 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the March 2010 CPU. Oracle has not commented on claims from a reliable researcher that this is a stack-based buffer overflow using an untrusted size value in the readMabCurveData function in the CMM module in the JVM. |
| CVE-2010-0094 | High | 2010-04-01 | Outside Waratek scope | Exploited | Unspecified vulnerability in the Java Runtime Environment component in Oracle Java SE and Java for Business 6 Update 18 and 5.0 Update 23 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the March 2010 CPU. Oracle has not commented on claims from a reliable researcher that this is due to missing privilege checks during deserialization of RMIConnectionImpl objects, which allows remote attackers to call system-level Java functions via the ClassLoader of a constructor that is being deserialized. |
| CVE-2009-3555 | Critical | 2009-11-09 | Not applicable | Exploited | The TLS protocol, and the SSL protocol 3.0 and possibly earlier, as used in Microsoft Internet Information Services (IIS) 7.0, mod_ssl in the Apache HTTP Server 2.2.14 and earlier, OpenSSL before 0.9.8l, GnuTLS 2.8.5 and earlier, Mozilla Network Security Services (NSS) 3.12.4 and earlier, multiple Cisco products, and other products, does not properly associate renegotiation handshakes with an existing connection, which allows man-in-the-middle attackers to insert data into HTTPS sessions, and possibly other types of sessions protected by TLS or SSL, by sending an unauthenticated request that is processed retroactively by a server in a post-renegotiation context, related to a "plaintext injection" attack, aka the "Project Mogul" issue. |