
Oracle Critical Security Patch Update September 2026
Released September 2026 · Oracle's advisory ↗ · ← Security Patch Update, August 2026 · Critical Patch Update, October 2026 →
806 CVEs in this release, one square each
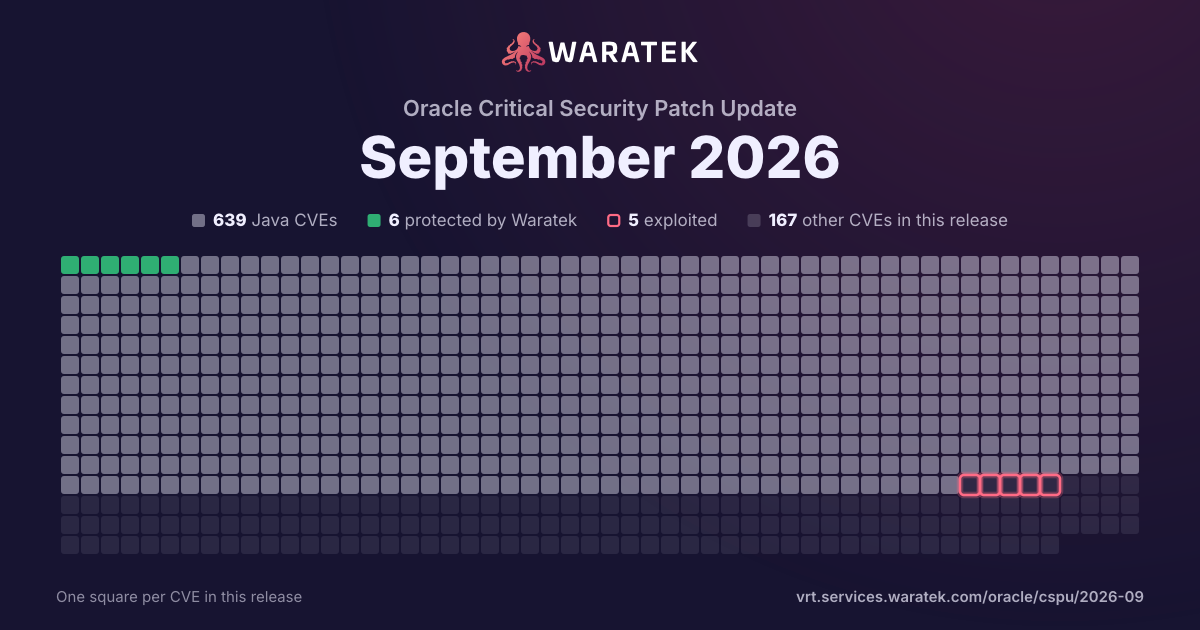
By status
No exploit published. For 596 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 39 matches · 1 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
1
2.6%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
38
97.4%
blocked by ARMR today
1
2.6%
partly blocked
0
0.0%
not blocked
38
97.4%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
39
100.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2026-87253 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM product of Oracle Supply Chain (component: Web Client). The supported version that is affected is 9.3.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Agile PLM. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Agile PLM, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Agile PLM accessible data as well as unauthorized read access to a subset of Oracle Agile PLM accessible data. CVSS 3.1 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2026-87252 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM product of Oracle Supply Chain (component: Application Server). The supported version that is affected is 9.3.6. Difficult to exploit vulnerability allows unauthenticated attacker with access to the physical communication segment attached to the hardware where the Oracle Agile PLM executes to compromise Oracle Agile PLM. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Agile PLM accessible data as well as unauthorized access to critical data or complete access to all Oracle Agile PLM accessible data. CVSS 3.1 Base Score 6.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:A/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-87248 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Hyperion Financial Management product of Oracle Hyperion (component: Security). The supported version that is affected is 11.2.26.0.000. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle Hyperion Financial Management executes to compromise Oracle Hyperion Financial Management. Successful attacks of this vulnerability can result in takeover of Oracle Hyperion Financial Management. CVSS 3.1 Base Score 6.7 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-87169 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Contract Lifecycle Management for Public Sector product of Oracle E-Business Suite (component: Wage Determination Online). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Contract Lifecycle Management for Public Sector. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Contract Lifecycle Management for Public Sector, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Contract Lifecycle Management for Public Sector accessible data as well as unauthorized read access to a subset of Oracle Contract Lifecycle Management for Public Sector accessible data. CVSS 3.1 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2026-83491 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle iRecruitment product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows unauthenticated attacker with access to the physical communication segment attached to the hardware where the Oracle iRecruitment executes to compromise Oracle iRecruitment. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle iRecruitment accessible data as well as unauthorized access to critical data or complete access to all Oracle iRecruitment accessible data. CVSS 3.1 Base Score 6.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:A/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-83488 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Helidon product of Oracle Fusion Middleware (component: helidon-microprofile-security). Supported versions that are affected are 4.0.0-4.5.4. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Helidon. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Helidon accessible data as well as unauthorized read access to a subset of Helidon accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-83480 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Helidon product of Oracle Fusion Middleware (component: WebSocket). Supported versions that are affected are 4.0.0-4.5.4. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Helidon. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Helidon. CVSS 3.1 Base Score 5.3 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-83460 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Helidon product of Oracle Fusion Middleware (component: LRA). Supported versions that are affected are 4.0.0-4.5.4. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Helidon. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Helidon accessible data as well as unauthorized read access to a subset of Helidon accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-83459 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Helidon product of Oracle Fusion Middleware (component: helidon-media-multipart). Supported versions that are affected are 3.0.0-3.2.20. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Helidon. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Helidon. CVSS 3.1 Base Score 5.3 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-83458 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Helidon product of Oracle Fusion Middleware (component: JSON). Supported versions that are affected are 4.0.0-4.5.4. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Helidon. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Helidon. CVSS 3.1 Base Score 5.3 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-83443 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Assets product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Assets. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Assets accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-83441 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Product Hub product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Product Hub. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Product Hub accessible data as well as unauthorized access to critical data or complete access to all Oracle Product Hub accessible data. CVSS 3.1 Base Score 6.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-83433 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Depot Repair product of Oracle E-Business Suite (component: Depot Repair Diagnostics). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Depot Repair. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Depot Repair accessible data as well as unauthorized access to critical data or complete access to all Oracle Depot Repair accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-83431 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Product Workbench product of Oracle E-Business Suite (component: WebUI). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Product Workbench. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Product Workbench, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Product Workbench accessible data as well as unauthorized read access to a subset of Oracle Product Workbench accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2026-83419 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Cloud Native Core Security Edge Protection Proxy product of Oracle Communications (component: SEPP). Supported versions that are affected are 26.1.200 and 25.2.201. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Communications Cloud Native Core Security Edge Protection Proxy. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Cloud Native Core Security Edge Protection Proxy accessible data as well as unauthorized read access to a subset of Oracle Communications Cloud Native Core Security Edge Protection Proxy accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-83416 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Coherence product of Oracle Fusion Middleware (component: Core). Supported versions that are affected are 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0 and 15.1.1.0.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Coherence. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Coherence. CVSS 3.1 Base Score 4.3 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-83354 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Coherence product of Oracle Fusion Middleware (component: Core). The supported version that is affected is 15.1.1.0.0. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Coherence. While the vulnerability is in Oracle Coherence, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Coherence accessible data. CVSS 3.1 Base Score 6.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:C/C:H/I:N/A:N). |
| CVE-2026-83346 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Fusion Middleware Control product of Oracle Fusion Middleware (component: Framework). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.0.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Fusion Middleware Control. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Fusion Middleware Control, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Fusion Middleware Control accessible data as well as unauthorized read access to a subset of Oracle Fusion Middleware Control accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2026-83279 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM MCAD Connector product of Oracle Supply Chain (component: CAX Client). The supported version that is affected is 3.6. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Agile PLM MCAD Connector executes to compromise Oracle Agile PLM MCAD Connector. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Agile PLM MCAD Connector accessible data. CVSS 3.1 Base Score 5.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-83278 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Helidon product of Oracle Fusion Middleware (component: helidon-integrations-neo4j). Supported versions that are affected are 3.0.0-3.2.20 and 4.0.0-4.5.4. Difficult to exploit vulnerability allows unauthenticated attacker with access to the physical communication segment attached to the hardware where the Helidon executes to compromise Helidon. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Helidon accessible data as well as unauthorized access to critical data or complete access to all Helidon accessible data. CVSS 3.1 Base Score 6.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:A/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-83274 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM MCAD Connector product of Oracle Supply Chain (component: CAX Client). The supported version that is affected is 3.6. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Agile PLM MCAD Connector executes to compromise Oracle Agile PLM MCAD Connector. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Agile PLM MCAD Connector accessible data. CVSS 3.1 Base Score 5.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-83251 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Forge). The supported version that is affected is 11.4.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via TLS to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Commerce Guided Search / Oracle Commerce Experience Manager and unauthorized read access to a subset of Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:H). |
| CVE-2026-83250 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Forge). The supported version that is affected is 11.4.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Commerce Guided Search / Oracle Commerce Experience Manager. CVSS 3.1 Base Score 6.5 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:N/A:L). |
| CVE-2026-83200 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Process Manufacturing Intelligence product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via Oracle Net to compromise Oracle Process Manufacturing Intelligence. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Process Manufacturing Intelligence accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-83198 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Field Service product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Field Service. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Field Service, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Field Service accessible data as well as unauthorized read access to a subset of Oracle Field Service accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2026-83175 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite (component: Core). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Application Object Library. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Application Object Library accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-83140 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Field Service product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Field Service. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Field Service accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-83109 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Forms product of Oracle Fusion Middleware (component: Forms Services, C/S, Charmode). Supported versions that are affected are 12.2.1.19.0 and 14.1.2.0.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Forms. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Forms accessible data. CVSS 3.1 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-83097 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Forms product of Oracle Fusion Middleware (component: Forms Services, C/S, Charmode). Supported versions that are affected are 12.2.1.19.0 and 14.1.2.0.0. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Forms. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Forms accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Forms. CVSS 3.1 Base Score 6.5 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:H/A:H). |
| CVE-2026-83077 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Siebel CRM Cloud Applications product of Oracle Siebel CRM (component: Siebel Cloud Manager). Supported versions that are affected are 22.3-26.7. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Siebel CRM Cloud Applications. While the vulnerability is in Siebel CRM Cloud Applications, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Siebel CRM Cloud Applications accessible data as well as unauthorized read access to a subset of Siebel CRM Cloud Applications accessible data. CVSS 3.1 Base Score 6.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:N). |
| CVE-2026-83076 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle HR Intelligence product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle HR Intelligence. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle HR Intelligence accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle HR Intelligence. CVSS 3.1 Base Score 6.8 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:H/A:H). |
| CVE-2026-73965 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Siebel CRM Deployment product of Oracle Siebel CRM (component: Cloud Gateway). Supported versions that are affected are 17.0-26.7. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Siebel CRM Deployment. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Siebel CRM Deployment accessible data as well as unauthorized access to critical data or complete access to all Siebel CRM Deployment accessible data. CVSS 3.1 Base Score 6.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-70755 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Web Applications Desktop Integrator product of Oracle E-Business Suite (component: File download). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Web Applications Desktop Integrator. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Web Applications Desktop Integrator accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-62597 | Medium | 2026-09-15 | No exploit published | No public exploit | Vulnerability in the Oracle Enterprise Manager Base Platform product of Oracle Enterprise Manager (component: Event Management). Supported versions that are affected are 13.5 and 24.1. Easily exploitable vulnerability allows low privileged attacker with network access via SOAP to compromise Oracle Enterprise Manager Base Platform. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Enterprise Manager Base Platform accessible data. CVSS 3.1 Base Score 6.5 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:H/A:N). |
| CVE-2026-19880 | Medium | 2026-08-14 | Protected by Waratek | No public exploit | Path-traversal vulnerability in QOS.CH Sarl Logback-classic on Java (logback-classic module) allows path-traversal vulnerability. More specifically, an MDC-based discriminator value flows unsanitized into a nested FileAppender path, letting an attacker who influences that MDC value (e.g. via an HTTP header) create and append log files outside the intended directory. This issue affects Logback-classic: from 0.9.14 through 1.6.2. |
| CVE-2026-59899 | Medium | 2026-07-29 | No exploit published | No public exploit | Netty is an asynchronous, event-driven network application framework. Prior to versions 4.1.136.Final and 4.2.16.Final, `HttpContentEncoder` (the superclass of the production handler `HttpContentCompressor`) maintains a per-channel `ArrayDeque<CharSequence>` named `acceptEncodingQueue` that accumulates attacker-controlled data without any size limit. The queue is filled on the I/O thread for every inbound HTTP request and drained only when the application later writes a non-1xx response. This creates a resource exhaustion vulnerability when an attacker exploits HTTP/1.1 pipelining to flood the connection with requests faster than the application produces responses. This issue has been fixed in versions 4.1.136.Final and 4.2.16.Final. |
| CVE-2026-59898 | Medium | 2026-07-29 | No exploit published | No public exploit | Netty is an asynchronous, event-driven network application framework. Prior to versions 4.1.136.Final and 4.2.16.Final, ab attacker can force WebSocket upgrade via the lax V07 (or V08) handshaker by sending `Sec-WebSocket-Version: 7` and omitting `Connection: Upgrade` / `Upgrade: websocket` headers, completing a protocol switch that a proxy would not recognize as an Upgrade request and enabling HTTP request smuggling / protocol-confusion attacks. This issue has been fixed in versions 4.1.136.Final and 4.2.16.Final. |
| CVE-2026-56746 | Medium | 2026-07-21 | No exploit published | No public exploit | Netty is a network application framework for development of protocol servers and clients. Versions 4.2.0.Final through 4.2.15.Final and 4.1.0.Final through 4.1.135.Final, are vulnerable to security control bypass during the origin evaluation process. CorsHandler provides a shortCircuit() configuration designed to reject unauthorized cross-origin requests immediately, acting as a security control before requests reach the application. However, due to a logical operator error in the origin evaluation process, this protection can be entirely bypassed. An attacker can bypass the short-circuit mechanism by sending a request with an Origin: null header. This failure forwards unauthorized requests to the backend application, bypassing intended access controls. This issue is fixed in versions 4.1.136.Final and 4.2.16.Final. |
| CVE-2026-49844 | Medium | 2026-07-10 | No exploit published | No public exploit | Improper encoding of non-finite floating-point values during MapMessage JSON serialization in Apache Log4j API produces output that is not valid JSON. This issue affects Apache Log4j API versions 2.13.1 through 2.25.4 and version 2.26.0. The fix for CVE-2026-34481 did not cover all code paths: when a MapMessage contains a non-finite IEEE 754 value (NaN, Infinity, or -Infinity), MapMessage.asJson() emits the corresponding bare token. RFC 8259 does not permit these tokens, so a conformant parser rejects the resulting document. The defect is reachable only when both of the following conditions hold: * The application uses the message resolver https://logging.apache.org/log4j/2.x/manual/json-template-layout.html#event-template-resolver-message of JsonTemplateLayout or any other layout that relies on MapMessage.asJson() or MapMessage.getFormattedMessage(new String[]{"JSON"}). * The application logs a MapMessage that contains an attacker-controlled floating-point value. An attacker who can supply a non-finite value can cause the affected layout to emit malformed JSON, which may corrupt the enclosing log record or disrupt downstream log ingestion and parsing. Users are advised to upgrade to Apache Log4j API 2.25.5 or 2.26.1, both of which emit RFC 8259-compliant JSON for non-finite values. |