
Oracle Critical Security Patch Update September 2026
Released September 2026 · Oracle's advisory ↗ · ← Security Patch Update, August 2026 · Critical Patch Update, October 2026 →
806 CVEs in this release, one square each
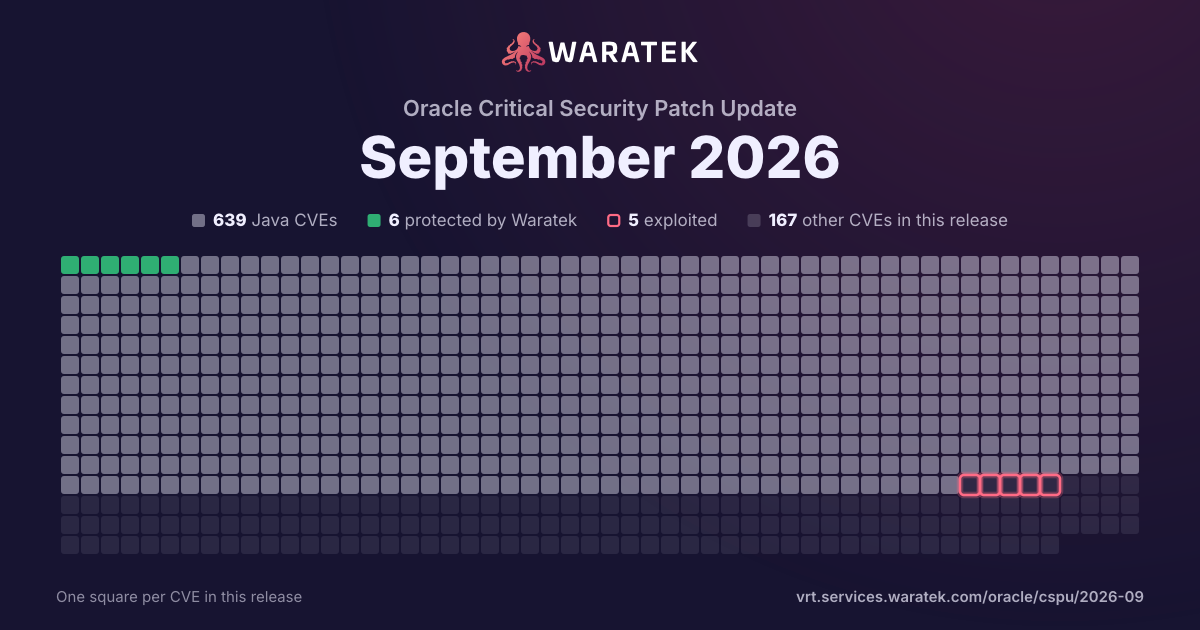
By status
6Protected by Waratek633No exploit published1Outside Waratek scope166Not applicable
5Exploited, marked by the ring
No exploit published. For 596 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 2 in Waratek scope · 2 protected · 3 exploited · 1 CISA KEV · 1 EPSS ≥ 0.5
Protected by Waratek
2
25.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
12.5%
Not applicable
5
62.5%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
25.0%
partly blocked
0
0.0%
not blocked
6
75.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
37.5%
Working exploit published
2
25.0%
Proof of concept only
3
37.5%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 5 / quarter
Q4 231
Outside Waratek scope1
Medium1
not blocked1
Exploited1
Q1 240
Q2 240
Q3 240
Q4 240
Q1 250
Q2 250
Q3 250
Q4 250
Q1 260
Q2 262
Protected by Waratek2
Critical1
Medium1
blocked by ARMR today2
Working exploit published1
Proof of concept only1
Q3 265
Not applicable5
Critical1
High2
Medium1
None1
not blocked5
Exploited2
Working exploit published1
Proof of concept only2
Q4 23Q1 24Q2 24Q3 24Q4 24Q1 25Q2 25Q3 25Q4 25Q1 26Q2 26Q3 26
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2026-64849 | Critical | 2026-08-17 | Not applicable | Exploited | MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. Starting in 3.3.0 and prior to 3.15.0, the unauthenticated POST /api/2.0/mlflow/webhooks/{id}/test endpoint calls _validate_webhook_url() in mlflow/utils/validation.py only for the original URL while mlflow/webhooks/delivery.py follows redirects and re-resolves the hostname without pinning the validated address, allowing attackers to reach internal or cloud metadata services and receive response_status and response_body. This issue is fixed in version 3.15.0. |
| CVE-2026-17544 | High | 2026-07-30 | Not applicable | Proof of concept only | Attacker-provided inputs to bccomp() could lead to an out-of-bounds write with stack and heap corruption in PHP versions from 8.4.* before 8.4.24 and from 8.5.* before 8.5.9. |
| CVE-2026-57219 | High | 2026-07-10 | Not applicable | Working exploit published | RabbitMQ is a messaging and streaming broker. Prior to 3.13.15, 4.0.20, 4.1.11, and 4.2.6, the obsolete GET /api/auth endpoint can disclose the OAuth 2 client secret on RabbitMQ installations configured with management.oauth_client_secret, exposing credentials to unauthenticated callers when the management plugin and that OAuth configuration are enabled. This issue is fixed in versions 3.13.15, 4.0.20, 4.1.11, and 4.2.6. |
| CVE-2026-8857 | None | 2026-07-01 | Not applicable | Exploited | A vulnerability in Wikimedia Foundation timeline. This vulnerability is associated with program files scripts/EasyTimeline.Pl, includes/Timeline.Php. This issue affects timeline: from * before 1.46.0, 1.45.4, 1.44.6, 1.43.9. |
| CVE-2026-58025 | Medium | 2026-07-01 | Not applicable | Proof of concept only | Deserialization of untrusted data vulnerability in Wikimedia Foundation MediaWiki. This vulnerability is associated with program files includes/Import/WikiImporter.Php, includes/Import/WikiRevision.Php, includes/Logging/LogEntryBase.Php. This issue affects MediaWiki: from * before 1.46.0, 1.45.4, 1.44.6, 1.43.9. |
| CVE-2026-50229 | Medium | 2026-06-29 | Protected by Waratek | Working exploit published | Improper Neutralization of Script-Related HTML Tags in a Web Page (Basic XSS) vulnerability in the number guess example for Apache Tomcat. This issue affects Apache Tomcat: from 11.0.0-M1 through 11.0.22, from 10.1.0-M1 through 10.1.55, from 9.0.0.M1 through 9.0.118, from 8.5.0 through 8.5.100, from 7.0.0 through 7.0.109. Other versions that have reached end of support may also be affected. Users are recommended to upgrade to version 11.0.23, 10.1.56 or 9.0.119, which fix the issue. |
| CVE-2026-42779 | Critical | 2026-05-01 | Protected by Waratek | Proof of concept only | The fix for CVE-2026-41635 was not applied to the 2.1.X and 2.2.X branches. Here was the original issue description: Apache MINA's AbstractIoBuffer.resolveClass() contains two branches, one of them (for static classes or primitive types) does not check the class at all, bypassing the classname allowlist and allowing arbitrary code to be executed. The fix checks if the class is present in the accepted class filter before calling Class.forName(). Affected versions are Apache MINA 2.1.0 <= 2.1.11, and 2.2.0 <= 2.2.6. The problem is resolved in Apache MINA 2.1.12, and 2.2.7 by applying the classname allowlist earlier. Affected are applications using Apache MINA that call IoBuffer.getObject(). Applications using Apache MINA are advised to upgrade. |
| CVE-2023-48795 | Medium | 2023-12-18 | Outside Waratek scope | Exploited | The SSH transport protocol with certain OpenSSH extensions, found in OpenSSH before 9.6 and other products, allows remote attackers to bypass integrity checks such that some packets are omitted (from the extension negotiation message), and a client and server may consequently end up with a connection for which some security features have been downgraded or disabled, aka a Terrapin attack. This occurs because the SSH Binary Packet Protocol (BPP), implemented by these extensions, mishandles the handshake phase and mishandles use of sequence numbers. For example, there is an effective attack against SSH's use of ChaCha20-Poly1305 (and CBC with Encrypt-then-MAC). The bypass occurs in chacha20-poly1305@openssh.com and (if CBC is used) the -etm@openssh.com MAC algorithms. This also affects Maverick Synergy Java SSH API before 3.1.0-SNAPSHOT, Dropbear through 2022.83, Ssh before 5.1.1 in Erlang/OTP, PuTTY before 0.80, AsyncSSH before 2.14.2, golang.org/x/crypto before 0.17.0, libssh before 0.10.6, libssh2 through 1.11.0, Thorn Tech SFTP Gateway before 3.4.6, Tera Term before 5.1, Paramiko before 3.4.0, jsch before 0.2.15, SFTPGo before 2.5.6, Netgate pfSense Plus through 23.09.1, Netgate pfSense CE through 2.7.2, HPN-SSH through 18.2.0, ProFTPD before 1.3.8b (and before 1.3.9rc2), ORYX CycloneSSH before 2.3.4, NetSarang XShell 7 before Build 0144, CrushFTP before 10.6.0, ConnectBot SSH library before 2.2.22, Apache MINA sshd through 2.11.0, sshj through 0.37.0, TinySSH through 20230101, trilead-ssh2 6401, LANCOM LCOS and LANconfig, FileZilla before 3.66.4, Nova before 11.8, PKIX-SSH before 14.4, SecureCRT before 9.4.3, Transmit5 before 5.10.4, Win32-OpenSSH before 9.5.0.0p1-Beta, WinSCP before 6.2.2, Bitvise SSH Server before 9.32, Bitvise SSH Client before 9.33, KiTTY through 0.76.1.13, the net-ssh gem 7.2.0 for Ruby, the mscdex ssh2 module before 1.15.0 for Node.js, the thrussh library before 0.35.1 for Rust, and the Russh crate before 0.40.2 for Rust. |