
Oracle Critical Security Patch Update May 2026
Released May 2026 · Oracle's advisory ↗ · ← Critical Patch Update, April 2026 · Security Patch Update, June 2026 →
74 CVEs in this release, one square each
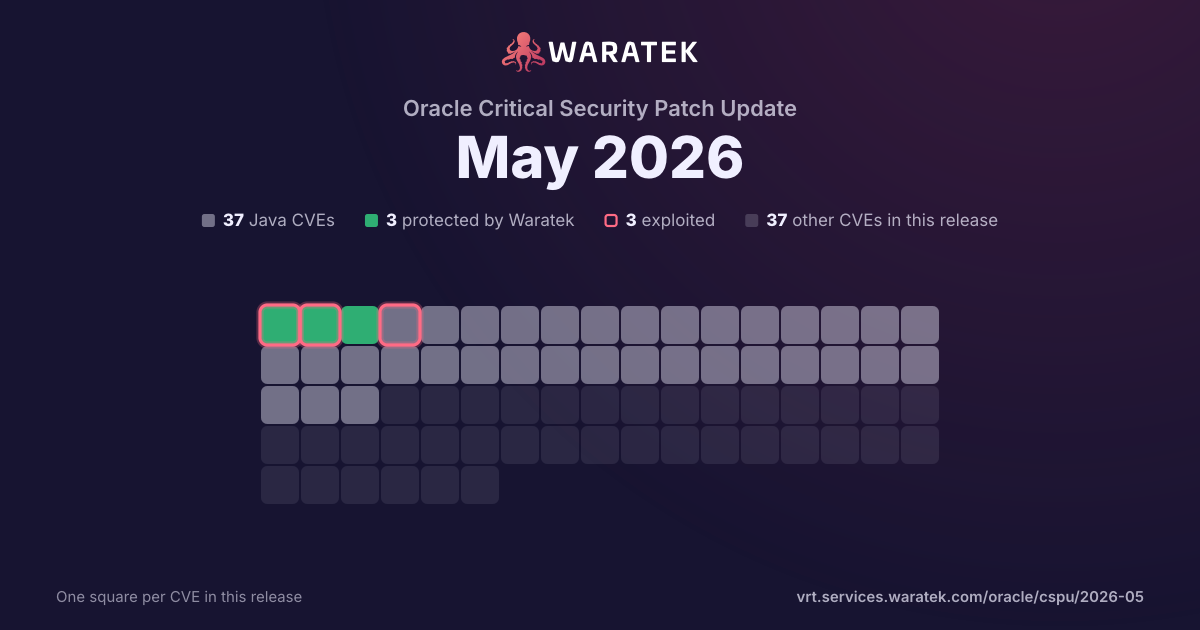
By status
3Protected by Waratek3Mitigation candidate31No exploit published37Not applicable
3Exploited, marked by the ring
No exploit published. For 22 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 2 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
2matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
100.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
2
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
2
100.0%
split by
peak 2 / month
Apr 26
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2026-41043 | Medium | 2026-04-24 | No exploit published | No public exploit | Improper Neutralization of Script-Related HTML Tags in a Web Page (Basic XSS) vulnerability in Apache ActiveMQ, Apache ActiveMQ Web. An authenticated attacker can show malicious content when browsing queues in the web console by overriding the content type to be HTML (instead of XML) and by injecting HTML into a JMS selector field. This issue affects Apache ActiveMQ: before 5.19.6, from 6.0.0 before 6.2.5; Apache ActiveMQ Web: before 5.19.6, from 6.0.0 before 6.2.5. Users are recommended to upgrade to version 6.2.5 or 5.19.6, which fixes the issue. |
| CVE-2026-34500 | Medium | 2026-04-09 | No exploit published | No public exploit | CLIENT_CERT authentication does not fail as expected for some scenarios when soft fail is disabled and FFM is used in Apache Tomcat. This issue affects Apache Tomcat: from 11.0.0-M14 through 11.0.20, from 10.1.22 through 10.1.53, from 9.0.92 through 9.0.116. Users are recommended to upgrade to version 11.0.21, 10.1.54 or 9.0.117, which fixes the issue. |