
Oracle Critical Patch Update January 2026
Released January 2026 · Oracle's advisory ↗ · ← Critical Patch Update, October 2025 · Critical Patch Update, April 2026 →
219 CVEs in this release, one square each
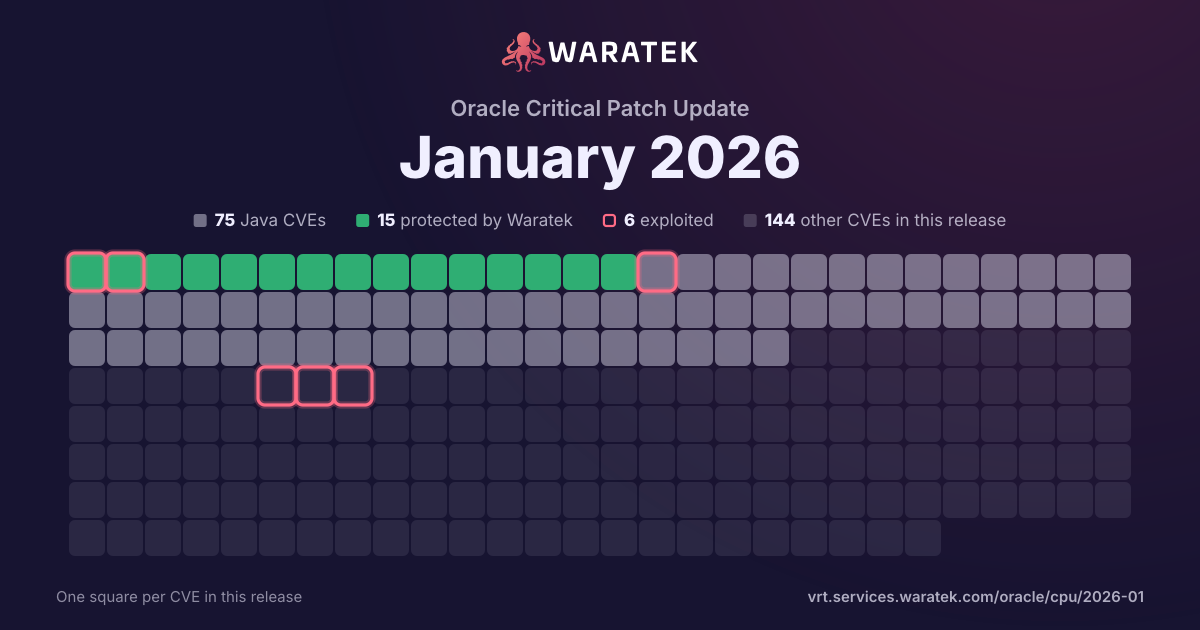
By status
15Protected by Waratek2Mitigation candidate58No exploit published14Outside Waratek scope130Not applicable
6Exploited, marked by the ring
No exploit published. For 26 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 204 matches · 60 in Waratek scope · 0 protected · 4 exploited · 2 CISA KEV · 12 public PoC · 4 EPSS ≥ 0.5
204matches
60in Waratek scope29.4%
0protected0.0%
4exploited2.0%
2CISA KEV1.0%
12public PoC5.9%
4EPSS ≥ 0.52.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
2
1.0%
No exploit published
58
28.4%
Outside Waratek scope
14
6.9%
Not applicable
130
63.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
204
100.0%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 66 / quarter
Q1 221
Not applicable1
Medium1
not blocked1
No public exploit1
Q2 220
Q3 220
Q4 220
Q1 233
Not applicable3
High3
not blocked3
No public exploit3
Q2 230
Q3 230
Q4 234
Not applicable4
High1
Medium3
not blocked4
No public exploit4
Q1 242
Not applicable2
Critical1
Medium1
not blocked2
No public exploit2
Q2 240
Q3 241
Not applicable1
Medium1
not blocked1
No public exploit1
Q4 245
No exploit published2
Outside Waratek scope1
Not applicable2
High1
Medium4
not blocked5
Proof of concept only1
No public exploit4
Q1 257
No exploit published2
Not applicable5
High3
Medium4
not blocked7
Exploited1
Proof of concept only3
No public exploit3
Q2 2525
Mitigation candidate2
No exploit published7
Outside Waratek scope2
Not applicable14
Critical2
High16
Medium6
Low1
not blocked25
Exploited1
Working exploit published1
Proof of concept only6
No public exploit17
Q3 2560
No exploit published12
Outside Waratek scope6
Not applicable42
Critical3
High27
Medium24
Low6
not blocked60
Working exploit published2
Proof of concept only13
No public exploit45
Q4 2530
No exploit published8
Outside Waratek scope1
Not applicable21
Critical2
High14
Medium11
Low3
not blocked30
Exploited1
Working exploit published3
Proof of concept only4
No public exploit22
Q1 2666
No exploit published27
Outside Waratek scope4
Not applicable35
Critical2
High19
Medium41
Low4
not blocked66
Exploited1
No public exploit65
Q1 22Q3 22Q1 23Q3 23Q1 24Q3 24Q1 25Q3 25Q1 26
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2023-1393 | High | 2023-03-30 | Not applicable | No public exploit | A flaw was found in X.Org Server Overlay Window. A Use-After-Free may lead to local privilege escalation. If a client explicitly destroys the compositor overlay window (aka COW), the Xserver would leave a dangling pointer to that window in the CompScreen structure, which will trigger a use-after-free later. |
| CVE-2022-41342 | High | 2023-02-06 | Not applicable | No public exploit | Improper buffer restrictions in the Intel(R) C++ Compiler Classic before version 2021.7.1 for some Intel(R) oneAPI Toolkits before version 2022.3.1 may allow a privileged user to potentially enable escalation of privilege via local access. |
| CVE-2022-40196 | High | 2023-02-06 | Not applicable | No public exploit | Improper access control in the Intel(R) oneAPI DPC++/C++ Compiler before version 2022.2.1 and Intel C++ Compiler Classic before version 2021.7.1 for some Intel(R) oneAPI Toolkits before version 2022.3.1 may allow an authenticated user to potentially enable escalation of privilege via local access. |
| CVE-2022-23395 | Medium | 2022-03-02 | Not applicable | No public exploit | jQuery Cookie 1.4.1 is affected by prototype pollution, which can lead to DOM cross-site scripting (XSS). |