
Oracle Critical Patch Update October 2025
Released October 2025 · Oracle's advisory ↗ · ← Critical Patch Update, July 2025 · Critical Patch Update, January 2026 →
234 CVEs in this release, one square each
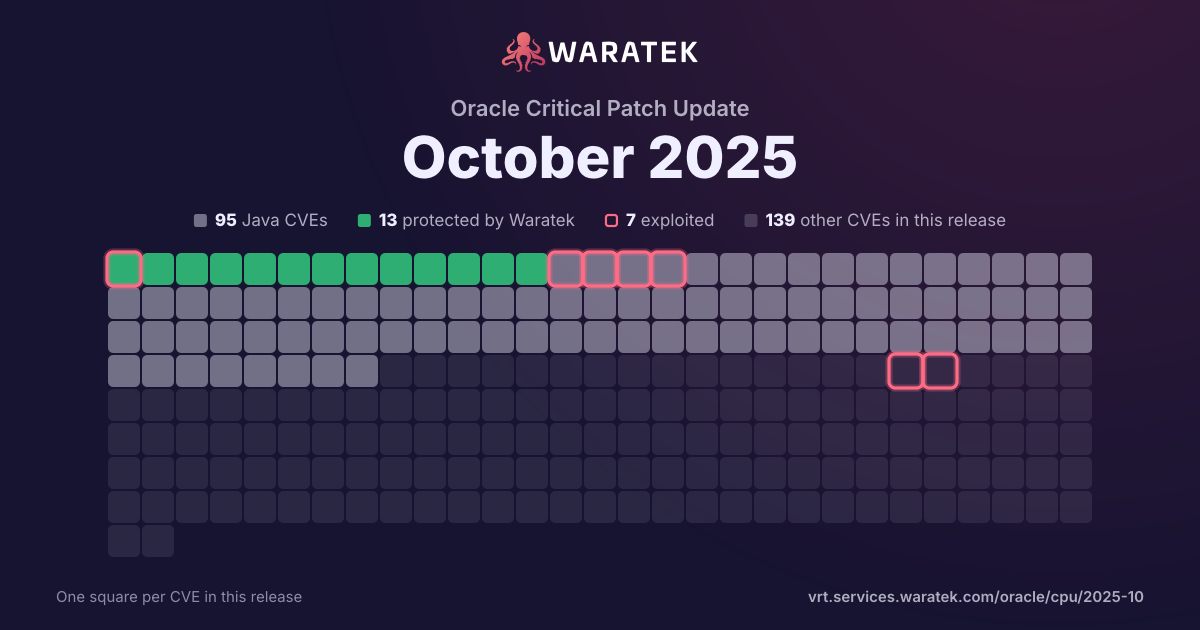
By status
13Protected by Waratek5Mitigation candidate77No exploit published15Outside Waratek scope124Not applicable
7Exploited, marked by the ring
No exploit published. For 36 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 124 matches · 0 in Waratek scope · 0 protected · 2 exploited · 2 CISA KEV · 7 public PoC · 2 EPSS ≥ 0.5
124matches
0in Waratek scope0.0%
0protected0.0%
2exploited1.6%
2CISA KEV1.6%
7public PoC5.6%
2EPSS ≥ 0.51.6%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
124
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
124
100.0%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 37 / quarter
Q2 211
Not applicable1
Medium1
not blocked1
Proof of concept only1
Q3 210
Q4 210
Q1 220
Q2 220
Q3 220
Q4 220
Q1 230
Q2 235
Not applicable5
Medium5
not blocked5
Proof of concept only1
No public exploit4
Q3 230
Q4 231
Not applicable1
Critical1
not blocked1
No public exploit1
Q1 241
Not applicable1
Critical1
not blocked1
No public exploit1
Q2 245
Not applicable5
Critical1
High2
Medium2
not blocked5
Forecast only1
No public exploit4
Q3 244
Not applicable4
High1
Medium3
not blocked4
Proof of concept only1
No public exploit3
Q4 242
Not applicable2
High1
Medium1
not blocked2
No public exploit2
Q1 2510
Not applicable10
High6
Medium3
Low1
not blocked10
Exploited1
Proof of concept only1
No public exploit8
Q2 2525
Not applicable25
Critical3
High10
Medium11
Low1
not blocked25
Proof of concept only8
No public exploit17
Q3 2537
Not applicable37
High19
Medium15
Low3
not blocked37
Exploited1
Working exploit published2
Proof of concept only4
No public exploit30
Q4 2533
Not applicable33
High7
Medium22
Low4
not blocked33
No public exploit33
Q2 21Q4 21Q2 22Q4 22Q2 23Q4 23Q2 24Q4 24Q2 25Q4 25
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2024-54160 | Medium | 2025-02-12 | Not applicable | No public exploit | dashboards-reporting (aka Dashboards Reports) before 2.19.0.0, as shipped in OpenSearch before 2.19, allows XSS because Markdown is not sanitized when previewing a header or footer. |
| CVE-2024-12797 | High | 2025-02-11 | Not applicable | No public exploit | Issue summary: Clients using RFC7250 Raw Public Keys (RPKs) to authenticate a server may fail to notice that the server was not authenticated, because handshakes don't abort as expected when the SSL_VERIFY_PEER verification mode is set. Impact summary: TLS and DTLS connections using raw public keys may be vulnerable to man-in-middle attacks when server authentication failure is not detected by clients. RPKs are disabled by default in both TLS clients and TLS servers. The issue only arises when TLS clients explicitly enable RPK use by the server, and the server, likewise, enables sending of an RPK instead of an X.509 certificate chain. The affected clients are those that then rely on the handshake to fail when the server's RPK fails to match one of the expected public keys, by setting the verification mode to SSL_VERIFY_PEER. Clients that enable server-side raw public keys can still find out that raw public key verification failed by calling SSL_get_verify_result(), and those that do, and take appropriate action, are not affected. This issue was introduced in the initial implementation of RPK support in OpenSSL 3.2. The FIPS modules in 3.4, 3.3, 3.2, 3.1 and 3.0 are not affected by this issue. |
| CVE-2024-12133 | Medium | 2025-02-10 | Not applicable | No public exploit | A flaw in libtasn1 causes inefficient handling of specific certificate data. When processing a large number of elements in a certificate, libtasn1 takes much longer than expected, which can slow down or even crash the system. This flaw allows an attacker to send a specially crafted certificate, causing a denial of service attack. |
| CVE-2024-57699 | High | 2025-02-05 | Not applicable | Proof of concept only | A security issue was found in Netplex Json-smart 2.5.0 through 2.5.1. When loading a specially crafted JSON input, containing a large number of ’{’, a stack exhaustion can be trigger, which could allow an attacker to cause a Denial of Service (DoS). This issue exists because of an incomplete fix for CVE-2023-1370. |
| CVE-2025-23084 | Medium | 2025-01-28 | Not applicable | No public exploit | A vulnerability has been identified in Node.js, specifically affecting the handling of drive names in the Windows environment. Certain Node.js functions do not treat drive names as special on Windows. As a result, although Node.js assumes a relative path, it actually refers to the root directory. On Windows, a path that does not start with the file separator is treated as relative to the current directory. This vulnerability affects Windows users of `path.join` API. |
| CVE-2024-12254 | High | 2024-12-06 | Not applicable | No public exploit | Starting in Python 3.12.0, the asyncio._SelectorSocketTransport.writelines() method would not "pause" writing and signal to the Protocol to drain the buffer to the wire once the write buffer reached the "high-water mark". Because of this, Protocols would not periodically drain the write buffer potentially leading to memory exhaustion. This vulnerability likely impacts a small number of users, you must be using Python 3.12.0 or later, on macOS or Linux, using the asyncio module with protocols, and using .writelines() method which had new zero-copy-on-write behavior in Python 3.12.0 and later. If not all of these factors are true then your usage of Python is unaffected. |
| CVE-2024-9287 | Medium | 2024-10-22 | Not applicable | No public exploit | A vulnerability has been found in the CPython `venv` module and CLI where path names provided when creating a virtual environment were not quoted properly, allowing the creator to inject commands into virtual environment "activation" scripts (ie "source venv/bin/activate"). This means that attacker-controlled virtual environments are able to run commands when the virtual environment is activated. Virtual environments which are not created by an attacker or which aren't activated before being used (ie "./venv/bin/python") are not affected. |
| CVE-2024-8006 | Medium | 2024-08-31 | Not applicable | No public exploit | Remote packet capture support is disabled by default in libpcap. When a user builds libpcap with remote packet capture support enabled, one of the functions that become available is pcap_findalldevs_ex(). One of the function arguments can be a filesystem path, which normally means a directory with input data files. When the specified path cannot be used as a directory, the function receives NULL from opendir(), but does not check the return value and passes the NULL value to readdir(), which causes a NULL pointer derefence. |
| CVE-2023-7256 | Medium | 2024-08-31 | Not applicable | No public exploit | In affected libpcap versions during the setup of a remote packet capture the internal function sock_initaddress() calls getaddrinfo() and possibly freeaddrinfo(), but does not clearly indicate to the caller function whether freeaddrinfo() still remains to be called after the function returns. This makes it possible in some scenarios that both the function and its caller call freeaddrinfo() for the same allocated memory block. A similar problem was reported in Apple libpcap, to which Apple assigned CVE-2023-40400. |
| CVE-2024-8088 | High | 2024-08-22 | Not applicable | No public exploit | There is a HIGH severity vulnerability affecting the CPython "zipfile" module affecting "zipfile.Path". Note that the more common API "zipfile.ZipFile" class is unaffected. When iterating over names of entries in a zip archive (for example, methods of "zipfile.Path" like "namelist()", "iterdir()", etc) the process can be put into an infinite loop with a maliciously crafted zip archive. This defect applies when reading only metadata or extracting the contents of the zip archive. Programs that are not handling user-controlled zip archives are not affected. |
| CVE-2024-6923 | Medium | 2024-08-01 | Not applicable | Proof of concept only | There is a MEDIUM severity vulnerability affecting CPython. The email module didn’t properly quote newlines for email headers when serializing an email message allowing for header injection when an email is serialized. |
| CVE-2024-37371 | Critical | 2024-06-28 | Not applicable | No public exploit | In MIT Kerberos 5 (aka krb5) before 1.21.3, an attacker can cause invalid memory reads during GSS message token handling by sending message tokens with invalid length fields. |
| CVE-2024-37370 | High | 2024-06-28 | Not applicable | No public exploit | In MIT Kerberos 5 (aka krb5) before 1.21.3, an attacker can modify the plaintext Extra Count field of a confidential GSS krb5 wrap token, causing the unwrapped token to appear truncated to the application. |
| CVE-2024-35195 | Medium | 2024-05-20 | Not applicable | No public exploit | Requests is a HTTP library. Prior to 2.32.0, when making requests through a Requests `Session`, if the first request is made with `verify=False` to disable cert verification, all subsequent requests to the same host will continue to ignore cert verification regardless of changes to the value of `verify`. This behavior will continue for the lifecycle of the connection in the connection pool. This vulnerability is fixed in 2.32.0. |
| CVE-2024-4140 | High | 2024-05-02 | Not applicable | No public exploit | An excessive memory use issue (CWE-770) exists in Email-MIME, before version 1.954, which can cause denial of service when parsing multipart MIME messages. The patch set (from 2020 and 2024) limits excessive depth and the total number of parts. |
| CVE-2024-28182 | Medium | 2024-04-04 | Not applicable | Forecast only | nghttp2 is an implementation of the Hypertext Transfer Protocol version 2 in C. The nghttp2 library prior to version 1.61.0 keeps reading the unbounded number of HTTP/2 CONTINUATION frames even after a stream is reset to keep HPACK context in sync. This causes excessive CPU usage to decode HPACK stream. nghttp2 v1.61.0 mitigates this vulnerability by limiting the number of CONTINUATION frames it accepts per stream. There is no workaround for this vulnerability. |
| CVE-2024-23807 | Critical | 2024-02-29 | Not applicable | No public exploit | The Apache Xerces C++ XML parser on versions 3.0.0 before 3.2.5 contains a use-after-free error triggered during the scanning of external DTDs. Users are recommended to upgrade to version 3.2.5 which fixes the issue, or mitigate the issue by disabling DTD processing. This can be accomplished via the DOM using a standard parser feature, or via SAX using the XERCES_DISABLE_DTD environment variable. This issue has been disclosed before as CVE-2018-1311, but unfortunately that advisory incorrectly stated the issue would be fixed in version 3.2.3 or 3.2.4. |
| CVE-2023-45853 | Critical | 2023-10-14 | Not applicable | No public exploit | MiniZip in zlib through 1.3 has an integer overflow and resultant heap-based buffer overflow in zipOpenNewFileInZip4_64 via a long filename, comment, or extra field. NOTE: MiniZip is not a supported part of the zlib product. NOTE: pyminizip through 0.2.6 is also vulnerable because it bundles an affected zlib version, and exposes the applicable MiniZip code through its compress API. |
| CVE-2023-26555 | Medium | 2023-04-11 | Not applicable | No public exploit | praecis_parse in ntpd/refclock_palisade.c in NTP 4.2.8p15 has an out-of-bounds write. Any attack method would be complex, e.g., with a manipulated GPS receiver. |
| CVE-2023-26554 | Medium | 2023-04-11 | Not applicable | Proof of concept only | mstolfp in libntp/mstolfp.c in NTP 4.2.8p15 has an out-of-bounds write when adding a '\0' character. An adversary may be able to attack a client ntpq process, but cannot attack ntpd. |
| CVE-2023-26553 | Medium | 2023-04-11 | Not applicable | No public exploit | mstolfp in libntp/mstolfp.c in NTP 4.2.8p15 has an out-of-bounds write when copying the trailing number. An adversary may be able to attack a client ntpq process, but cannot attack ntpd. |
| CVE-2023-26552 | Medium | 2023-04-11 | Not applicable | No public exploit | mstolfp in libntp/mstolfp.c in NTP 4.2.8p15 has an out-of-bounds write when adding a decimal point. An adversary may be able to attack a client ntpq process, but cannot attack ntpd. |
| CVE-2023-26551 | Medium | 2023-04-11 | Not applicable | No public exploit | mstolfp in libntp/mstolfp.c in NTP 4.2.8p15 has an out-of-bounds write in the cp<cpdec while loop. An adversary may be able to attack a client ntpq process, but cannot attack ntpd. |
| CVE-2021-22897 | Medium | 2021-06-11 | Not applicable | Proof of concept only | curl 7.61.0 through 7.76.1 suffers from exposure of data element to wrong session due to a mistake in the code for CURLOPT_SSL_CIPHER_LIST when libcurl is built to use the Schannel TLS library. The selected cipher set was stored in a single "static" variable in the library, which has the surprising side-effect that if an application sets up multiple concurrent transfers, the last one that sets the ciphers will accidentally control the set used by all transfers. In a worst-case scenario, this weakens transport security significantly. |