
Oracle Critical Patch Update October 2025
Released October 2025 · Oracle's advisory ↗ · ← Critical Patch Update, July 2025 · Critical Patch Update, January 2026 →
234 CVEs in this release, one square each
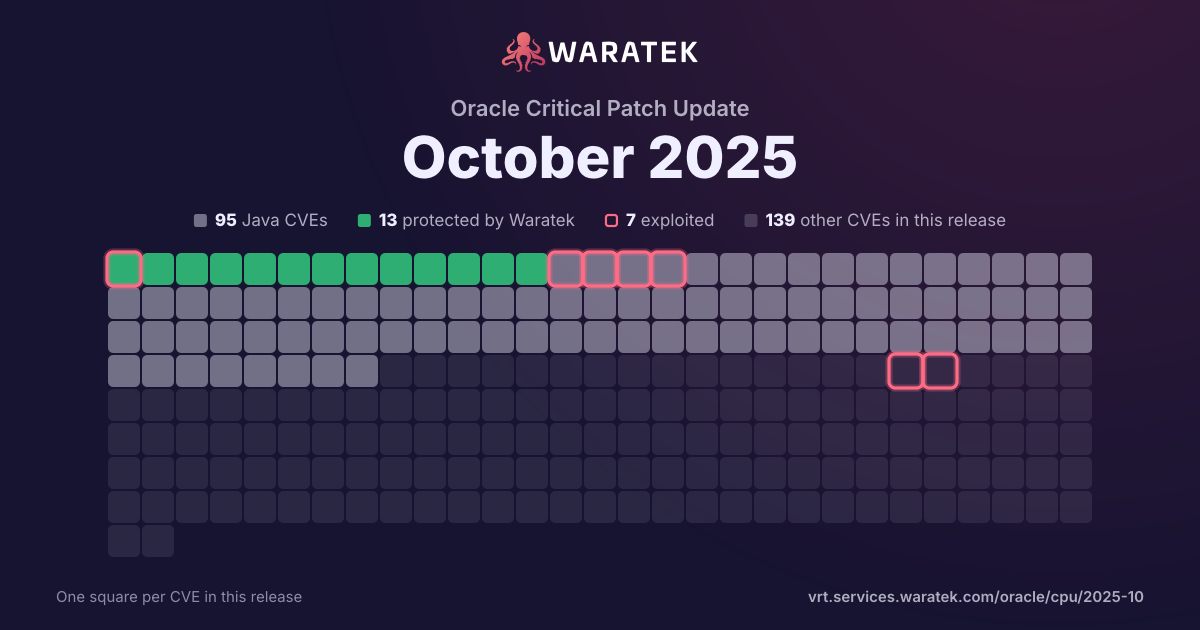
By status
13Protected by Waratek5Mitigation candidate77No exploit published15Outside Waratek scope124Not applicable
7Exploited, marked by the ring
No exploit published. For 36 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 3 matches · 1 in Waratek scope · 1 protected · 1 EPSS ≥ 0.5
Protected by Waratek
1
33.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
2
66.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
33.3%
partly blocked
0
0.0%
not blocked
2
66.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
100.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / month
Mar 25Apr 25May 25Jun 25Jul 25Aug 25Sep 25Oct 25
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2025-61757 | Critical | 2025-10-21 | Protected by Waratek | Exploited | Vulnerability in the Identity Manager product of Oracle Fusion Middleware (component: REST WebServices). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Identity Manager. Successful attacks of this vulnerability can result in takeover of Identity Manager. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2025-6558 | High | 2025-07-15 | Not applicable | Exploited | Insufficient validation of untrusted input in ANGLE and GPU in Google Chrome prior to 138.0.7204.157 allowed a remote attacker to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High) |
| CVE-2025-27363 | High | 2025-03-11 | Not applicable | Exploited | An out of bounds write exists in FreeType versions 2.13.0 and below (newer versions of FreeType are not vulnerable) when attempting to parse font subglyph structures related to TrueType GX and variable font files. The vulnerable code assigns a signed short value to an unsigned long and then adds a static value causing it to wrap around and allocate too small of a heap buffer. The code then writes up to 6 signed long integers out of bounds relative to this buffer. This may result in arbitrary code execution. This vulnerability may have been exploited in the wild. |