
Oracle Critical Patch Update July 2025
Released July 2025 · Oracle's advisory ↗ · ← Critical Patch Update, April 2025 · Critical Patch Update, October 2025 →
196 CVEs in this release, one square each
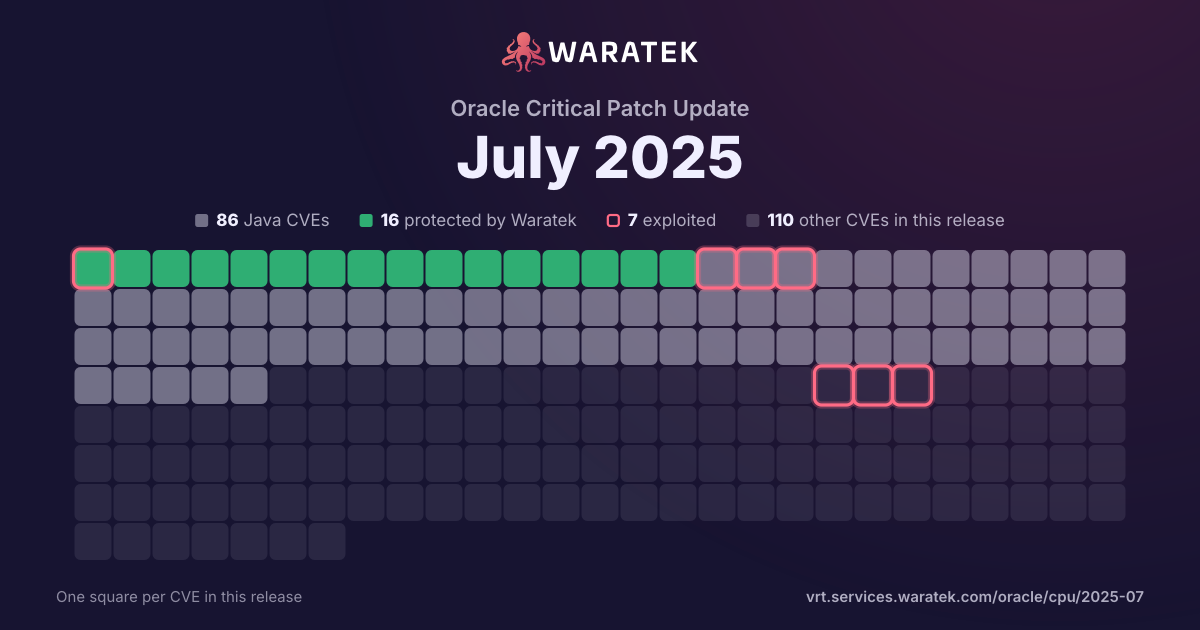
By status
16Protected by Waratek4Mitigation candidate66No exploit published14Outside Waratek scope96Not applicable
7Exploited, marked by the ring
No exploit published. For 31 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 102 matches · 43 in Waratek scope · 3 protected · 2 exploited · 0 CISA KEV · 2 public PoC · 3 EPSS ≥ 0.5
102matches
43in Waratek scope42.2%
3protected2.9%
2exploited2.0%
0CISA KEV0.0%
2public PoC2.0%
3EPSS ≥ 0.52.9%
Protected by Waratek
3
2.9%
Rule in development
0
0.0%
Mitigation candidate
3
2.9%
No exploit published
37
36.3%
Outside Waratek scope
5
4.9%
Not applicable
54
52.9%
Withdrawn CVE
0
0.0%
blocked by ARMR today
3
2.9%
partly blocked
0
0.0%
not blocked
99
97.1%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 52 / quarter
Q4 232
No exploit published2
Medium2
not blocked2
No public exploit2
Q1 242
No exploit published1
Not applicable1
Medium2
not blocked2
No public exploit2
Q2 248
No exploit published1
Outside Waratek scope2
Not applicable5
Medium8
not blocked8
Forecast only1
No public exploit7
Q3 246
Not applicable6
Medium6
not blocked6
No public exploit6
Q4 2413
No exploit published8
Outside Waratek scope1
Not applicable4
Medium13
not blocked13
Proof of concept only1
No public exploit12
Q1 2513
Protected by Waratek1
Mitigation candidate2
No exploit published3
Outside Waratek scope1
Not applicable6
Medium13
blocked by ARMR today1
not blocked12
Exploited2
Proof of concept only3
No public exploit8
Q2 256
Mitigation candidate1
No exploit published3
Not applicable2
Medium6
not blocked6
Working exploit published1
Proof of concept only2
No public exploit3
Q3 2552
Protected by Waratek2
No exploit published19
Outside Waratek scope1
Not applicable30
Medium52
blocked by ARMR today2
not blocked50
No public exploit52
Q4 23Q1 24Q2 24Q3 24Q4 24Q1 25Q2 25Q3 25
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2023-51074 | Medium | 2023-12-27 | No exploit published | No public exploit | json-path v2.8.0 was discovered to contain a stack overflow via the Criteria.parse() method. |
| CVE-2023-44483 | Medium | 2023-10-20 | No exploit published | No public exploit | All versions of Apache Santuario - XML Security for Java prior to 2.2.6, 2.3.4, and 3.0.3, when using the JSR 105 API, are vulnerable to an issue where a private key may be disclosed in log files when generating an XML Signature and logging with debug level is enabled. Users are recommended to upgrade to version 2.2.6, 2.3.4, or 3.0.3, which fixes this issue. |