
Oracle Critical Patch Update July 2023
Released July 2023 · Oracle's advisory ↗ · ← Critical Patch Update, April 2023 · Critical Patch Update, October 2023 →
269 CVEs in this release, one square each
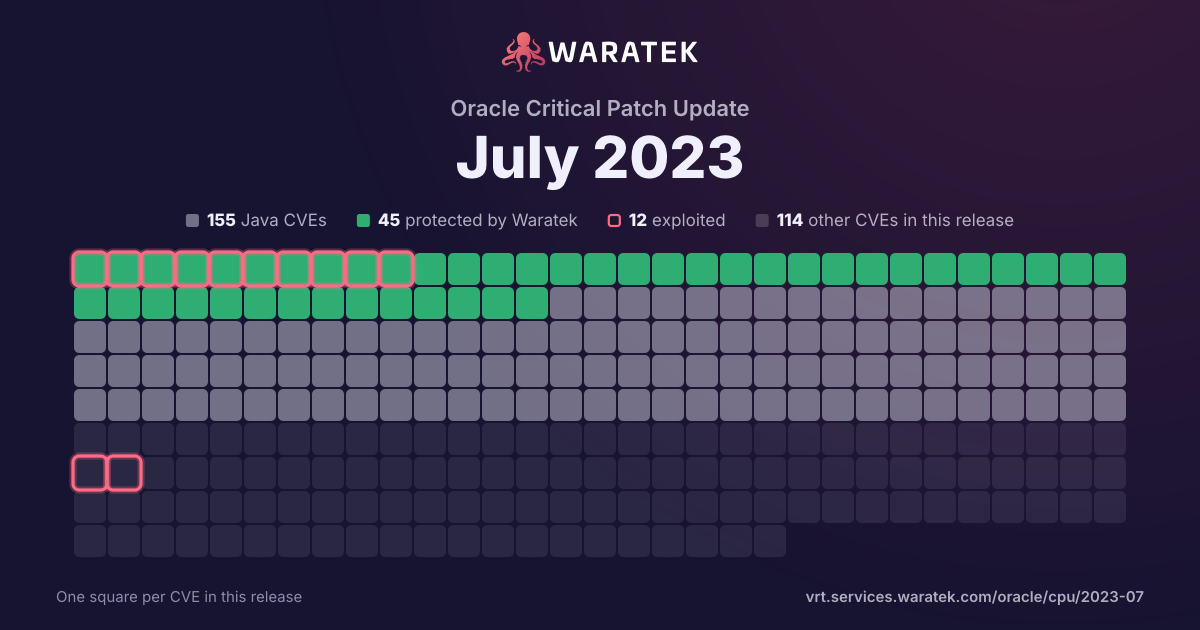
By status
45Protected by Waratek5Mitigation candidate105No exploit published31Outside Waratek scope83Not applicable
12Exploited, marked by the ring
No exploit published. For 37 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 105 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
105
100.0%
Outside Waratek scope
0
0.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
105
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
13
12.4%
Forecast only
1
1.0%
No public exploit
91
86.7%
split by
peak 24 / quarter
Q3 181
No exploit published1
Medium1
not blocked1
No public exploit1
Q4 180
Q1 190
Q2 190
Q3 191
No exploit published1
High1
not blocked1
No public exploit1
Q4 191
No exploit published1
Critical1
not blocked1
No public exploit1
Q1 201
No exploit published1
Critical1
not blocked1
No public exploit1
Q2 200
Q3 200
Q4 202
No exploit published2
High1
Low1
not blocked2
No public exploit2
Q1 217
No exploit published7
High4
Medium3
not blocked7
Forecast only1
No public exploit6
Q2 211
No exploit published1
Medium1
not blocked1
No public exploit1
Q3 217
No exploit published7
High5
Medium2
not blocked7
No public exploit7
Q4 210
Q1 224
No exploit published4
High3
Medium1
not blocked4
Proof of concept only2
No public exploit2
Q2 224
No exploit published4
High1
Medium2
Low1
not blocked4
Proof of concept only1
No public exploit3
Q3 2213
No exploit published13
Critical3
High7
Medium2
Low1
not blocked13
Proof of concept only2
No public exploit11
Q4 2215
No exploit published15
High12
Medium3
not blocked15
Proof of concept only5
No public exploit10
Q1 2316
No exploit published16
Critical1
High8
Medium7
not blocked16
Proof of concept only3
No public exploit13
Q2 238
No exploit published8
Critical2
High1
Medium5
not blocked8
No public exploit8
Q3 2324
No exploit published24
High3
Medium20
Low1
not blocked24
No public exploit24
Q3 18Q1 19Q3 19Q1 20Q3 20Q1 21Q3 21Q1 22Q3 22Q1 23Q3 23
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2020-7760 | High | 2020-10-30 | No exploit published | No public exploit | This affects the package codemirror before 5.58.2; the package org.apache.marmotta.webjars:codemirror before 5.58.2. The vulnerable regular expression is located in https://github.com/codemirror/CodeMirror/blob/cdb228ac736369c685865b122b736cd0d397836c/mode/javascript/javascript.jsL129. The ReDOS vulnerability of the regex is mainly due to the sub-pattern (s|/*.*?*/)* |
| CVE-2020-1953 | Critical | 2020-03-13 | No exploit published | No public exploit | Apache Commons Configuration uses a third-party library to parse YAML files which by default allows the instantiation of classes if the YAML includes special statements. Apache Commons Configuration versions 2.2, 2.3, 2.4, 2.5, 2.6 did not change the default settings of this library. So if a YAML file was loaded from an untrusted source, it could therefore load and execute code out of the control of the host application. |
| CVE-2019-17531 | Critical | 2019-10-12 | No exploit published | No public exploit | A Polymorphic Typing issue was discovered in FasterXML jackson-databind 2.0.0 through 2.9.10. When Default Typing is enabled (either globally or for a specific property) for an externally exposed JSON endpoint and the service has the apache-log4j-extra (version 1.2.x) jar in the classpath, and an attacker can provide a JNDI service to access, it is possible to make the service execute a malicious payload. |
| CVE-2019-12402 | High | 2019-08-30 | No exploit published | No public exploit | The file name encoding algorithm used internally in Apache Commons Compress 1.15 to 1.18 can get into an infinite loop when faced with specially crafted inputs. This can lead to a denial of service attack if an attacker can choose the file names inside of an archive created by Compress. |
| CVE-2018-8032 | Medium | 2018-08-02 | No exploit published | No public exploit | Apache Axis 1.x up to and including 1.4 is vulnerable to a cross-site scripting (XSS) attack in the default servlet/services. |