
Oracle Critical Patch Update July 2023
Released July 2023 · Oracle's advisory ↗ · ← Critical Patch Update, April 2023 · Critical Patch Update, October 2023 →
269 CVEs in this release, one square each
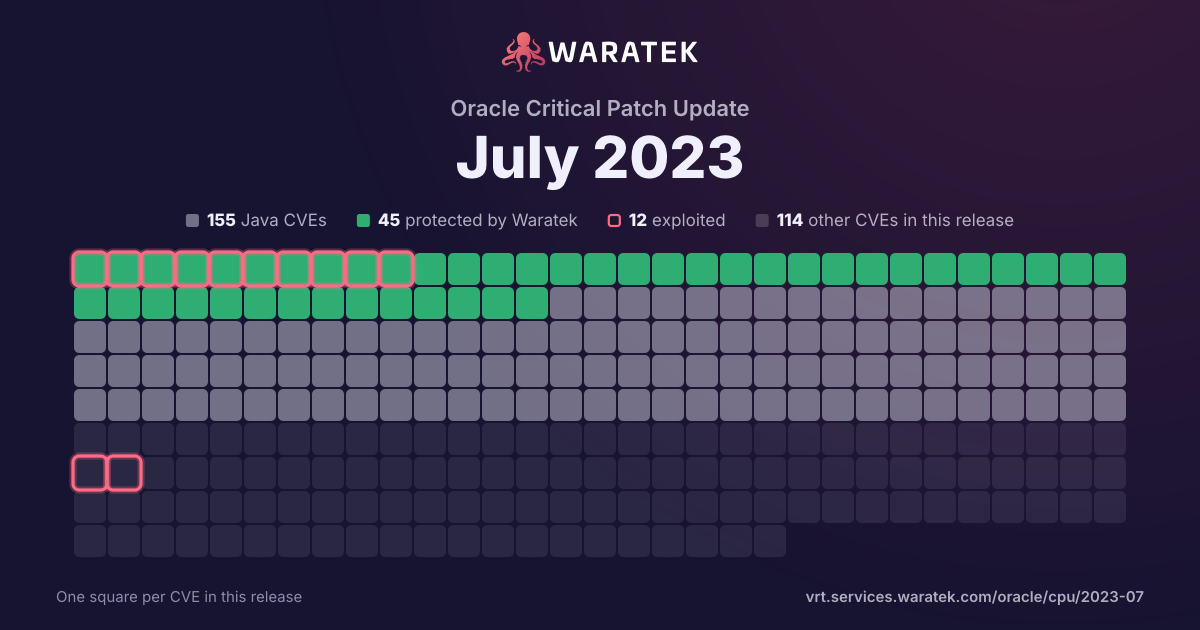
By status
45Protected by Waratek5Mitigation candidate105No exploit published31Outside Waratek scope83Not applicable
12Exploited, marked by the ring
No exploit published. For 37 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 4 in Waratek scope · 3 protected · 3 exploited · 0 CISA KEV · 2 public PoC
Protected by Waratek
3
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
16.7%
Outside Waratek scope
0
0.0%
Not applicable
2
33.3%
Withdrawn CVE
0
0.0%
blocked by ARMR today
3
50.0%
partly blocked
0
0.0%
not blocked
3
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
50.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
3
50.0%
No public exploit
0
0.0%
split by
peak 2 / quarter
Q1 211
No exploit published1
Medium1
not blocked1
Forecast only1
Q2 210
Q3 211
Protected by Waratek1
Medium1
blocked by ARMR today1
Exploited1
Q4 212
Protected by Waratek2
Medium2
blocked by ARMR today2
Exploited2
Q1 220
Q2 220
Q3 220
Q4 220
Q1 231
Not applicable1
Medium1
not blocked1
Forecast only1
Q2 231
Not applicable1
Medium1
not blocked1
Forecast only1
Q1 21Q2 21Q3 21Q4 21Q1 22Q2 22Q3 22Q4 22Q1 23Q2 23
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2023-2650 | Medium | 2023-05-30 | Not applicable | Forecast only | Issue summary: Processing some specially crafted ASN.1 object identifiers or data containing them may be very slow. Impact summary: Applications that use OBJ_obj2txt() directly, or use any of the OpenSSL subsystems OCSP, PKCS7/SMIME, CMS, CMP/CRMF or TS with no message size limit may experience notable to very long delays when processing those messages, which may lead to a Denial of Service. An OBJECT IDENTIFIER is composed of a series of numbers - sub-identifiers - most of which have no size limit. OBJ_obj2txt() may be used to translate an ASN.1 OBJECT IDENTIFIER given in DER encoding form (using the OpenSSL type ASN1_OBJECT) to its canonical numeric text form, which are the sub-identifiers of the OBJECT IDENTIFIER in decimal form, separated by periods. When one of the sub-identifiers in the OBJECT IDENTIFIER is very large (these are sizes that are seen as absurdly large, taking up tens or hundreds of KiBs), the translation to a decimal number in text may take a very long time. The time complexity is O(n^2) with 'n' being the size of the sub-identifiers in bytes (*). With OpenSSL 3.0, support to fetch cryptographic algorithms using names / identifiers in string form was introduced. This includes using OBJECT IDENTIFIERs in canonical numeric text form as identifiers for fetching algorithms. Such OBJECT IDENTIFIERs may be received through the ASN.1 structure AlgorithmIdentifier, which is commonly used in multiple protocols to specify what cryptographic algorithm should be used to sign or verify, encrypt or decrypt, or digest passed data. Applications that call OBJ_obj2txt() directly with untrusted data are affected, with any version of OpenSSL. If the use is for the mere purpose of display, the severity is considered low. In OpenSSL 3.0 and newer, this affects the subsystems OCSP, PKCS7/SMIME, CMS, CMP/CRMF or TS. It also impacts anything that processes X.509 certificates, including simple things like verifying its signature. The impact on TLS is relatively low, because all versions of OpenSSL have a 100KiB limit on the peer's certificate chain. Additionally, this only impacts clients, or servers that have explicitly enabled client authentication. In OpenSSL 1.1.1 and 1.0.2, this only affects displaying diverse objects, such as X.509 certificates. This is assumed to not happen in such a way that it would cause a Denial of Service, so these versions are considered not affected by this issue in such a way that it would be cause for concern, and the severity is therefore considered low. |
| CVE-2022-37436 | Medium | 2023-01-17 | Not applicable | Forecast only | Prior to Apache HTTP Server 2.4.55, a malicious backend can cause the response headers to be truncated early, resulting in some headers being incorporated into the response body. If the later headers have any security purpose, they will not be interpreted by the client. |
| CVE-2021-44832 | Medium | 2021-12-28 | Protected by Waratek | Exploited | Apache Log4j2 versions 2.0-beta7 through 2.17.0 (excluding security fix releases 2.3.2 and 2.12.4) are vulnerable to a remote code execution (RCE) attack when a configuration uses a JDBC Appender with a JNDI LDAP data source URI when an attacker has control of the target LDAP server. This issue is fixed by limiting JNDI data source names to the java protocol in Log4j2 versions 2.17.1, 2.12.4, and 2.3.2. |
| CVE-2021-45105 | Medium | 2021-12-18 | Protected by Waratek | Exploited | Apache Log4j2 versions 2.0-alpha1 through 2.16.0 (excluding 2.12.3 and 2.3.1) did not protect from uncontrolled recursion from self-referential lookups. This allows an attacker with control over Thread Context Map data to cause a denial of service when a crafted string is interpreted. This issue was fixed in Log4j 2.17.0, 2.12.3, and 2.3.1. |
| CVE-2021-34429 | Medium | 2021-07-15 | Protected by Waratek | Exploited | For Eclipse Jetty versions 9.4.37-9.4.42, 10.0.1-10.0.5 & 11.0.1-11.0.5, URIs can be crafted using some encoded characters to access the content of the WEB-INF directory and/or bypass some security constraints. This is a variation of the vulnerability reported in CVE-2021-28164/GHSA-v7ff-8wcx-gmc5. |
| CVE-2020-13947 | Medium | 2021-02-08 | No exploit published | Forecast only | An instance of a cross-site scripting vulnerability was identified to be present in the web based administration console on the message.jsp page of Apache ActiveMQ versions 5.15.12 through 5.16.0. |