
Oracle Critical Patch Update January 2023
Released January 2023 · Oracle's advisory ↗ · ← Critical Patch Update, October 2022 · Critical Patch Update, April 2023 →
183 CVEs in this release, one square each
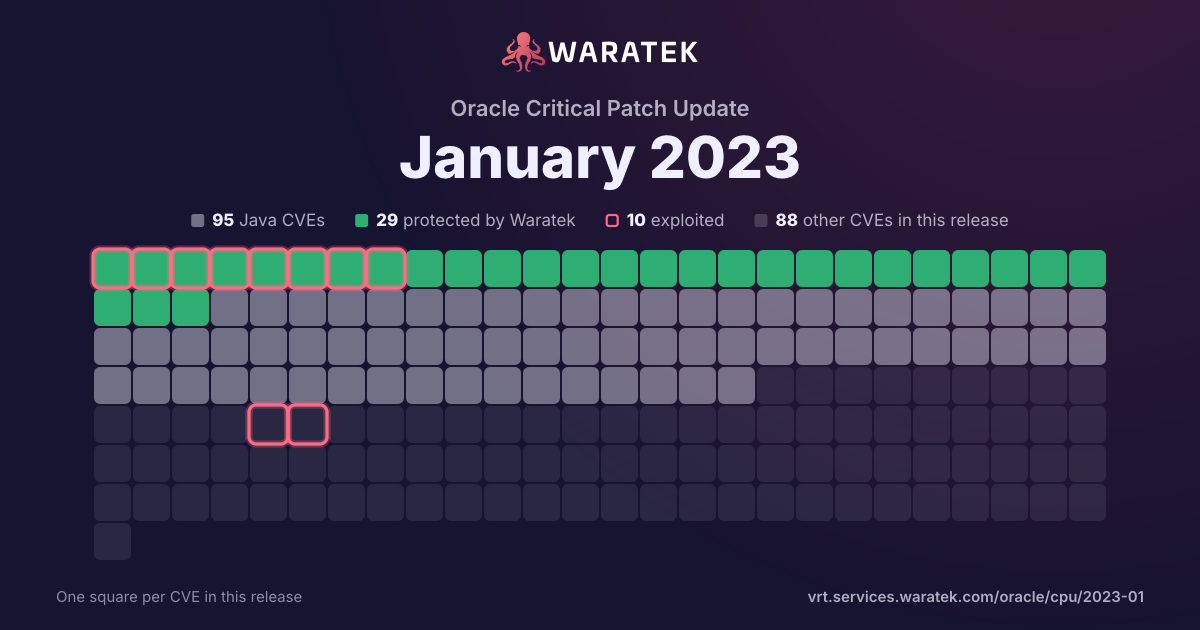
By status
29Protected by Waratek4Mitigation candidate62No exploit published13Outside Waratek scope74Not applicable1Withdrawn CVE
10Exploited, marked by the ring
No exploit published. For 39 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 7 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
7matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
7
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
7
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
3
42.9%
Forecast only
0
0.0%
No public exploit
4
57.1%
split by
peak 2 / month
Nov 211
Not applicable1
Critical1
not blocked1
No public exploit1
Dec 210
Jan 220
Feb 222
Not applicable2
Critical2
not blocked2
Proof of concept only1
No public exploit1
Mar 220
Apr 221
Not applicable1
Critical1
not blocked1
No public exploit1
May 220
Jun 221
Not applicable1
Critical1
not blocked1
No public exploit1
Jul 220
Aug 220
Sep 220
Oct 221
Not applicable1
Critical1
not blocked1
Proof of concept only1
Nov 220
Dec 221
Not applicable1
Critical1
not blocked1
Proof of concept only1
Dec 21Feb 22Apr 22Jun 22Aug 22Oct 22Dec 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-32221 | Critical | 2022-12-05 | Not applicable | Proof of concept only | When doing HTTP(S) transfers, libcurl might erroneously use the read callback (`CURLOPT_READFUNCTION`) to ask for data to send, even when the `CURLOPT_POSTFIELDS` option has been set, if the same handle previously was used to issue a `PUT` request which used that callback. This flaw may surprise the application and cause it to misbehave and either send off the wrong data or use memory after free or similar in the subsequent `POST` request. The problem exists in the logic for a reused handle when it is changed from a PUT to a POST. |
| CVE-2022-37454 | Critical | 2022-10-21 | Not applicable | Proof of concept only | The Keccak XKCP SHA-3 reference implementation before fdc6fef has an integer overflow and resultant buffer overflow that allows attackers to execute arbitrary code or eliminate expected cryptographic properties. This occurs in the sponge function interface. |
| CVE-2022-31813 | Critical | 2022-06-09 | Not applicable | No public exploit | Apache HTTP Server 2.4.53 and earlier may not send the X-Forwarded-* headers to the origin server based on client side Connection header hop-by-hop mechanism. This may be used to bypass IP based authentication on the origin server/application. |
| CVE-2022-27404 | Critical | 2022-04-22 | Not applicable | No public exploit | FreeType commit 1e2eb65048f75c64b68708efed6ce904c31f3b2f was discovered to contain a heap buffer overflow via the function sfnt_init_face. |
| CVE-2022-25315 | Critical | 2022-02-18 | Not applicable | Proof of concept only | In Expat (aka libexpat) before 2.4.5, there is an integer overflow in storeRawNames. |
| CVE-2022-25236 | Critical | 2022-02-16 | Not applicable | No public exploit | xmlparse.c in Expat (aka libexpat) before 2.4.5 allows attackers to insert namespace-separator characters into namespace URIs. |
| CVE-2021-3918 | Critical | 2021-11-13 | Not applicable | No public exploit | json-schema is vulnerable to Improperly Controlled Modification of Object Prototype Attributes ('Prototype Pollution') |