
Oracle Critical Patch Update January 2023
Released January 2023 · Oracle's advisory ↗ · ← Critical Patch Update, October 2022 · Critical Patch Update, April 2023 →
183 CVEs in this release, one square each
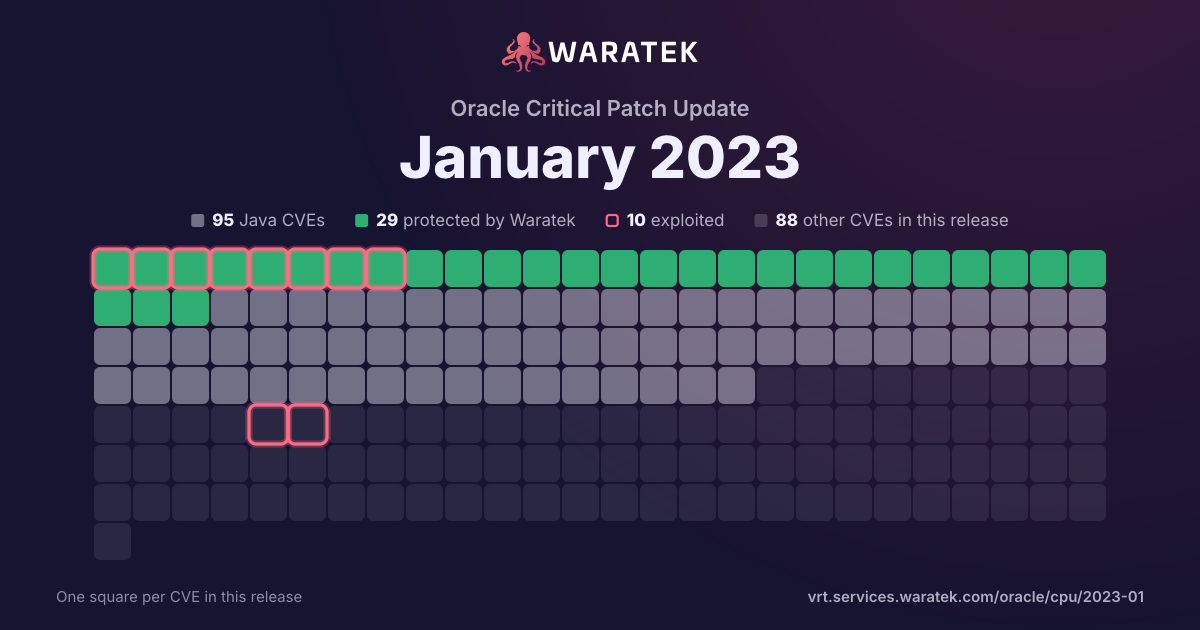
By status
29Protected by Waratek4Mitigation candidate62No exploit published13Outside Waratek scope74Not applicable1Withdrawn CVE
10Exploited, marked by the ring
No exploit published. For 39 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 13 matches · 7 in Waratek scope · 4 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
13matches
7in Waratek scope53.8%
4protected30.8%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
4
30.8%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
3
23.1%
Outside Waratek scope
2
15.4%
Not applicable
4
30.8%
Withdrawn CVE
0
0.0%
blocked by ARMR today
4
30.8%
partly blocked
0
0.0%
not blocked
9
69.2%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
13
100.0%
split by
peak 3 / quarter
Q1 181
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q2 180
Q3 180
Q4 180
Q1 190
Q2 190
Q3 190
Q4 190
Q1 200
Q2 201
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q3 200
Q4 200
Q1 211
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q2 210
Q3 210
Q4 211
Not applicable1
Critical1
not blocked1
No public exploit1
Q1 221
Not applicable1
Critical1
not blocked1
No public exploit1
Q2 223
Protected by Waratek1
Not applicable2
Critical3
blocked by ARMR today1
not blocked2
No public exploit3
Q3 221
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q4 223
Protected by Waratek1
No exploit published2
Critical3
blocked by ARMR today1
not blocked2
No public exploit3
Q1 231
No exploit published1
Critical1
not blocked1
No public exploit1
Q1 18Q3 18Q1 19Q3 19Q1 20Q3 20Q1 21Q3 21Q1 22Q3 22Q1 23
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2023-21890 | Critical | 2023-01-18 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Converged Application Server product of Oracle Communications (component: Core). Supported versions that are affected are 7.1.0 and 8.0.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via UDP to compromise Oracle Communications Converged Application Server. Successful attacks of this vulnerability can result in takeover of Oracle Communications Converged Application Server. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2022-42920 | Critical | 2022-11-07 | Protected by Waratek | No public exploit | Apache Commons BCEL has a number of APIs that would normally only allow changing specific class characteristics. However, due to an out-of-bounds writing issue, these APIs can be used to produce arbitrary bytecode. This could be abused in applications that pass attacker-controllable data to those APIs, giving the attacker more control over the resulting bytecode than otherwise expected. Update to Apache Commons BCEL 6.6.0. |
| CVE-2022-43403 | Critical | 2022-10-19 | No exploit published | No public exploit | A sandbox bypass vulnerability involving casting an array-like value to an array type in Jenkins Script Security Plugin 1183.v774b_0b_0a_a_451 and earlier allows attackers with permission to define and run sandboxed scripts, including Pipelines, to bypass the sandbox protection and execute arbitrary code in the context of the Jenkins controller JVM. |
| CVE-2022-40664 | Critical | 2022-10-12 | No exploit published | No public exploit | Apache Shiro before 1.10.0, Authentication Bypass Vulnerability in Shiro when forwarding or including via RequestDispatcher. |
| CVE-2022-2526 | Critical | 2022-09-09 | Outside Waratek scope | No public exploit | A use-after-free vulnerability was found in systemd. This issue occurs due to the on_stream_io() function and dns_stream_complete() function in 'resolved-dns-stream.c' not incrementing the reference counting for the DnsStream object. Therefore, other functions and callbacks called can dereference the DNSStream object, causing the use-after-free when the reference is still used later. |
| CVE-2021-41411 | Critical | 2022-06-16 | Protected by Waratek | No public exploit | drools <=7.59.x is affected by an XML External Entity (XXE) vulnerability in KieModuleMarshaller.java. The Validator class is not used correctly, resulting in the XXE injection vulnerability. |
| CVE-2022-31813 | Critical | 2022-06-09 | Not applicable | No public exploit | Apache HTTP Server 2.4.53 and earlier may not send the X-Forwarded-* headers to the origin server based on client side Connection header hop-by-hop mechanism. This may be used to bypass IP based authentication on the origin server/application. |
| CVE-2022-27404 | Critical | 2022-04-22 | Not applicable | No public exploit | FreeType commit 1e2eb65048f75c64b68708efed6ce904c31f3b2f was discovered to contain a heap buffer overflow via the function sfnt_init_face. |
| CVE-2022-25236 | Critical | 2022-02-16 | Not applicable | No public exploit | xmlparse.c in Expat (aka libexpat) before 2.4.5 allows attackers to insert namespace-separator characters into namespace URIs. |
| CVE-2021-3918 | Critical | 2021-11-13 | Not applicable | No public exploit | json-schema is vulnerable to Improperly Controlled Modification of Object Prototype Attributes ('Prototype Pollution') |
| CVE-2020-36242 | Critical | 2021-02-07 | Outside Waratek scope | No public exploit | In the cryptography package before 3.3.2 for Python, certain sequences of update calls to symmetrically encrypt multi-GB values could result in an integer overflow and buffer overflow, as demonstrated by the Fernet class. |
| CVE-2020-10683 | Critical | 2020-05-01 | Protected by Waratek | No public exploit | dom4j before 2.0.3 and 2.1.x before 2.1.3 allows external DTDs and External Entities by default, which might enable XXE attacks. However, there is popular external documentation from OWASP showing how to enable the safe, non-default behavior in any application that uses dom4j. |
| CVE-2018-7489 | Critical | 2018-02-26 | Protected by Waratek | No public exploit | FasterXML jackson-databind before 2.7.9.3, 2.8.x before 2.8.11.1 and 2.9.x before 2.9.5 allows unauthenticated remote code execution because of an incomplete fix for the CVE-2017-7525 deserialization flaw. This is exploitable by sending maliciously crafted JSON input to the readValue method of the ObjectMapper, bypassing a blacklist that is ineffective if the c3p0 libraries are available in the classpath. |