
Oracle Critical Patch Update January 2023
Released January 2023 · Oracle's advisory ↗ · ← Critical Patch Update, October 2022 · Critical Patch Update, April 2023 →
183 CVEs in this release, one square each
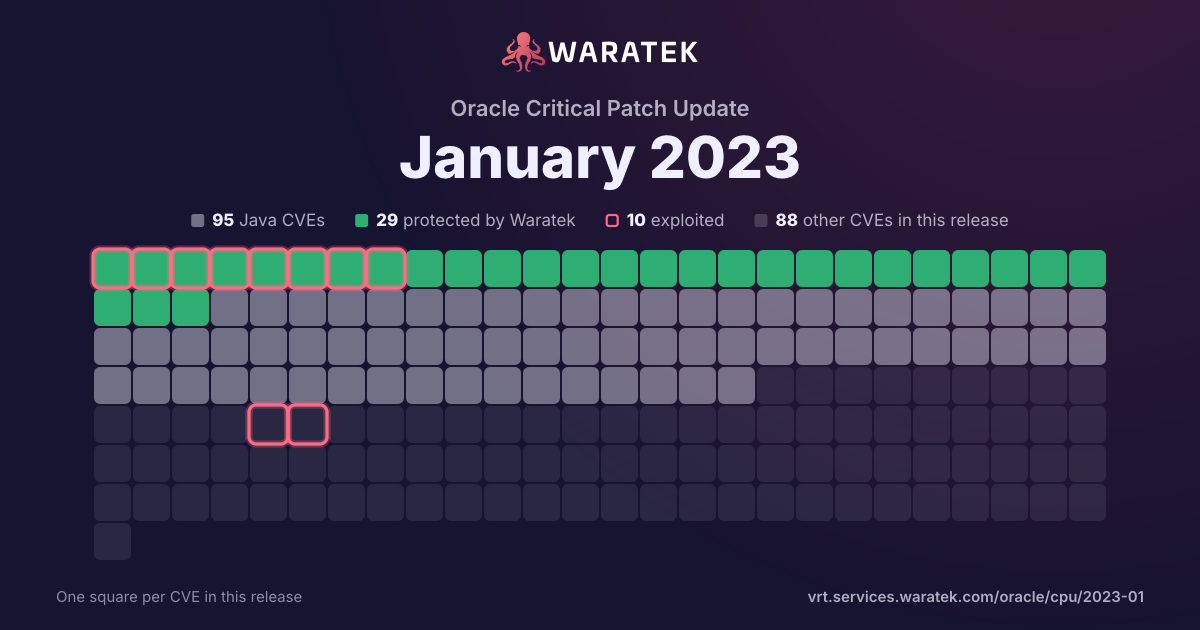
By status
29Protected by Waratek4Mitigation candidate62No exploit published13Outside Waratek scope74Not applicable1Withdrawn CVE
10Exploited, marked by the ring
No exploit published. For 39 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 2 CISA KEV
4matches
2CISA KEV50.0%
Protected by Waratek
4
100.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
blocked by ARMR today
4
100.0%
partly blocked
0
0.0%
not blocked
0
0.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
4
100.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 2 / quarter
Q2 181
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q3 180
Q4 180
Q1 190
Q2 190
Q3 190
Q4 190
Q1 200
Q2 200
Q3 200
Q4 200
Q1 210
Q2 210
Q3 210
Q4 210
Q1 220
Q2 222
Protected by Waratek2
Critical2
blocked by ARMR today2
Exploited2
Q3 220
Q4 221
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q2 18Q4 18Q2 19Q4 19Q2 20Q4 20Q2 21Q4 21Q2 22Q4 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-42889 | Critical | 2022-10-13 | Protected by Waratek | Exploited | Apache Commons Text performs variable interpolation, allowing properties to be dynamically evaluated and expanded. The standard format for interpolation is "${prefix:name}", where "prefix" is used to locate an instance of org.apache.commons.text.lookup.StringLookup that performs the interpolation. Starting with version 1.5 and continuing through 1.9, the set of default Lookup instances included interpolators that could result in arbitrary code execution or contact with remote servers. These lookups are: - "script" - execute expressions using the JVM script execution engine (javax.script) - "dns" - resolve dns records - "url" - load values from urls, including from remote servers Applications using the interpolation defaults in the affected versions may be vulnerable to remote code execution or unintentional contact with remote servers if untrusted configuration values are used. Users are recommended to upgrade to Apache Commons Text 1.10.0, which disables the problematic interpolators by default. |
| CVE-2021-31805 | Critical | 2022-04-12 | Protected by Waratek | Exploited | The fix issued for CVE-2020-17530 was incomplete. So from Apache Struts 2.0.0 to 2.5.29, still some of the tag’s attributes could perform a double evaluation if a developer applied forced OGNL evaluation by using the %{...} syntax. Using forced OGNL evaluation on untrusted user input can lead to a Remote Code Execution and security degradation. |
| CVE-2022-22965 | Critical | 2022-04-01 | Protected by Waratek | Exploited | A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit requires the application to run on Tomcat as a WAR deployment. If the application is deployed as a Spring Boot executable jar, i.e. the default, it is not vulnerable to the exploit. However, the nature of the vulnerability is more general, and there may be other ways to exploit it. |
| CVE-2018-1273 | Critical | 2018-04-11 | Protected by Waratek | Exploited | Spring Data Commons, versions prior to 1.13 to 1.13.10, 2.0 to 2.0.5, and older unsupported versions, contain a property binder vulnerability caused by improper neutralization of special elements. An unauthenticated remote malicious user (or attacker) can supply specially crafted request parameters against Spring Data REST backed HTTP resources or using Spring Data's projection-based request payload binding hat can lead to a remote code execution attack. |