
Oracle Critical Patch Update October 2022
Released October 2022 · Oracle's advisory ↗ · ← Critical Patch Update, July 2022 · Critical Patch Update, January 2023 →
179 CVEs in this release, one square each
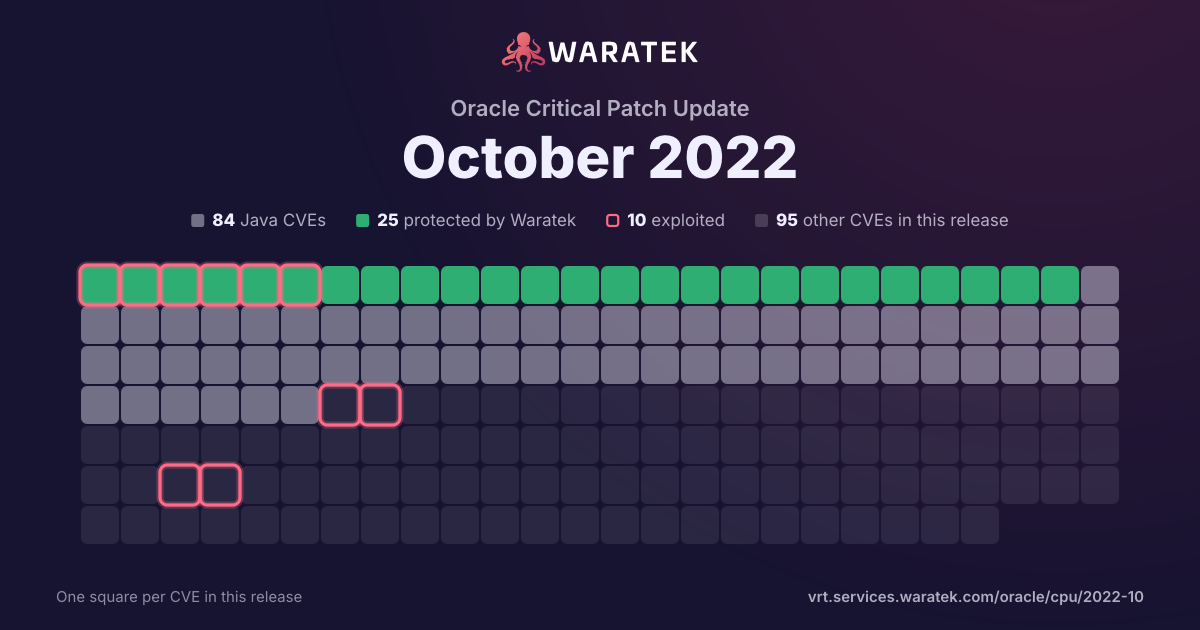
By status
25Protected by Waratek4Mitigation candidate55No exploit published48Outside Waratek scope47Not applicable
10Exploited, marked by the ring
No exploit published. For 33 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 1 EPSS ≥ 0.5
6matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
1EPSS ≥ 0.516.7%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
6
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
6
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
16.7%
Forecast only
1
16.7%
No public exploit
4
66.7%
split by
peak 3 / quarter
Q1 191
Not applicable1
Critical1
not blocked1
No public exploit1
Q2 190
Q3 190
Q4 190
Q1 200
Q2 200
Q3 200
Q4 200
Q1 210
Q2 210
Q3 210
Q4 211
Not applicable1
Critical1
not blocked1
No public exploit1
Q1 223
Not applicable3
Critical3
not blocked3
Proof of concept only1
Forecast only1
No public exploit1
Q2 221
Not applicable1
Critical1
not blocked1
No public exploit1
Q2 19Q4 19Q2 20Q4 20Q2 21Q4 21Q2 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-31813 | Critical | 2022-06-09 | Not applicable | No public exploit | Apache HTTP Server 2.4.53 and earlier may not send the X-Forwarded-* headers to the origin server based on client side Connection header hop-by-hop mechanism. This may be used to bypass IP based authentication on the origin server/application. |
| CVE-2022-23943 | Critical | 2022-03-14 | Not applicable | Forecast only | Out-of-bounds Write vulnerability in mod_sed of Apache HTTP Server allows an attacker to overwrite heap memory with possibly attacker provided data. This issue affects Apache HTTP Server 2.4 version 2.4.52 and prior versions. |
| CVE-2021-21708 | Critical | 2022-02-27 | Not applicable | No public exploit | In PHP versions 7.4.x below 7.4.28, 8.0.x below 8.0.16, and 8.1.x below 8.1.3, when using filter functions with FILTER_VALIDATE_FLOAT filter and min/max limits, if the filter fails, there is a possibility to trigger use of allocated memory after free, which can result it crashes, and potentially in overwrite of other memory chunks and RCE. This issue affects: code that uses FILTER_VALIDATE_FLOAT with min/max limits. |
| CVE-2022-25315 | Critical | 2022-02-18 | Not applicable | Proof of concept only | In Expat (aka libexpat) before 2.4.5, there is an integer overflow in storeRawNames. |
| CVE-2021-3918 | Critical | 2021-11-13 | Not applicable | No public exploit | json-schema is vulnerable to Improperly Controlled Modification of Object Prototype Attributes ('Prototype Pollution') |
| CVE-2019-3862 | Critical | 2019-03-21 | Not applicable | No public exploit | An out of bounds read flaw was discovered in libssh2 before 1.8.1 in the way SSH_MSG_CHANNEL_REQUEST packets with an exit status message and no payload are parsed. A remote attacker who compromises a SSH server may be able to cause a Denial of Service or read data in the client memory. |