
Oracle Critical Patch Update October 2022
Released October 2022 · Oracle's advisory ↗ · ← Critical Patch Update, July 2022 · Critical Patch Update, January 2023 →
179 CVEs in this release, one square each
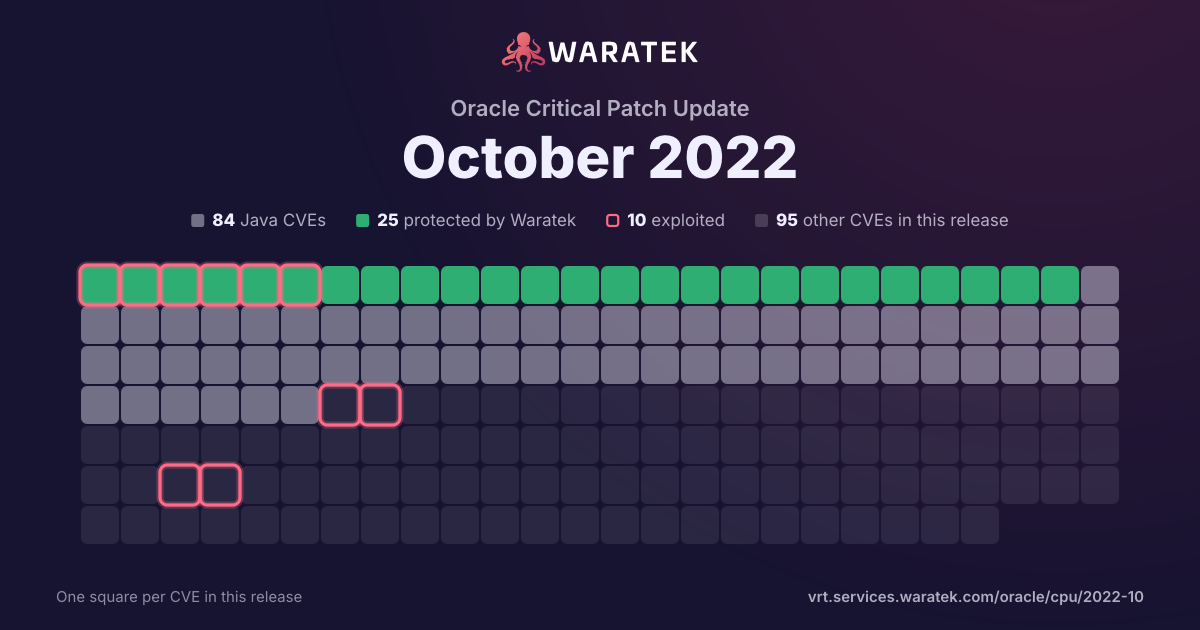
By status
25Protected by Waratek4Mitigation candidate55No exploit published48Outside Waratek scope47Not applicable
10Exploited, marked by the ring
No exploit published. For 33 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 3 in Waratek scope · 3 protected · 0 CISA KEV · 3 public PoC · 3 EPSS ≥ 0.5
Protected by Waratek
3
60.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
2
40.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
3
60.0%
partly blocked
0
0.0%
not blocked
2
40.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
5
100.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / quarter
Q2 201
Outside Waratek scope1
Medium1
not blocked1
Exploited1
Q3 200
Q4 200
Q1 210
Q2 210
Q3 211
Protected by Waratek1
Medium1
blocked by ARMR today1
Exploited1
Q4 211
Protected by Waratek1
Medium1
blocked by ARMR today1
Exploited1
Q1 220
Q2 221
Protected by Waratek1
Medium1
blocked by ARMR today1
Exploited1
Q3 220
Q4 221
Outside Waratek scope1
Medium1
not blocked1
Exploited1
Q2 20Q3 20Q4 20Q1 21Q2 21Q3 21Q4 21Q1 22Q2 22Q3 22Q4 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-21589 | Medium | 2022-10-18 | Outside Waratek scope | Exploited | Vulnerability in the MySQL Server product of Oracle MySQL (component: Server: Security: Privileges). Supported versions that are affected are 5.7.39 and prior and 8.0.16 and prior. Easily exploitable vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized read access to a subset of MySQL Server accessible data. CVSS 3.1 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2022-34305 | Medium | 2022-06-23 | Protected by Waratek | Exploited | In Apache Tomcat 10.1.0-M1 to 10.1.0-M16, 10.0.0-M1 to 10.0.22, 9.0.30 to 9.0.64 and 8.5.50 to 8.5.81 the Form authentication example in the examples web application displayed user provided data without filtering, exposing a XSS vulnerability. |
| CVE-2021-44832 | Medium | 2021-12-28 | Protected by Waratek | Exploited | Apache Log4j2 versions 2.0-beta7 through 2.17.0 (excluding security fix releases 2.3.2 and 2.12.4) are vulnerable to a remote code execution (RCE) attack when a configuration uses a JDBC Appender with a JNDI LDAP data source URI when an attacker has control of the target LDAP server. This issue is fixed by limiting JNDI data source names to the java protocol in Log4j2 versions 2.17.1, 2.12.4, and 2.3.2. |
| CVE-2021-34429 | Medium | 2021-07-15 | Protected by Waratek | Exploited | For Eclipse Jetty versions 9.4.37-9.4.42, 10.0.1-10.0.5 & 11.0.1-11.0.5, URIs can be crafted using some encoded characters to access the content of the WEB-INF directory and/or bypass some security constraints. This is a variation of the vulnerability reported in CVE-2021-28164/GHSA-v7ff-8wcx-gmc5. |
| CVE-2020-11022 | Medium | 2020-04-29 | Outside Waratek scope | Exploited | In jQuery starting with 1.12.0 and before 3.5.0, passing HTML from untrusted sources - even after sanitizing it - to one of jQuery's DOM manipulation methods (i.e. .html(), .append(), and others) may execute untrusted code. This problem is patched in jQuery 3.5.0. |