
Oracle Critical Patch Update October 2022
Released October 2022 · Oracle's advisory ↗ · ← Critical Patch Update, July 2022 · Critical Patch Update, January 2023 →
179 CVEs in this release, one square each
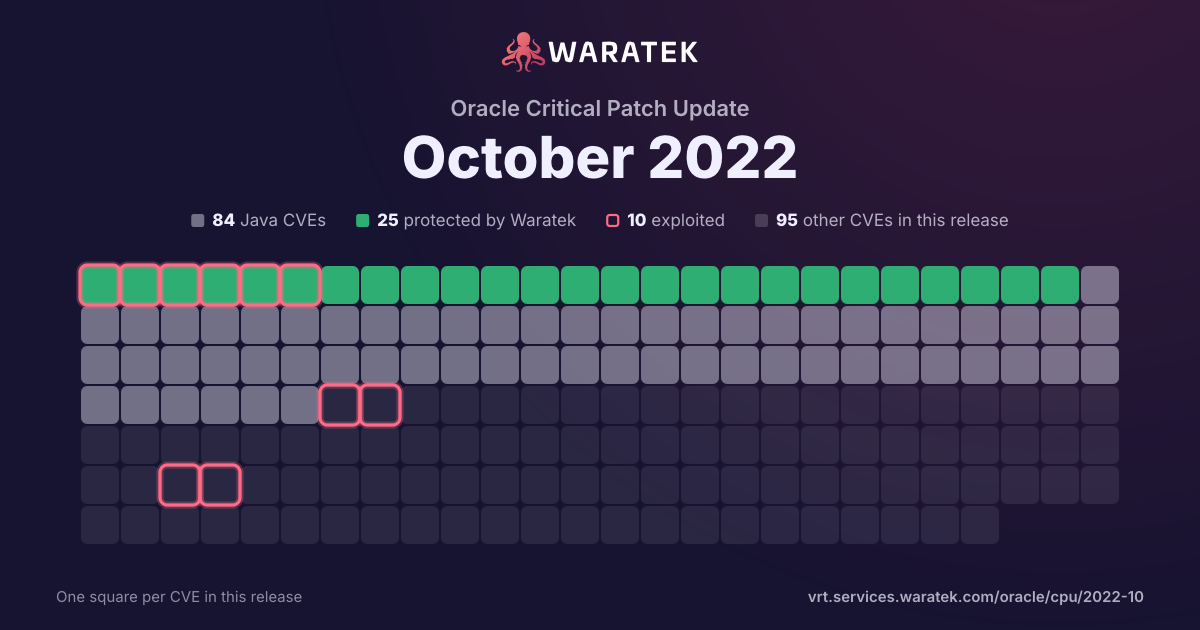
By status
25Protected by Waratek4Mitigation candidate55No exploit published48Outside Waratek scope47Not applicable
10Exploited, marked by the ring
No exploit published. For 33 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 2 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
2matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
100.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
2
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
2
100.0%
split by
peak 1 / month
Jun 22Jul 22Aug 22Sep 22Oct 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-39409 | Low | 2022-10-18 | No exploit published | No public exploit | Vulnerability in the Oracle Transportation Management product of Oracle Supply Chain (component: Business Process Automation). Supported versions that are affected are 6.4.3 and 6.5.1. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Transportation Management. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Transportation Management. CVSS 3.1 Base Score 2.7 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2022-33879 | Low | 2022-06-27 | No exploit published | No public exploit | The initial fixes in CVE-2022-30126 and CVE-2022-30973 for regexes in the StandardsExtractingContentHandler were insufficient, and we found a separate, new regex DoS in a different regex in the StandardsExtractingContentHandler. These are now fixed in 1.28.4 and 2.4.1. |