
Oracle Critical Patch Update July 2022
Released July 2022 · Oracle's advisory ↗ · ← Critical Patch Update, April 2022 · Critical Patch Update, October 2022 →
188 CVEs in this release, one square each
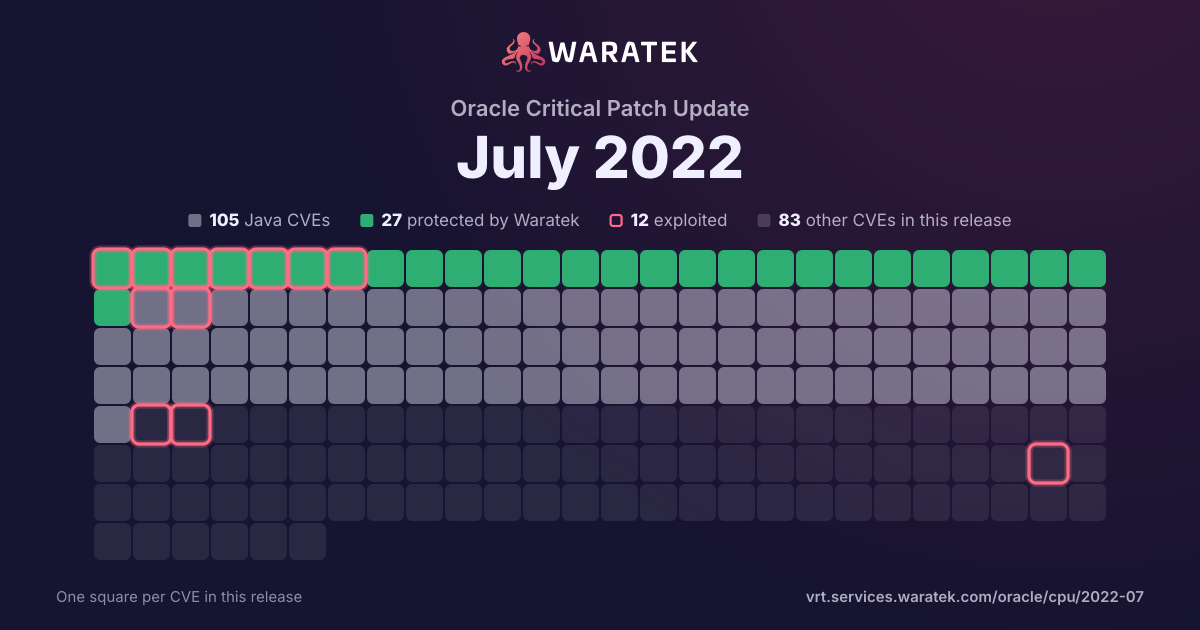
By status
27Protected by Waratek6Mitigation candidate72No exploit published49Outside Waratek scope34Not applicable
12Exploited, marked by the ring
No exploit published. For 47 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 34 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 1 EPSS ≥ 0.5
34matches
0in Waratek scope0.0%
0protected0.0%
1exploited2.9%
0CISA KEV0.0%
2public PoC5.9%
1EPSS ≥ 0.52.9%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
34
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
34
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
2.9%
Working exploit published
0
0.0%
Proof of concept only
2
5.9%
Forecast only
1
2.9%
No public exploit
30
88.2%
split by
peak 18 / quarter
Q2 191
Not applicable1
Medium1
not blocked1
No public exploit1
Q3 190
Q4 190
Q1 200
Q2 200
Q3 200
Q4 200
Q1 212
Not applicable2
High2
not blocked2
Exploited1
No public exploit1
Q2 210
Q3 213
Not applicable3
Critical1
High2
not blocked3
No public exploit3
Q4 212
Not applicable2
Medium2
not blocked2
No public exploit2
Q1 226
Not applicable6
High5
Medium1
not blocked6
Proof of concept only1
No public exploit5
Q2 222
Not applicable2
High2
not blocked2
Proof of concept only1
No public exploit1
Q3 2218
Not applicable18
High8
Medium8
Low2
not blocked18
Forecast only1
No public exploit17
Q3 19Q1 20Q3 20Q1 21Q3 21Q1 22Q3 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-1271 | High | 2022-08-31 | Not applicable | No public exploit | An arbitrary file write vulnerability was found in GNU gzip's zgrep utility. When zgrep is applied on the attacker's chosen file name (for example, a crafted file name), this can overwrite an attacker's content to an arbitrary attacker-selected file. This flaw occurs due to insufficient validation when processing filenames with two or more newlines where selected content and the target file names are embedded in crafted multi-line file names. This flaw allows a remote, low privileged attacker to force zgrep to write arbitrary files on the system. |
| CVE-2022-21571 | High | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle VM VirtualBox product of Oracle Virtualization (component: Core). The supported version that is affected is Prior to 6.1.36. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of Oracle VM VirtualBox. CVSS 3.1 Base Score 8.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2022-21565 | Medium | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Java VM component of Oracle Database Server. Supported versions that are affected are 12.1.0.2, 19c and 21c. Easily exploitable vulnerability allows low privileged attacker having Create Procedure privilege with network access via Oracle Net to compromise Java VM. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Java VM accessible data. CVSS 3.1 Base Score 6.5 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:H/A:N). |
| CVE-2022-21563 | Low | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle ZFS Storage Appliance Kit product of Oracle Systems (component: Core). The supported version that is affected is 8.8. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle ZFS Storage Appliance Kit executes to compromise Oracle ZFS Storage Appliance Kit. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle ZFS Storage Appliance Kit accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle ZFS Storage Appliance Kit. CVSS 3.1 Base Score 3.4 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:H/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2022-21558 | High | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle Crystal Ball product of Oracle Construction and Engineering (component: Installation). Supported versions that are affected are 11.1.2.0.000-11.1.2.4.900. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Crystal Ball executes to compromise Oracle Crystal Ball. While the vulnerability is in Oracle Crystal Ball, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of Oracle Crystal Ball. CVSS 3.1 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2022-21555 | Medium | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the MySQL Shell for VS Code product of Oracle MySQL (component: Shell: GUI). Supported versions that are affected are 1.1.8 and prior. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where MySQL Shell for VS Code executes to compromise MySQL Shell for VS Code. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in MySQL Shell for VS Code, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Shell for VS Code accessible data as well as unauthorized read access to a subset of MySQL Shell for VS Code accessible data. CVSS 3.1 Base Score 4.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2022-21554 | Medium | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle VM VirtualBox product of Oracle Virtualization (component: Core). The supported version that is affected is Prior to 6.1.36. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle VM VirtualBox. CVSS 3.1 Base Score 4.4 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2022-21551 | Medium | 2022-07-19 | Not applicable | No public exploit | Vulnerability in Oracle GoldenGate (component: Oracle GoldenGate). The supported version that is affected is 21c: prior to 21.7.0.0.0; 19c: prior to 19.1.0.0.220719. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle GoldenGate. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Oracle GoldenGate. CVSS 3.1 Base Score 6.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2022-21550 | Medium | 2022-07-19 | Not applicable | Forecast only | Vulnerability in the MySQL Cluster product of Oracle MySQL (component: Cluster: General). Supported versions that are affected are 7.4.36 and prior, 7.5.26 and prior, 7.6.22 and prior and and 8.0.29 and prior. Difficult to exploit vulnerability allows high privileged attacker with access to the physical communication segment attached to the hardware where the MySQL Cluster executes to compromise MySQL Cluster. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of MySQL Cluster. CVSS 3.1 Base Score 6.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:A/AC:H/PR:H/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2022-21535 | Low | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the MySQL Shell product of Oracle MySQL (component: Shell: General/Core Client). Supported versions that are affected are 8.0.28 and prior. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where MySQL Shell executes to compromise MySQL Shell. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of MySQL Shell. CVSS 3.1 Base Score 2.5 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:N/UI:R/S:U/C:N/I:N/A:L). |
| CVE-2022-21533 | Medium | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle Solaris product of Oracle Systems (component: SMB Server). The supported version that is affected is 11. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Solaris executes to compromise Oracle Solaris. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Solaris. CVSS 3.1 Base Score 5.5 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2022-21524 | High | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle Solaris product of Oracle Systems (component: Filesystem). The supported version that is affected is 11. Easily exploitable vulnerability allows low privileged attacker with network access via SMB to compromise Oracle Solaris. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Solaris as well as unauthorized update, insert or delete access to some of Oracle Solaris accessible data and unauthorized read access to a subset of Oracle Solaris accessible data. CVSS 3.1 Base Score 7.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:H). |
| CVE-2022-21519 | Medium | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the MySQL Cluster product of Oracle MySQL (component: Cluster: General). Supported versions that are affected are 8.0.29 and prior. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise MySQL Cluster. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Cluster. CVSS 3.1 Base Score 5.9 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2022-21514 | High | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle Solaris product of Oracle Systems (component: Remote Administration Daemon). The supported version that is affected is 11. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Oracle Solaris. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Solaris. CVSS 3.1 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2022-21513 | High | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle ZFS Storage Appliance Kit product of Oracle Systems (component: Core). The supported version that is affected is 8.8. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle ZFS Storage Appliance Kit executes to compromise Oracle ZFS Storage Appliance Kit. While the vulnerability is in Oracle ZFS Storage Appliance Kit, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of Oracle ZFS Storage Appliance Kit. CVSS 3.1 Base Score 8.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2022-21511 | High | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle Database - Enterprise Edition Recovery component of Oracle Database Server. For supported versions that are affected see note. Easily exploitable vulnerability allows high privileged attacker having EXECUTE ON DBMS_IR.EXECUTESQLSCRIPT privilege with network access via Oracle Net to compromise Oracle Database - Enterprise Edition Recovery. Successful attacks of this vulnerability can result in takeover of Oracle Database - Enterprise Edition Recovery. Note: None of the supported versions are affected. CVSS 3.1 Base Score 7.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2022-21510 | High | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle Database - Enterprise Edition Sharding component of Oracle Database Server. For supported versions that are affected see note. Easily exploitable vulnerability allows low privileged attacker having Local Logon privilege with logon to the infrastructure where Oracle Database - Enterprise Edition Sharding executes to compromise Oracle Database - Enterprise Edition Sharding. While the vulnerability is in Oracle Database - Enterprise Edition Sharding, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of Oracle Database - Enterprise Edition Sharding. Note: None of the supported versions are affected. CVSS 3.1 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2022-21439 | Medium | 2022-07-19 | Not applicable | No public exploit | Vulnerability in the Oracle Solaris product of Oracle Systems (component: Kernel). Supported versions that are affected are 10 and 11. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle Solaris executes to compromise Oracle Solaris. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Solaris. CVSS 3.1 Base Score 4.2 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:H/UI:R/S:U/C:N/I:N/A:H). |
| CVE-2022-24735 | High | 2022-04-27 | Not applicable | Proof of concept only | Redis is an in-memory database that persists on disk. By exploiting weaknesses in the Lua script execution environment, an attacker with access to Redis prior to version 7.0.0 or 6.2.7 can inject Lua code that will execute with the (potentially higher) privileges of another Redis user. The Lua script execution environment in Redis provides some measures that prevent a script from creating side effects that persist and can affect the execution of the same, or different script, at a later time. Several weaknesses of these measures have been publicly known for a long time, but they had no security impact as the Redis security model did not endorse the concept of users or privileges. With the introduction of ACLs in Redis 6.0, these weaknesses can be exploited by a less privileged users to inject Lua code that will execute at a later time, when a privileged user executes a Lua script. The problem is fixed in Redis versions 7.0.0 and 6.2.7. An additional workaround to mitigate this problem without patching the redis-server executable, if Lua scripting is not being used, is to block access to `SCRIPT LOAD` and `EVAL` commands using ACL rules. |
| CVE-2022-24801 | High | 2022-04-04 | Not applicable | No public exploit | Twisted is an event-based framework for internet applications, supporting Python 3.6+. Prior to version 22.4.0rc1, the Twisted Web HTTP 1.1 server, located in the `twisted.web.http` module, parsed several HTTP request constructs more leniently than permitted by RFC 7230. This non-conformant parsing can lead to desync if requests pass through multiple HTTP parsers, potentially resulting in HTTP request smuggling. Users who may be affected use Twisted Web's HTTP 1.1 server and/or proxy and also pass requests through a different HTTP server and/or proxy. The Twisted Web client is not affected. The HTTP 2.0 server uses a different parser, so it is not affected. The issue has been addressed in Twisted 22.4.0rc1. Two workarounds are available: Ensure any vulnerabilities in upstream proxies have been addressed, such as by upgrading them; or filter malformed requests by other means, such as configuration of an upstream proxy. |
| CVE-2022-1154 | High | 2022-03-30 | Not applicable | No public exploit | Use after free in utf_ptr2char in GitHub repository vim/vim prior to 8.2.4646. |
| CVE-2022-23308 | High | 2022-02-26 | Not applicable | No public exploit | valid.c in libxml2 before 2.9.13 has a use-after-free of ID and IDREF attributes. |
| CVE-2022-25636 | High | 2022-02-24 | Not applicable | Proof of concept only | net/netfilter/nf_dup_netdev.c in the Linux kernel 5.4 through 5.6.10 allows local users to gain privileges because of a heap out-of-bounds write. This is related to nf_tables_offload. |
| CVE-2022-21824 | High | 2022-02-24 | Not applicable | No public exploit | Due to the formatting logic of the "console.table()" function it was not safe to allow user controlled input to be passed to the "properties" parameter while simultaneously passing a plain object with at least one property as the first parameter, which could be "__proto__". The prototype pollution has very limited control, in that it only allows an empty string to be assigned to numerical keys of the object prototype.Node.js >= 12.22.9, >= 14.18.3, >= 16.13.2, and >= 17.3.1 use a null protoype for the object these properties are being assigned to. |
| CVE-2022-23632 | High | 2022-02-17 | Not applicable | No public exploit | Traefik is an HTTP reverse proxy and load balancer. Prior to version 2.6.1, Traefik skips the router transport layer security (TLS) configuration when the host header is a fully qualified domain name (FQDN). For a request, the TLS configuration choice can be different than the router choice, which implies the use of a wrong TLS configuration. When sending a request using FQDN handled by a router configured with a dedicated TLS configuration, the TLS configuration falls back to the default configuration that might not correspond to the configured one. If the CNAME flattening is enabled, the selected TLS configuration is the SNI one and the routing uses the CNAME value, so this can skip the expected TLS configuration. Version 2.6.1 contains a patch for this issue. As a workaround, one may add the FDQN to the host rule. However, there is no workaround if the CNAME flattening is enabled. |
| CVE-2021-45943 | Medium | 2022-01-01 | Not applicable | No public exploit | GDAL 3.3.0 through 3.4.0 has a heap-based buffer overflow in PCIDSK::CPCIDSKFile::ReadFromFile (called from PCIDSK::CPCIDSKSegment::ReadFromFile and PCIDSK::CPCIDSKBinarySegment::CPCIDSKBinarySegment). |
| CVE-2021-34141 | Medium | 2021-12-17 | Not applicable | No public exploit | An incomplete string comparison in the numpy.core component in NumPy before 1.22.0 allows attackers to trigger slightly incorrect copying by constructing specific string objects. NOTE: the vendor states that this reported code behavior is "completely harmless." |
| CVE-2021-3572 | Medium | 2021-11-10 | Not applicable | No public exploit | A flaw was found in python-pip in the way it handled Unicode separators in git references. A remote attacker could possibly use this issue to install a different revision on a repository. The highest threat from this vulnerability is to data integrity. This is fixed in python-pip version 21.1. |
| CVE-2021-3749 | High | 2021-08-31 | Not applicable | No public exploit | axios is vulnerable to Inefficient Regular Expression Complexity |
| CVE-2021-35940 | High | 2021-08-23 | Not applicable | No public exploit | An out-of-bounds array read in the apr_time_exp*() functions was fixed in the Apache Portable Runtime 1.6.3 release (CVE-2017-12613). The fix for this issue was not carried forward to the APR 1.7.x branch, and hence version 1.7.0 regressed compared to 1.6.3 and is vulnerable to the same issue. |
| CVE-2021-22931 | Critical | 2021-08-16 | Not applicable | No public exploit | Node.js before 16.6.0, 14.17.4, and 12.22.4 is vulnerable to Remote Code Execution, XSS, Application crashes due to missing input validation of host names returned by Domain Name Servers in Node.js dns library which can lead to output of wrong hostnames (leading to Domain Hijacking) and injection vulnerabilities in applications using the library. |
| CVE-2021-3450 | High | 2021-03-25 | Not applicable | No public exploit | The X509_V_FLAG_X509_STRICT flag enables additional security checks of the certificates present in a certificate chain. It is not set by default. Starting from OpenSSL version 1.1.1h a check to disallow certificates in the chain that have explicitly encoded elliptic curve parameters was added as an additional strict check. An error in the implementation of this check meant that the result of a previous check to confirm that certificates in the chain are valid CA certificates was overwritten. This effectively bypasses the check that non-CA certificates must not be able to issue other certificates. If a "purpose" has been configured then there is a subsequent opportunity for checks that the certificate is a valid CA. All of the named "purpose" values implemented in libcrypto perform this check. Therefore, where a purpose is set the certificate chain will still be rejected even when the strict flag has been used. A purpose is set by default in libssl client and server certificate verification routines, but it can be overridden or removed by an application. In order to be affected, an application must explicitly set the X509_V_FLAG_X509_STRICT verification flag and either not set a purpose for the certificate verification or, in the case of TLS client or server applications, override the default purpose. OpenSSL versions 1.1.1h and newer are affected by this issue. Users of these versions should upgrade to OpenSSL 1.1.1k. OpenSSL 1.0.2 is not impacted by this issue. Fixed in OpenSSL 1.1.1k (Affected 1.1.1h-1.1.1j). |
| CVE-2021-23337 | High | 2021-02-15 | Not applicable | Exploited | Lodash versions prior to 4.17.21 are vulnerable to Command Injection via the template function. |
| CVE-2019-0220 | Medium | 2019-06-11 | Not applicable | No public exploit | A vulnerability was found in Apache HTTP Server 2.4.0 to 2.4.38. When the path component of a request URL contains multiple consecutive slashes ('/'), directives such as LocationMatch and RewriteRule must account for duplicates in regular expressions while other aspects of the servers processing will implicitly collapse them. |