
Oracle Critical Patch Update July 2022
Released July 2022 · Oracle's advisory ↗ · ← Critical Patch Update, April 2022 · Critical Patch Update, October 2022 →
188 CVEs in this release, one square each
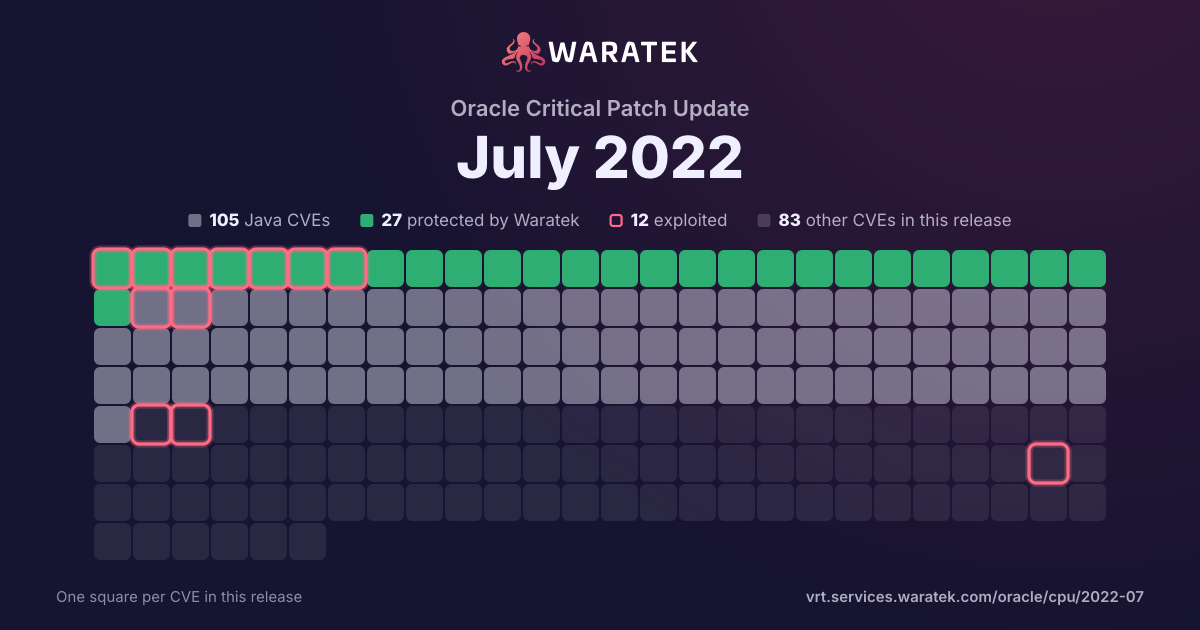
By status
27Protected by Waratek6Mitigation candidate72No exploit published49Outside Waratek scope34Not applicable
12Exploited, marked by the ring
No exploit published. For 47 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 10 matches · 1 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
Protected by Waratek
10
100.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
blocked by ARMR today
10
100.0%
partly blocked
0
0.0%
not blocked
0
0.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
10.0%
Working exploit published
0
0.0%
Proof of concept only
1
10.0%
Forecast only
0
0.0%
No public exploit
8
80.0%
split by
peak 2 / quarter
Q3 191
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q4 190
Q1 200
Q2 200
Q3 201
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q4 201
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q1 210
Q2 212
Protected by Waratek2
High2
blocked by ARMR today2
No public exploit2
Q3 210
Q4 211
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q1 221
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q2 222
Protected by Waratek2
High2
blocked by ARMR today2
Exploited1
No public exploit1
Q3 221
Protected by Waratek1
High1
blocked by ARMR today1
Proof of concept only1
Q3 19Q1 20Q3 20Q1 21Q3 21Q1 22Q3 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-34169 | High | 2022-07-19 | Protected by Waratek | Proof of concept only | The Apache Xalan Java XSLT library is vulnerable to an integer truncation issue when processing malicious XSLT stylesheets. This can be used to corrupt Java class files generated by the internal XSLTC compiler and execute arbitrary Java bytecode. Users are recommended to update to version 2.7.3 or later. Note: Java runtimes (such as OpenJDK) include repackaged copies of Xalan. |
| CVE-2022-21500 | High | 2022-05-20 | Protected by Waratek | Exploited | Vulnerability in Oracle E-Business Suite (component: Manage Proxies). The supported version that is affected is 12.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle E-Business Suite. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle E-Business Suite accessible data. Note: Authentication is required for successful attack, however the user may be self-registered. <br> <br>Oracle E-Business Suite 12.1 is not impacted by this vulnerability. Customers should refer to the Patch Availability Document for details. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2022-25647 | High | 2022-05-01 | Protected by Waratek | No public exploit | The package com.google.code.gson:gson before 2.8.9 are vulnerable to Deserialization of Untrusted Data via the writeReplace() method in internal classes, which may lead to DoS attacks. |
| CVE-2022-23181 | High | 2022-01-27 | Protected by Waratek | No public exploit | The fix for bug CVE-2020-9484 introduced a time of check, time of use vulnerability into Apache Tomcat 10.1.0-M1 to 10.1.0-M8, 10.0.0-M5 to 10.0.14, 9.0.35 to 9.0.56 and 8.5.55 to 8.5.73 that allowed a local attacker to perform actions with the privileges of the user that the Tomcat process is using. This issue is only exploitable when Tomcat is configured to persist sessions using the FileStore. |
| CVE-2021-42340 | High | 2021-10-14 | Protected by Waratek | No public exploit | The fix for bug 63362 present in Apache Tomcat 10.1.0-M1 to 10.1.0-M5, 10.0.0-M1 to 10.0.11, 9.0.40 to 9.0.53 and 8.5.60 to 8.5.71 introduced a memory leak. The object introduced to collect metrics for HTTP upgrade connections was not released for WebSocket connections once the connection was closed. This created a memory leak that, over time, could lead to a denial of service via an OutOfMemoryError. |
| CVE-2021-33813 | High | 2021-06-16 | Protected by Waratek | No public exploit | An XXE issue in SAXBuilder in JDOM through 2.0.6 allows attackers to cause a denial of service via a crafted HTTP request. |
| CVE-2021-22118 | High | 2021-05-27 | Protected by Waratek | No public exploit | In Spring Framework, versions 5.2.x prior to 5.2.15 and versions 5.3.x prior to 5.3.7, a WebFlux application is vulnerable to a privilege escalation: by (re)creating the temporary storage directory, a locally authenticated malicious user can read or modify files that have been uploaded to the WebFlux application, or overwrite arbitrary files with multipart request data. |
| CVE-2020-25649 | High | 2020-12-03 | Protected by Waratek | No public exploit | A flaw was found in FasterXML Jackson Databind, where it did not have entity expansion secured properly. This flaw allows vulnerability to XML external entity (XXE) attacks. The highest threat from this vulnerability is data integrity. |
| CVE-2020-7712 | High | 2020-08-30 | Protected by Waratek | No public exploit | This affects the package json before 10.0.0. It is possible to inject arbritary commands using the parseLookup function. |
| CVE-2019-10086 | High | 2019-08-20 | Protected by Waratek | No public exploit | In Apache Commons Beanutils 1.9.2, a special BeanIntrospector class was added which allows suppressing the ability for an attacker to access the classloader via the class property available on all Java objects. We, however were not using this by default characteristic of the PropertyUtilsBean. |