
Oracle Critical Patch Update April 2022
Released April 2022 · Oracle's advisory ↗ · ← Critical Patch Update, January 2022 · Critical Patch Update, July 2022 →
222 CVEs in this release, one square each
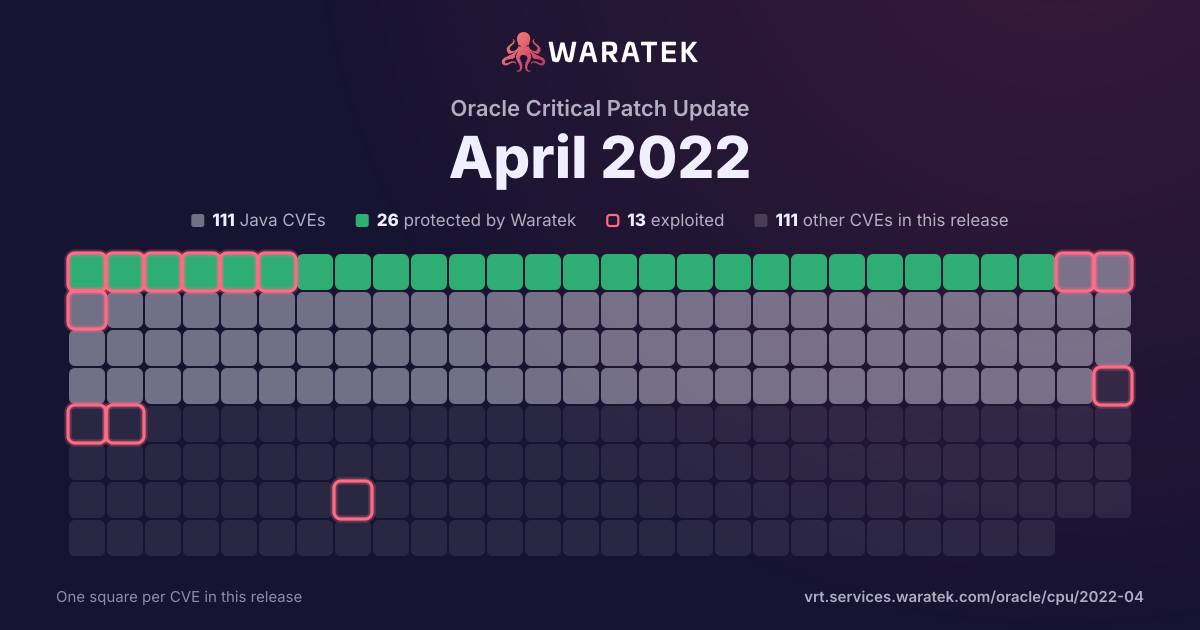
By status
26Protected by Waratek5Mitigation candidate80No exploit published64Outside Waratek scope47Not applicable
13Exploited, marked by the ring
No exploit published. For 40 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 111 matches · 26 protected · 9 exploited · 5 CISA KEV · 13 public PoC · 15 EPSS ≥ 0.5
Protected by Waratek
26
23.4%
Rule in development
0
0.0%
Mitigation candidate
5
4.5%
No exploit published
80
72.1%
blocked by ARMR today
26
23.4%
partly blocked
0
0.0%
not blocked
85
76.6%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 40 / quarter
Q1 181
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q2 180
Q3 180
Q4 180
Q1 190
Q2 192
Protected by Waratek2
High1
Medium1
blocked by ARMR today2
Working exploit published1
No public exploit1
Q3 191
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q4 190
Q1 203
No exploit published3
High3
not blocked3
Proof of concept only1
No public exploit2
Q2 201
No exploit published1
High1
not blocked1
No public exploit1
Q3 202
Protected by Waratek1
No exploit published1
High1
Medium1
blocked by ARMR today1
not blocked1
No public exploit2
Q4 2011
Protected by Waratek5
No exploit published6
Critical1
High6
Medium3
Low1
blocked by ARMR today5
not blocked6
Exploited1
No public exploit10
Q1 217
No exploit published7
High1
Medium6
not blocked7
No public exploit7
Q2 219
Protected by Waratek4
Mitigation candidate1
No exploit published4
High3
Medium6
blocked by ARMR today4
not blocked5
Exploited1
Working exploit published1
No public exploit7
Q3 2114
Protected by Waratek1
Mitigation candidate1
No exploit published12
High7
Medium7
blocked by ARMR today1
not blocked13
Exploited2
Forecast only1
No public exploit11
Q4 216
Protected by Waratek2
Mitigation candidate1
No exploit published3
High2
Medium4
blocked by ARMR today2
not blocked4
Exploited1
Proof of concept only1
No public exploit4
Q1 2213
Protected by Waratek4
Mitigation candidate1
No exploit published8
Critical4
High4
Medium5
blocked by ARMR today4
not blocked9
Exploited1
Working exploit published1
Proof of concept only4
Forecast only1
No public exploit6
Q2 2240
Protected by Waratek5
Mitigation candidate1
No exploit published34
Critical4
High11
Medium24
Low1
blocked by ARMR today5
not blocked35
Exploited2
Proof of concept only1
No public exploit37
Q3 221
No exploit published1
High1
not blocked1
No public exploit1
Q1 18Q3 18Q1 19Q3 19Q1 20Q3 20Q1 21Q3 21Q1 22Q3 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2020-11979 | High | 2020-10-01 | No exploit published | No public exploit | As mitigation for CVE-2020-1945 Apache Ant 1.10.8 changed the permissions of temporary files it created so that only the current user was allowed to access them. Unfortunately the fixcrlf task deleted the temporary file and created a new one without said protection, effectively nullifying the effort. This would still allow an attacker to inject modified source files into the build process. |
| CVE-2020-5421 | Medium | 2020-09-19 | No exploit published | No public exploit | In Spring Framework versions 5.2.0 - 5.2.8, 5.1.0 - 5.1.17, 5.0.0 - 5.0.18, 4.3.0 - 4.3.28, and older unsupported versions, the protections against RFD attacks from CVE-2015-5211 may be bypassed depending on the browser used through the use of a jsessionid path parameter. |
| CVE-2020-24750 | High | 2020-09-17 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.10.6 mishandles the interaction between serialization gadgets and typing, related to com.pastdev.httpcomponents.configuration.JndiConfiguration. |
| CVE-2020-11971 | High | 2020-05-14 | No exploit published | No public exploit | Apache Camel's JMX is vulnerable to Rebind Flaw. Apache Camel 2.22.x, 2.23.x, 2.24.x, 2.25.x, 3.0.0 up to 3.1.0 is affected. Users should upgrade to 3.2.0. |
| CVE-2020-5245 | High | 2020-02-24 | No exploit published | Proof of concept only | Dropwizard-Validation before 1.3.19, and 2.0.2 may allow arbitrary code execution on the host system, with the privileges of the Dropwizard service account, by injecting arbitrary Java Expression Language expressions when using the self-validating feature. The issue has been fixed in dropwizard-validation 1.3.19 and 2.0.2. |
| CVE-2020-7226 | High | 2020-01-24 | No exploit published | No public exploit | CiphertextHeader.java in Cryptacular 1.2.3, as used in Apereo CAS and other products, allows attackers to trigger excessive memory allocation during a decode operation, because the nonce array length associated with "new byte" may depend on untrusted input within the header of encoded data. |
| CVE-2019-12399 | High | 2020-01-14 | No exploit published | No public exploit | When Connect workers in Apache Kafka 2.0.0, 2.0.1, 2.1.0, 2.1.1, 2.2.0, 2.2.1, or 2.3.0 are configured with one or more config providers, and a connector is created/updated on that Connect cluster to use an externalized secret variable in a substring of a connector configuration property value, then any client can issue a request to the same Connect cluster to obtain the connector's task configuration and the response will contain the plaintext secret rather than the externalized secrets variables. |
| CVE-2019-10086 | High | 2019-08-20 | Protected by Waratek | No public exploit | In Apache Commons Beanutils 1.9.2, a special BeanIntrospector class was added which allows suppressing the ability for an attacker to access the classloader via the class property available on all Java objects. We, however were not using this by default characteristic of the PropertyUtilsBean. |
| CVE-2019-12086 | High | 2019-05-17 | Protected by Waratek | No public exploit | A Polymorphic Typing issue was discovered in FasterXML jackson-databind 2.x before 2.9.9. When Default Typing is enabled (either globally or for a specific property) for an externally exposed JSON endpoint, the service has the mysql-connector-java jar (8.0.14 or earlier) in the classpath, and an attacker can host a crafted MySQL server reachable by the victim, an attacker can send a crafted JSON message that allows them to read arbitrary local files on the server. This occurs because of missing com.mysql.cj.jdbc.admin.MiniAdmin validation. |
| CVE-2019-3799 | Medium | 2019-05-06 | Protected by Waratek | Working exploit published | Spring Cloud Config, versions 2.1.x prior to 2.1.2, versions 2.0.x prior to 2.0.4, and versions 1.4.x prior to 1.4.6, and older unsupported versions allow applications to serve arbitrary configuration files through the spring-cloud-config-server module. A malicious user, or attacker, can send a request using a specially crafted URL that can lead a directory traversal attack. |
| CVE-2017-1000353 | Critical | 2018-01-29 | Protected by Waratek | Exploited | Jenkins versions 2.56 and earlier as well as 2.46.1 LTS and earlier are vulnerable to an unauthenticated remote code execution. An unauthenticated remote code execution vulnerability allowed attackers to transfer a serialized Java `SignedObject` object to the Jenkins CLI, that would be deserialized using a new `ObjectInputStream`, bypassing the existing blacklist-based protection mechanism. We're fixing this issue by adding `SignedObject` to the blacklist. We're also backporting the new HTTP CLI protocol from Jenkins 2.54 to LTS 2.46.2, and deprecating the remoting-based (i.e. Java serialization) CLI protocol, disabling it by default. |