
Oracle Critical Patch Update April 2022
Released April 2022 · Oracle's advisory ↗ · ← Critical Patch Update, January 2022 · Critical Patch Update, July 2022 →
222 CVEs in this release, one square each
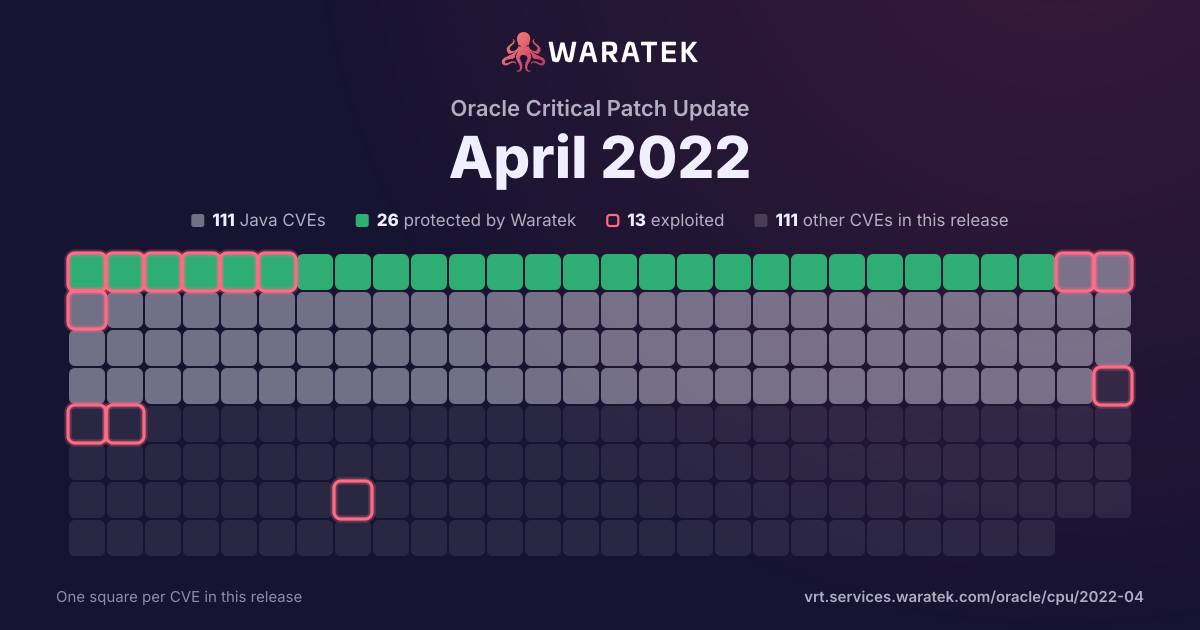
By status
26Protected by Waratek5Mitigation candidate80No exploit published64Outside Waratek scope47Not applicable
13Exploited, marked by the ring
No exploit published. For 40 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 13 matches · 9 in Waratek scope · 6 protected · 8 CISA KEV · 11 public PoC · 12 EPSS ≥ 0.5
Protected by Waratek
6
46.2%
Rule in development
0
0.0%
Mitigation candidate
3
23.1%
No exploit published
0
0.0%
Outside Waratek scope
3
23.1%
Not applicable
1
7.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
6
46.2%
partly blocked
0
0.0%
not blocked
7
53.8%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
13
100.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 3 / quarter
Q1 181
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q2 180
Q3 180
Q4 180
Q1 190
Q2 190
Q3 190
Q4 190
Q1 200
Q2 201
Outside Waratek scope1
Medium1
not blocked1
Exploited1
Q3 200
Q4 201
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q1 211
Outside Waratek scope1
High1
not blocked1
Exploited1
Q2 211
Mitigation candidate1
Medium1
not blocked1
Exploited1
Q3 213
Protected by Waratek1
Mitigation candidate1
Outside Waratek scope1
Critical1
Medium2
blocked by ARMR today1
not blocked2
Exploited3
Q4 212
Protected by Waratek1
Not applicable1
Critical1
Medium1
blocked by ARMR today1
not blocked1
Exploited2
Q1 221
Mitigation candidate1
Critical1
not blocked1
Exploited1
Q2 222
Protected by Waratek2
Critical2
blocked by ARMR today2
Exploited2
Q2 18Q4 18Q2 19Q4 19Q2 20Q4 20Q2 21Q4 21Q2 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-21445 | Critical | 2022-04-19 | Protected by Waratek | Exploited | Vulnerability in the Oracle Application Development Framework (ADF) product of Oracle Fusion Middleware (component: ADF Faces). Supported versions that are affected are 12.2.1.3.0 and 12.2.1.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Application Development Framework (ADF). Successful attacks of this vulnerability can result in takeover of Oracle Application Development Framework (ADF). Note: Oracle Application Development Framework (ADF) is downloaded via Oracle JDeveloper Product. Please refer to Fusion Middleware Patch Advisor for more details. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2022-22965 | Critical | 2022-04-01 | Protected by Waratek | Exploited | A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit requires the application to run on Tomcat as a WAR deployment. If the application is deployed as a Spring Boot executable jar, i.e. the default, it is not vulnerable to the exploit. However, the nature of the vulnerability is more general, and there may be other ways to exploit it. |
| CVE-2022-22947 | Critical | 2022-03-03 | Mitigation candidate | Exploited | In spring cloud gateway versions prior to 3.1.1+ and 3.0.7+ , applications are vulnerable to a code injection attack when the Gateway Actuator endpoint is enabled, exposed and unsecured. A remote attacker could make a maliciously crafted request that could allow arbitrary remote execution on the remote host. |
| CVE-2021-44832 | Medium | 2021-12-28 | Protected by Waratek | Exploited | Apache Log4j2 versions 2.0-beta7 through 2.17.0 (excluding security fix releases 2.3.2 and 2.12.4) are vulnerable to a remote code execution (RCE) attack when a configuration uses a JDBC Appender with a JNDI LDAP data source URI when an attacker has control of the target LDAP server. This issue is fixed by limiting JNDI data source names to the java protocol in Log4j2 versions 2.17.1, 2.12.4, and 2.3.2. |
| CVE-2021-42013 | Critical | 2021-10-07 | Not applicable | Exploited | It was found that the fix for CVE-2021-41773 in Apache HTTP Server 2.4.50 was insufficient. An attacker could use a path traversal attack to map URLs to files outside the directories configured by Alias-like directives. If files outside of these directories are not protected by the usual default configuration "require all denied", these requests can succeed. If CGI scripts are also enabled for these aliased pathes, this could allow for remote code execution. This issue only affects Apache 2.4.49 and Apache 2.4.50 and not earlier versions. |
| CVE-2021-38153 | Medium | 2021-09-22 | Mitigation candidate | Exploited | Some components in Apache Kafka use `Arrays.equals` to validate a password or key, which is vulnerable to timing attacks that make brute force attacks for such credentials more likely to be successful. Users should upgrade to 2.8.1 or higher, or 3.0.0 or higher where this vulnerability has been fixed. The affected versions include Apache Kafka 2.0.0, 2.0.1, 2.1.0, 2.1.1, 2.2.0, 2.2.1, 2.2.2, 2.3.0, 2.3.1, 2.4.0, 2.4.1, 2.5.0, 2.5.1, 2.6.0, 2.6.1, 2.6.2, 2.7.0, 2.7.1, and 2.8.0. |
| CVE-2021-40438 | Critical | 2021-09-16 | Outside Waratek scope | Exploited | A crafted request uri-path can cause mod_proxy to forward the request to an origin server choosen by the remote user. This issue affects Apache HTTP Server 2.4.48 and earlier. |
| CVE-2021-34429 | Medium | 2021-07-15 | Protected by Waratek | Exploited | For Eclipse Jetty versions 9.4.37-9.4.42, 10.0.1-10.0.5 & 11.0.1-11.0.5, URIs can be crafted using some encoded characters to access the content of the WEB-INF directory and/or bypass some security constraints. This is a variation of the vulnerability reported in CVE-2021-28164/GHSA-v7ff-8wcx-gmc5. |
| CVE-2021-28169 | Medium | 2021-06-09 | Mitigation candidate | Exploited | For Eclipse Jetty versions <= 9.4.40, <= 10.0.2, <= 11.0.2, it is possible for requests to the ConcatServlet with a doubly encoded path to access protected resources within the WEB-INF directory. For example a request to `/concat?/%2557EB-INF/web.xml` can retrieve the web.xml file. This can reveal sensitive information regarding the implementation of a web application. |
| CVE-2021-3156 | High | 2021-01-26 | Outside Waratek scope | Exploited | Sudo before 1.9.5p2 contains an off-by-one error that can result in a heap-based buffer overflow, which allows privilege escalation to root via "sudoedit -s" and a command-line argument that ends with a single backslash character. |
| CVE-2020-17530 | Critical | 2020-12-11 | Protected by Waratek | Exploited | Forced OGNL evaluation, when evaluated on raw user input in tag attributes, may lead to remote code execution. Affected software : Apache Struts 2.0.0 - Struts 2.5.25. |
| CVE-2020-11022 | Medium | 2020-04-29 | Outside Waratek scope | Exploited | In jQuery starting with 1.12.0 and before 3.5.0, passing HTML from untrusted sources - even after sanitizing it - to one of jQuery's DOM manipulation methods (i.e. .html(), .append(), and others) may execute untrusted code. This problem is patched in jQuery 3.5.0. |
| CVE-2017-1000353 | Critical | 2018-01-29 | Protected by Waratek | Exploited | Jenkins versions 2.56 and earlier as well as 2.46.1 LTS and earlier are vulnerable to an unauthenticated remote code execution. An unauthenticated remote code execution vulnerability allowed attackers to transfer a serialized Java `SignedObject` object to the Jenkins CLI, that would be deserialized using a new `ObjectInputStream`, bypassing the existing blacklist-based protection mechanism. We're fixing this issue by adding `SignedObject` to the blacklist. We're also backporting the new HTTP CLI protocol from Jenkins 2.54 to LTS 2.46.2, and deprecating the remoting-based (i.e. Java serialization) CLI protocol, disabling it by default. |