
Oracle Critical Patch Update January 2022
Released January 2022 · Oracle's advisory ↗ · ← Critical Patch Update, October 2021 · Critical Patch Update, April 2022 →
266 CVEs in this release, one square each
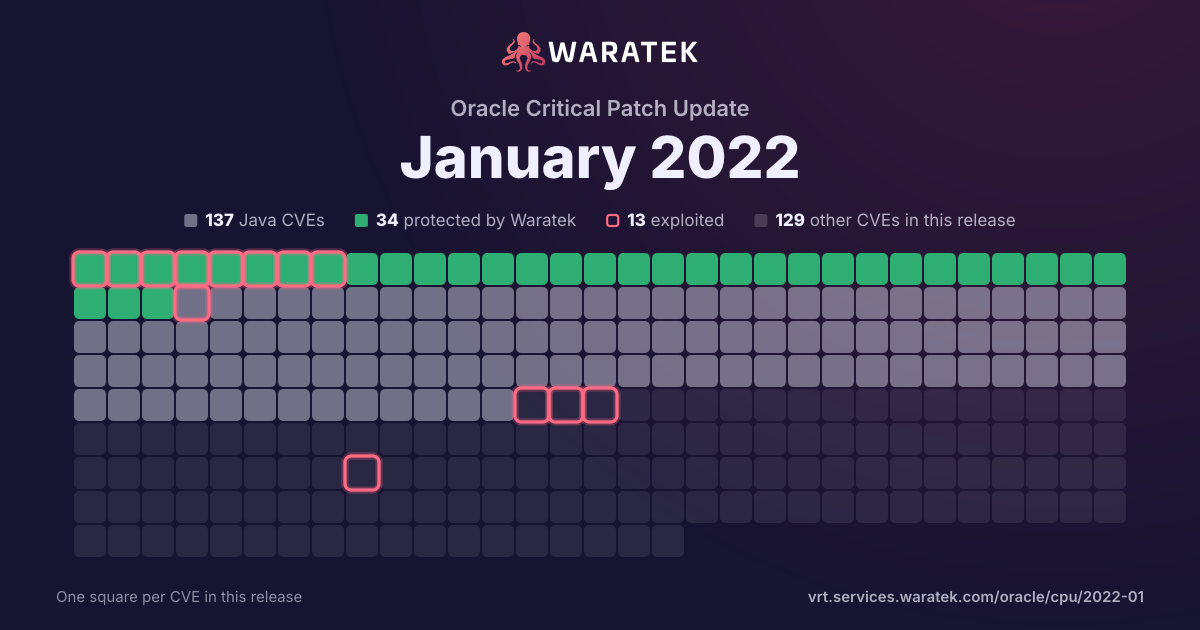
By status
34Protected by Waratek3Mitigation candidate100No exploit published57Outside Waratek scope72Not applicable
13Exploited, marked by the ring
No exploit published. For 71 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 25 matches · 7 protected · 4 exploited · 0 CISA KEV · 3 public PoC · 4 EPSS ≥ 0.5
Protected by Waratek
7
28.0%
Rule in development
0
0.0%
Mitigation candidate
1
4.0%
No exploit published
17
68.0%
blocked by ARMR today
7
28.0%
partly blocked
0
0.0%
not blocked
18
72.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
4
16.0%
Working exploit published
1
4.0%
Proof of concept only
0
0.0%
Forecast only
1
4.0%
No public exploit
19
76.0%
split by
peak 11 / month
Sep 201
No exploit published1
Medium1
not blocked1
No public exploit1
Oct 200
Nov 200
Dec 201
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
Jan 210
Feb 212
Protected by Waratek1
No exploit published1
Medium2
blocked by ARMR today1
not blocked1
No public exploit2
Mar 211
No exploit published1
Medium1
not blocked1
No public exploit1
Apr 211
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
May 210
Jun 212
Protected by Waratek1
No exploit published1
Medium2
blocked by ARMR today1
not blocked1
Working exploit published1
No public exploit1
Jul 213
Protected by Waratek1
No exploit published2
Medium3
blocked by ARMR today1
not blocked2
Exploited1
Forecast only1
No public exploit1
Aug 210
Sep 211
Mitigation candidate1
Medium1
not blocked1
Exploited1
Oct 210
Nov 210
Dec 212
Protected by Waratek2
Medium2
blocked by ARMR today2
Exploited2
Jan 2211
No exploit published11
Medium11
not blocked11
No public exploit11
Sep 20Nov 20Jan 21Mar 21May 21Jul 21Sep 21Nov 21Jan 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-21403 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Operations Monitor product of Oracle Communications (component: Mediation Engine). Supported versions that are affected are 3.4, 4.2, 4.3, 4.4 and 5.0. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Communications Operations Monitor. While the vulnerability is in Oracle Communications Operations Monitor, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Operations Monitor accessible data as well as unauthorized read access to a subset of Oracle Communications Operations Monitor accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Communications Operations Monitor. CVSS 3.1 Base Score 6.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:L/I:L/A:L). |
| CVE-2022-21402 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Operations Monitor product of Oracle Communications (component: Mediation Engine). Supported versions that are affected are 3.4, 4.2, 4.3, 4.4 and 5.0. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Communications Operations Monitor. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Communications Operations Monitor, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Operations Monitor accessible data as well as unauthorized read access to a subset of Oracle Communications Operations Monitor accessible data. CVSS 3.1 Base Score 4.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2022-21401 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Operations Monitor product of Oracle Communications (component: Mediation Engine). Supported versions that are affected are 3.4, 4.2, 4.3, 4.4 and 5.0. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Communications Operations Monitor. While the vulnerability is in Oracle Communications Operations Monitor, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Operations Monitor accessible data as well as unauthorized read access to a subset of Oracle Communications Operations Monitor accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Communications Operations Monitor. CVSS 3.1 Base Score 6.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:L/I:L/A:L). |
| CVE-2022-21400 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Operations Monitor product of Oracle Communications (component: Mediation Engine). Supported versions that are affected are 3.4, 4.2, 4.3, 4.4 and 5.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Communications Operations Monitor. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Communications Operations Monitor, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Operations Monitor accessible data as well as unauthorized read access to a subset of Oracle Communications Operations Monitor accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2022-21399 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Operations Monitor product of Oracle Communications (component: Mediation Engine). Supported versions that are affected are 3.4, 4.2, 4.3, 4.4 and 5.0. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Communications Operations Monitor. While the vulnerability is in Oracle Communications Operations Monitor, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Operations Monitor accessible data as well as unauthorized read access to a subset of Oracle Communications Operations Monitor accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Communications Operations Monitor. CVSS 3.1 Base Score 6.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:L/I:L/A:L). |
| CVE-2022-21398 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Operations Monitor product of Oracle Communications (component: Mediation Engine). Supported versions that are affected are 3.4, 4.2, 4.3, 4.4 and 5.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Communications Operations Monitor. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Communications Operations Monitor, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Operations Monitor accessible data as well as unauthorized read access to a subset of Oracle Communications Operations Monitor accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2022-21397 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Operations Monitor product of Oracle Communications (component: Mediation Engine). Supported versions that are affected are 3.4, 4.2, 4.3, 4.4 and 5.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Communications Operations Monitor. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Communications Operations Monitor, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Operations Monitor accessible data as well as unauthorized read access to a subset of Oracle Communications Operations Monitor accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2022-21396 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Operations Monitor product of Oracle Communications (component: Mediation Engine). Supported versions that are affected are 3.4, 4.2, 4.3, 4.4 and 5.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Communications Operations Monitor. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Communications Operations Monitor, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Operations Monitor accessible data as well as unauthorized read access to a subset of Oracle Communications Operations Monitor accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2022-21383 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Enterprise Session Border Controller product of Oracle Communications (component: Log). Supported versions that are affected are 8.4 and 9.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Enterprise Session Border Controller. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Enterprise Session Border Controller. CVSS 3.1 Base Score 4.3 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2022-21381 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Enterprise Session Border Controller product of Oracle Communications (component: WebUI). Supported versions that are affected are 8.4 and 9.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Enterprise Session Border Controller. While the vulnerability is in Oracle Enterprise Session Border Controller, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Enterprise Session Border Controller accessible data as well as unauthorized read access to a subset of Oracle Enterprise Session Border Controller accessible data. CVSS 3.1 Base Score 6.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:N). |
| CVE-2022-21246 | Medium | 2022-01-19 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Operations Monitor product of Oracle Communications (component: Mediation Engine). Supported versions that are affected are 3.4, 4.2, 4.3, 4.4 and 5.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Communications Operations Monitor. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Communications Operations Monitor, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Operations Monitor accessible data as well as unauthorized read access to a subset of Oracle Communications Operations Monitor accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2021-44832 | Medium | 2021-12-28 | Protected by Waratek | Exploited | Apache Log4j2 versions 2.0-beta7 through 2.17.0 (excluding security fix releases 2.3.2 and 2.12.4) are vulnerable to a remote code execution (RCE) attack when a configuration uses a JDBC Appender with a JNDI LDAP data source URI when an attacker has control of the target LDAP server. This issue is fixed by limiting JNDI data source names to the java protocol in Log4j2 versions 2.17.1, 2.12.4, and 2.3.2. |
| CVE-2021-45105 | Medium | 2021-12-18 | Protected by Waratek | Exploited | Apache Log4j2 versions 2.0-alpha1 through 2.16.0 (excluding 2.12.3 and 2.3.1) did not protect from uncontrolled recursion from self-referential lookups. This allows an attacker with control over Thread Context Map data to cause a denial of service when a crafted string is interpreted. This issue was fixed in Log4j 2.17.0, 2.12.3, and 2.3.1. |
| CVE-2021-38153 | Medium | 2021-09-22 | Mitigation candidate | Exploited | Some components in Apache Kafka use `Arrays.equals` to validate a password or key, which is vulnerable to timing attacks that make brute force attacks for such credentials more likely to be successful. Users should upgrade to 2.8.1 or higher, or 3.0.0 or higher where this vulnerability has been fixed. The affected versions include Apache Kafka 2.0.0, 2.0.1, 2.1.0, 2.1.1, 2.2.0, 2.2.1, 2.2.2, 2.3.0, 2.3.1, 2.4.0, 2.4.1, 2.5.0, 2.5.1, 2.6.0, 2.6.1, 2.6.2, 2.7.0, 2.7.1, and 2.8.0. |
| CVE-2021-34429 | Medium | 2021-07-15 | Protected by Waratek | Exploited | For Eclipse Jetty versions 9.4.37-9.4.42, 10.0.1-10.0.5 & 11.0.1-11.0.5, URIs can be crafted using some encoded characters to access the content of the WEB-INF directory and/or bypass some security constraints. This is a variation of the vulnerability reported in CVE-2021-28164/GHSA-v7ff-8wcx-gmc5. |
| CVE-2021-36374 | Medium | 2021-07-14 | No exploit published | No public exploit | When reading a specially crafted ZIP archive, or a derived formats, an Apache Ant build can be made to allocate large amounts of memory that leads to an out of memory error, even for small inputs. This can be used to disrupt builds using Apache Ant. Commonly used derived formats from ZIP archives are for instance JAR files and many office files. Apache Ant prior to 1.9.16 and 1.10.11 were affected. |
| CVE-2021-33037 | Medium | 2021-07-12 | No exploit published | Forecast only | Apache Tomcat 10.0.0-M1 to 10.0.6, 9.0.0.M1 to 9.0.46 and 8.5.0 to 8.5.66 did not correctly parse the HTTP transfer-encoding request header in some circumstances leading to the possibility to request smuggling when used with a reverse proxy. Specifically: - Tomcat incorrectly ignored the transfer encoding header if the client declared it would only accept an HTTP/1.0 response; - Tomcat honoured the identify encoding; and - Tomcat did not ensure that, if present, the chunked encoding was the final encoding. |
| CVE-2020-6950 | Medium | 2021-06-02 | Protected by Waratek | Working exploit published | Directory traversal in Eclipse Mojarra before 2.3.14 allows attackers to read arbitrary files via the loc parameter or con parameter. |
| CVE-2020-14340 | Medium | 2021-06-02 | No exploit published | No public exploit | A vulnerability was discovered in XNIO where file descriptor leak caused by growing amounts of NIO Selector file handles between garbage collection cycles. It may allow the attacker to cause a denial of service. It affects XNIO versions 3.6.0.Beta1 through 3.8.1.Final. |
| CVE-2021-29425 | Medium | 2021-04-13 | Protected by Waratek | No public exploit | In Apache Commons IO before 2.7, When invoking the method FileNameUtils.normalize with an improper input string, like "//../foo", or "\\..\foo", the result would be the same value, thus possibly providing access to files in the parent directory, but not further above (thus "limited" path traversal), if the calling code would use the result to construct a path value. |
| CVE-2021-21409 | Medium | 2021-03-30 | No exploit published | No public exploit | Netty is an open-source, asynchronous event-driven network application framework for rapid development of maintainable high performance protocol servers & clients. In Netty (io.netty:netty-codec-http2) before version 4.1.61.Final there is a vulnerability that enables request smuggling. The content-length header is not correctly validated if the request only uses a single Http2HeaderFrame with the endStream set to to true. This could lead to request smuggling if the request is proxied to a remote peer and translated to HTTP/1.1. This is a followup of GHSA-wm47-8v5p-wjpj/CVE-2021-21295 which did miss to fix this one case. This was fixed as part of 4.1.61.Final. |
| CVE-2021-27568 | Medium | 2021-02-23 | Protected by Waratek | No public exploit | An issue was discovered in netplex json-smart-v1 through 2015-10-23 and json-smart-v2 through 2.4. An exception is thrown from a function, but it is not caught, as demonstrated by NumberFormatException. When it is not caught, it may cause programs using the library to crash or expose sensitive information. |
| CVE-2020-29582 | Medium | 2021-02-03 | No exploit published | No public exploit | In JetBrains Kotlin before 1.4.21, a vulnerable Java API was used for temporary file and folder creation. An attacker was able to read data from such files and list directories due to insecure permissions. |
| CVE-2020-17521 | Medium | 2020-12-07 | Protected by Waratek | No public exploit | Apache Groovy provides extension methods to aid with creating temporary directories. Prior to this fix, Groovy's implementation of those extension methods was using a now superseded Java JDK method call that is potentially not secure on some operating systems in some contexts. Users not using the extension methods mentioned in the advisory are not affected, but may wish to read the advisory for further details. Versions Affected: 2.0 to 2.4.20, 2.5.0 to 2.5.13, 3.0.0 to 3.0.6, and 4.0.0-alpha-1. Fixed in versions 2.4.21, 2.5.14, 3.0.7, 4.0.0-alpha-2. |
| CVE-2020-5421 | Medium | 2020-09-19 | No exploit published | No public exploit | In Spring Framework versions 5.2.0 - 5.2.8, 5.1.0 - 5.1.17, 5.0.0 - 5.0.18, 4.3.0 - 4.3.28, and older unsupported versions, the protections against RFD attacks from CVE-2015-5211 may be bypassed depending on the browser used through the use of a jsessionid path parameter. |