
Oracle Critical Patch Update January 2022
Released January 2022 · Oracle's advisory ↗ · ← Critical Patch Update, October 2021 · Critical Patch Update, April 2022 →
266 CVEs in this release, one square each
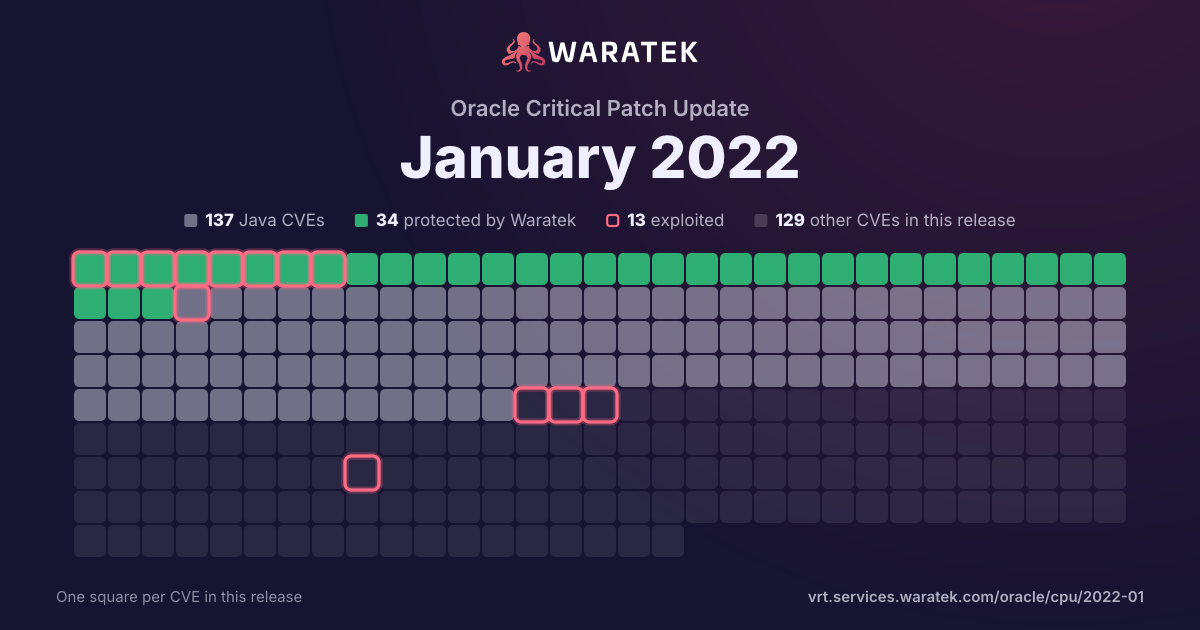
By status
34Protected by Waratek3Mitigation candidate100No exploit published57Outside Waratek scope72Not applicable
13Exploited, marked by the ring
No exploit published. For 71 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 1 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
6matches
1in Waratek scope16.7%
1protected16.7%
0exploited0.0%
0CISA KEV0.0%
1public PoC16.7%
0EPSS ≥ 0.50.0%
Protected by Waratek
1
16.7%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
3
50.0%
Not applicable
2
33.3%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
16.7%
partly blocked
0
0.0%
not blocked
5
83.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
6
100.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 2 / quarter
Q4 201
Not applicable1
High1
not blocked1
Proof of concept only1
Q1 211
Outside Waratek scope1
Critical1
not blocked1
Proof of concept only1
Q2 210
Q3 212
Outside Waratek scope2
High2
not blocked2
Proof of concept only2
Q4 210
Q1 221
Protected by Waratek1
Medium1
blocked by ARMR today1
Proof of concept only1
Q2 220
Q3 220
Q4 221
Not applicable1
Medium1
not blocked1
Proof of concept only1
Q4 20Q1 21Q2 21Q3 21Q4 21Q1 22Q2 22Q3 22Q4 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2021-43395 | Medium | 2022-12-26 | Not applicable | Proof of concept only | An issue was discovered in illumos before f859e7171bb5db34321e45585839c6c3200ebb90, OmniOS Community Edition r151038, OpenIndiana Hipster 2021.04, and SmartOS 20210923. A local unprivileged user can cause a deadlock and kernel panic via crafted rename and rmdir calls on tmpfs filesystems. Oracle Solaris 10 and 11 is also affected. |
| CVE-2022-21341 | Medium | 2022-01-19 | Protected by Waratek | Proof of concept only | Vulnerability in the Oracle Java SE, Oracle GraalVM Enterprise Edition product of Oracle Java SE (component: Serialization). Supported versions that are affected are Oracle Java SE: 7u321, 8u311, 11.0.13, 17.0.1; Oracle GraalVM Enterprise Edition: 20.3.4 and 21.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Oracle Java SE, Oracle GraalVM Enterprise Edition. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Java SE, Oracle GraalVM Enterprise Edition. Note: This vulnerability applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. This vulnerability can also be exploited by using APIs in the specified Component, e.g., through a web service which supplies data to the APIs. CVSS 3.1 Base Score 5.3 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2021-22946 | High | 2021-09-29 | Outside Waratek scope | Proof of concept only | A user can tell curl >= 7.20.0 and <= 7.78.0 to require a successful upgrade to TLS when speaking to an IMAP, POP3 or FTP server (`--ssl-reqd` on the command line or`CURLOPT_USE_SSL` set to `CURLUSESSL_CONTROL` or `CURLUSESSL_ALL` withlibcurl). This requirement could be bypassed if the server would return a properly crafted but perfectly legitimate response.This flaw would then make curl silently continue its operations **withoutTLS** contrary to the instructions and expectations, exposing possibly sensitive data in clear text over the network. |
| CVE-2021-33909 | High | 2021-07-20 | Outside Waratek scope | Proof of concept only | fs/seq_file.c in the Linux kernel 3.16 through 5.13.x before 5.13.4 does not properly restrict seq buffer allocations, leading to an integer overflow, an Out-of-bounds Write, and escalation to root by an unprivileged user, aka CID-8cae8cd89f05. |
| CVE-2021-3177 | Critical | 2021-01-19 | Outside Waratek scope | Proof of concept only | Python 3.x through 3.9.1 has a buffer overflow in PyCArg_repr in _ctypes/callproc.c, which may lead to remote code execution in certain Python applications that accept floating-point numbers as untrusted input, as demonstrated by a 1e300 argument to c_double.from_param. This occurs because sprintf is used unsafely. |
| CVE-2020-8285 | High | 2020-12-14 | Not applicable | Proof of concept only | curl 7.21.0 to and including 7.73.0 is vulnerable to uncontrolled recursion due to a stack overflow issue in FTP wildcard match parsing. |