
Oracle Critical Patch Update October 2021
Released October 2021 · Oracle's advisory ↗ · ← Critical Patch Update, July 2021 · Critical Patch Update, January 2022 →
231 CVEs in this release, one square each
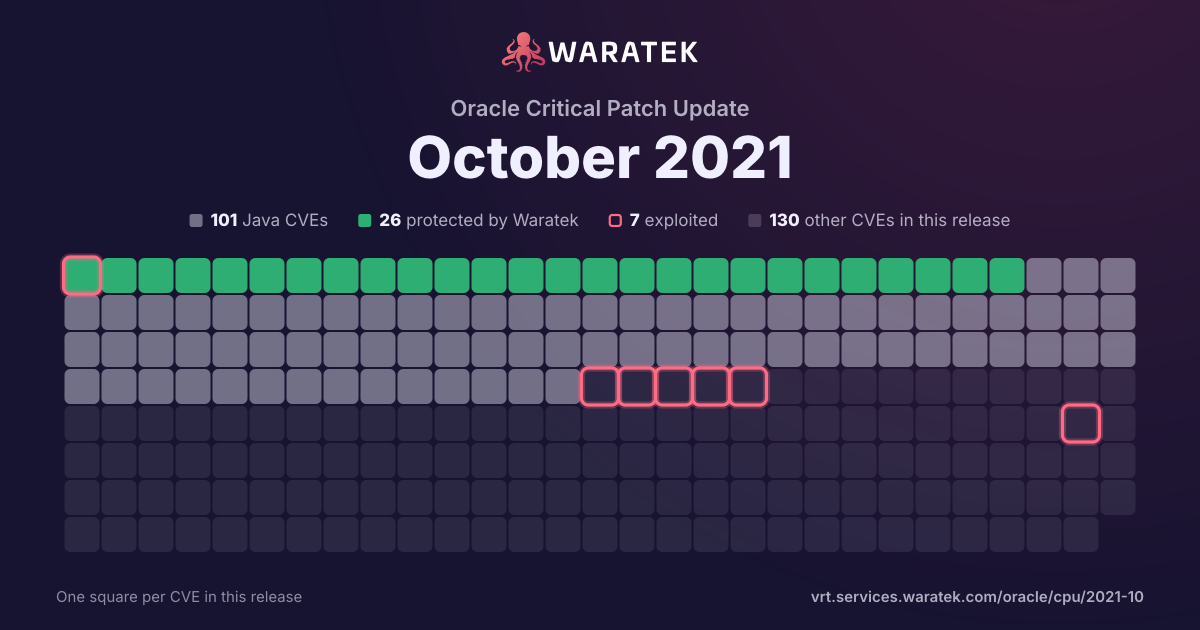
By status
26Protected by Waratek3Mitigation candidate72No exploit published42Outside Waratek scope88Not applicable
7Exploited, marked by the ring
No exploit published. For 52 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 205 matches · 75 in Waratek scope · 0 protected · 6 exploited · 3 CISA KEV · 15 public PoC · 21 EPSS ≥ 0.5
205matches
75in Waratek scope36.6%
0protected0.0%
6exploited2.9%
3CISA KEV1.5%
15public PoC7.3%
21EPSS ≥ 0.510.2%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
3
1.5%
No exploit published
72
35.1%
Outside Waratek scope
42
20.5%
Not applicable
88
42.9%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
205
100.0%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 130 / quarter
Q3 161
Outside Waratek scope1
High1
not blocked1
Proof of concept only1
Q4 160
Q1 170
Q2 171
Outside Waratek scope1
Critical1
not blocked1
Exploited1
Q3 170
Q4 170
Q1 180
Q2 180
Q3 180
Q4 180
Q1 192
Outside Waratek scope1
Not applicable1
High1
Medium1
not blocked2
No public exploit2
Q2 193
Outside Waratek scope2
Not applicable1
High2
Medium1
not blocked3
Exploited1
Working exploit published1
No public exploit1
Q3 192
Outside Waratek scope2
Critical1
Medium1
not blocked2
No public exploit2
Q4 191
Outside Waratek scope1
Critical1
not blocked1
Proof of concept only1
Q1 203
No exploit published1
Outside Waratek scope2
High3
not blocked3
Proof of concept only1
No public exploit2
Q2 207
Outside Waratek scope7
High3
Medium3
Low1
not blocked7
Exploited2
Proof of concept only1
No public exploit4
Q3 206
No exploit published3
Outside Waratek scope2
Not applicable1
Critical1
High3
Medium1
Low1
not blocked6
No public exploit6
Q4 208
No exploit published4
Outside Waratek scope4
High4
Medium3
Low1
not blocked8
Proof of concept only1
No public exploit7
Q1 2117
No exploit published7
Outside Waratek scope5
Not applicable5
Critical2
High8
Medium7
not blocked17
Exploited2
Proof of concept only1
No public exploit14
Q2 2112
Mitigation candidate1
No exploit published6
Outside Waratek scope2
Not applicable3
Critical1
High9
Medium2
not blocked12
Working exploit published2
Forecast only2
No public exploit8
Q3 2112
No exploit published6
Outside Waratek scope3
Not applicable3
Critical2
High6
Medium4
not blocked12
Proof of concept only1
Forecast only2
No public exploit9
Q4 21130
Mitigation candidate2
No exploit published45
Outside Waratek scope9
Not applicable74
Critical2
High34
Medium84
Low10
not blocked130
Proof of concept only3
Forecast only6
No public exploit121
Q4 16Q2 17Q4 17Q2 18Q4 18Q2 19Q4 19Q2 20Q4 20Q2 21Q4 21
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-11358 | Medium | 2019-04-20 | Outside Waratek scope | Exploited | jQuery before 3.4.0, as used in Drupal, Backdrop CMS, and other products, mishandles jQuery.extend(true, {}, ...) because of Object.prototype pollution. If an unsanitized source object contained an enumerable __proto__ property, it could extend the native Object.prototype. |
| CVE-2018-20034 | High | 2019-03-21 | Outside Waratek scope | No public exploit | A Denial of Service vulnerability related to adding an item to a list in lmgrd and vendor daemon components of FlexNet Publisher version 11.16.1.0 and earlier allows a remote attacker to send a combination of messages to lmgrd or the vendor daemon, causing the heartbeat between lmgrd and the vendor daemon to stop, and the vendor daemon to shut down. |
| CVE-2019-7317 | Medium | 2019-02-04 | Not applicable | No public exploit | png_image_free in png.c in libpng 1.6.x before 1.6.37 has a use-after-free because png_image_free_function is called under png_safe_execute. |
| CVE-2017-9841 | Critical | 2017-06-27 | Outside Waratek scope | Exploited | Util/PHP/eval-stdin.php in PHPUnit before 4.8.28 and 5.x before 5.6.3 allows remote attackers to execute arbitrary PHP code via HTTP POST data beginning with a "<?php " substring, as demonstrated by an attack on a site with an exposed /vendor folder, i.e., external access to the /vendor/phpunit/phpunit/src/Util/PHP/eval-stdin.php URI. |
| CVE-2016-2183 | High | 2016-09-01 | Outside Waratek scope | Proof of concept only | The DES and Triple DES ciphers, as used in the TLS, SSH, and IPSec protocols and other protocols and products, have a birthday bound of approximately four billion blocks, which makes it easier for remote attackers to obtain cleartext data via a birthday attack against a long-duration encrypted session, as demonstrated by an HTTPS session using Triple DES in CBC mode, aka a "Sweet32" attack. |