
Oracle Critical Patch Update October 2021
Released October 2021 · Oracle's advisory ↗ · ← Critical Patch Update, July 2021 · Critical Patch Update, January 2022 →
231 CVEs in this release, one square each
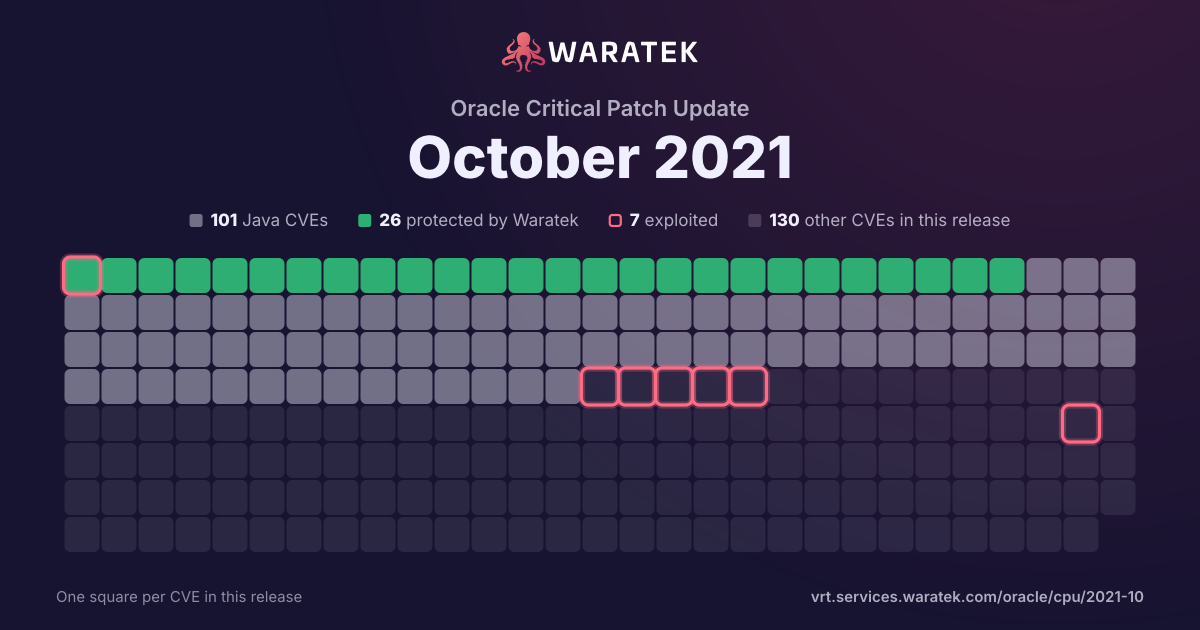
By status
26Protected by Waratek3Mitigation candidate72No exploit published42Outside Waratek scope88Not applicable
7Exploited, marked by the ring
No exploit published. For 52 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 1 in Waratek scope · 1 protected
Protected by Waratek
1
25.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
3
75.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
25.0%
partly blocked
0
0.0%
not blocked
3
75.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
4
100.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / quarter
Q2 171
Outside Waratek scope1
Critical1
not blocked1
Exploited1
Q3 170
Q4 170
Q1 180
Q2 180
Q3 180
Q4 180
Q1 190
Q2 190
Q3 190
Q4 190
Q1 200
Q2 201
Outside Waratek scope1
Medium1
not blocked1
Exploited1
Q3 200
Q4 201
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q1 211
Outside Waratek scope1
High1
not blocked1
Exploited1
Q3 17Q1 18Q3 18Q1 19Q3 19Q1 20Q3 20Q1 21
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2021-3156 | High | 2021-01-26 | Outside Waratek scope | Exploited | Sudo before 1.9.5p2 contains an off-by-one error that can result in a heap-based buffer overflow, which allows privilege escalation to root via "sudoedit -s" and a command-line argument that ends with a single backslash character. |
| CVE-2020-17530 | Critical | 2020-12-11 | Protected by Waratek | Exploited | Forced OGNL evaluation, when evaluated on raw user input in tag attributes, may lead to remote code execution. Affected software : Apache Struts 2.0.0 - Struts 2.5.25. |
| CVE-2020-11023 | Medium | 2020-04-29 | Outside Waratek scope | Exploited | In jQuery versions greater than or equal to 1.0.3 and before 3.5.0, passing HTML containing <option> elements from untrusted sources - even after sanitizing it - to one of jQuery's DOM manipulation methods (i.e. .html(), .append(), and others) may execute untrusted code. This problem is patched in jQuery 3.5.0. |
| CVE-2017-9841 | Critical | 2017-06-27 | Outside Waratek scope | Exploited | Util/PHP/eval-stdin.php in PHPUnit before 4.8.28 and 5.x before 5.6.3 allows remote attackers to execute arbitrary PHP code via HTTP POST data beginning with a "<?php " substring, as demonstrated by an attack on a site with an exposed /vendor folder, i.e., external access to the /vendor/phpunit/phpunit/src/Util/PHP/eval-stdin.php URI. |