
Oracle Critical Patch Update July 2021
Released July 2021 · Oracle's advisory ↗ · ← Critical Patch Update, April 2021 · Critical Patch Update, October 2021 →
231 CVEs in this release, one square each
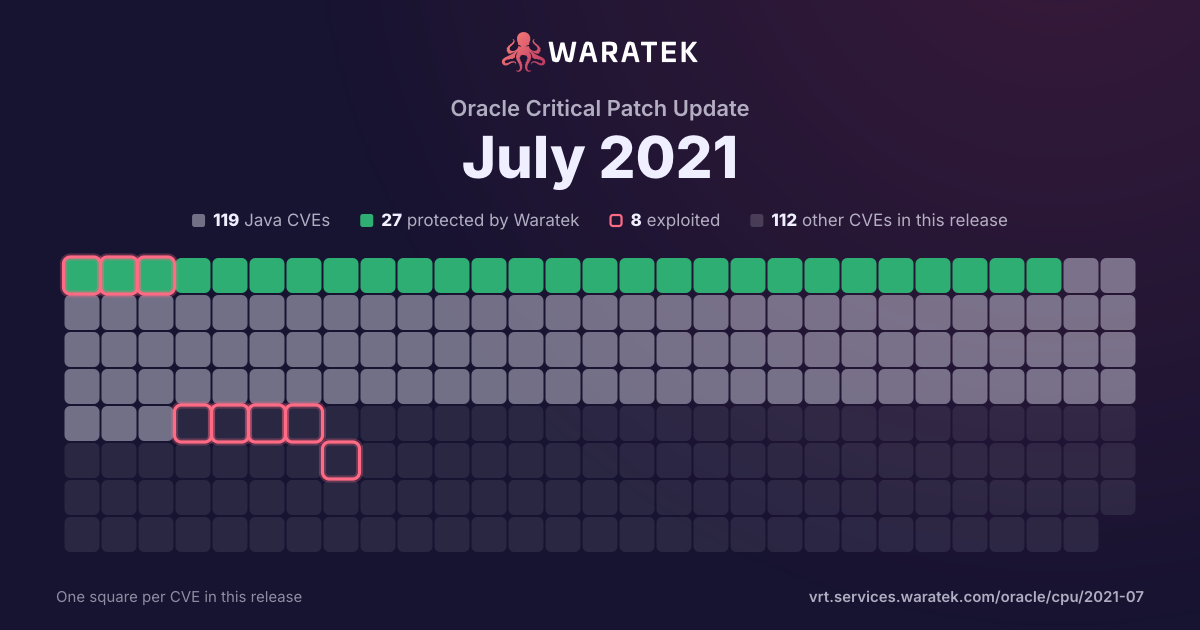
By status
27Protected by Waratek2Mitigation candidate90No exploit published33Outside Waratek scope79Not applicable
8Exploited, marked by the ring
No exploit published. For 70 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
6matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
6
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
6
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
6
100.0%
split by
peak 2 / quarter
Q2 171
Not applicable1
Critical1
not blocked1
No public exploit1
Q3 170
Q4 171
Not applicable1
Critical1
not blocked1
No public exploit1
Q1 180
Q2 180
Q3 180
Q4 180
Q1 190
Q2 190
Q3 191
Not applicable1
Critical1
not blocked1
No public exploit1
Q4 191
Not applicable1
Critical1
not blocked1
No public exploit1
Q1 200
Q2 200
Q3 200
Q4 200
Q1 210
Q2 210
Q3 212
Not applicable2
Critical2
not blocked2
No public exploit2
Q3 17Q1 18Q3 18Q1 19Q3 19Q1 20Q3 20Q1 21Q3 21
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2021-2447 | Critical | 2021-07-21 | Not applicable | No public exploit | Vulnerability in the Oracle Secure Global Desktop product of Oracle Virtualization (component: Server). The supported version that is affected is 5.6. Easily exploitable vulnerability allows low privileged attacker with network access via multiple protocols to compromise Oracle Secure Global Desktop. While the vulnerability is in Oracle Secure Global Desktop, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Oracle Secure Global Desktop. CVSS 3.1 Base Score 9.9 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2021-2446 | Critical | 2021-07-21 | Not applicable | No public exploit | Vulnerability in the Oracle Secure Global Desktop product of Oracle Virtualization (component: Client). The supported version that is affected is 5.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Oracle Secure Global Desktop. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Secure Global Desktop, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Oracle Secure Global Desktop. CVSS 3.1 Base Score 9.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2019-17545 | Critical | 2019-10-14 | Not applicable | No public exploit | GDAL through 3.0.1 has a poolDestroy double free in OGRExpatRealloc in ogr/ogr_expat.cpp when the 10MB threshold is exceeded. |
| CVE-2019-10746 | Critical | 2019-08-23 | Not applicable | No public exploit | mixin-deep is vulnerable to Prototype Pollution in versions before 1.3.2 and version 2.0.0. The function mixin-deep could be tricked into adding or modifying properties of Object.prototype using a constructor payload. |
| CVE-2017-16931 | Critical | 2017-11-23 | Not applicable | No public exploit | parser.c in libxml2 before 2.9.5 mishandles parameter-entity references because the NEXTL macro calls the xmlParserHandlePEReference function in the case of a '%' character in a DTD name. |
| CVE-2017-5461 | Critical | 2017-05-11 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.21.4, 3.22.x through 3.28.x before 3.28.4, 3.29.x before 3.29.5, and 3.30.x before 3.30.1 allows remote attackers to cause a denial of service (out-of-bounds write) or possibly have unspecified other impact by leveraging incorrect base64 operations. |