
Oracle Critical Patch Update July 2021
Released July 2021 · Oracle's advisory ↗ · ← Critical Patch Update, April 2021 · Critical Patch Update, October 2021 →
231 CVEs in this release, one square each
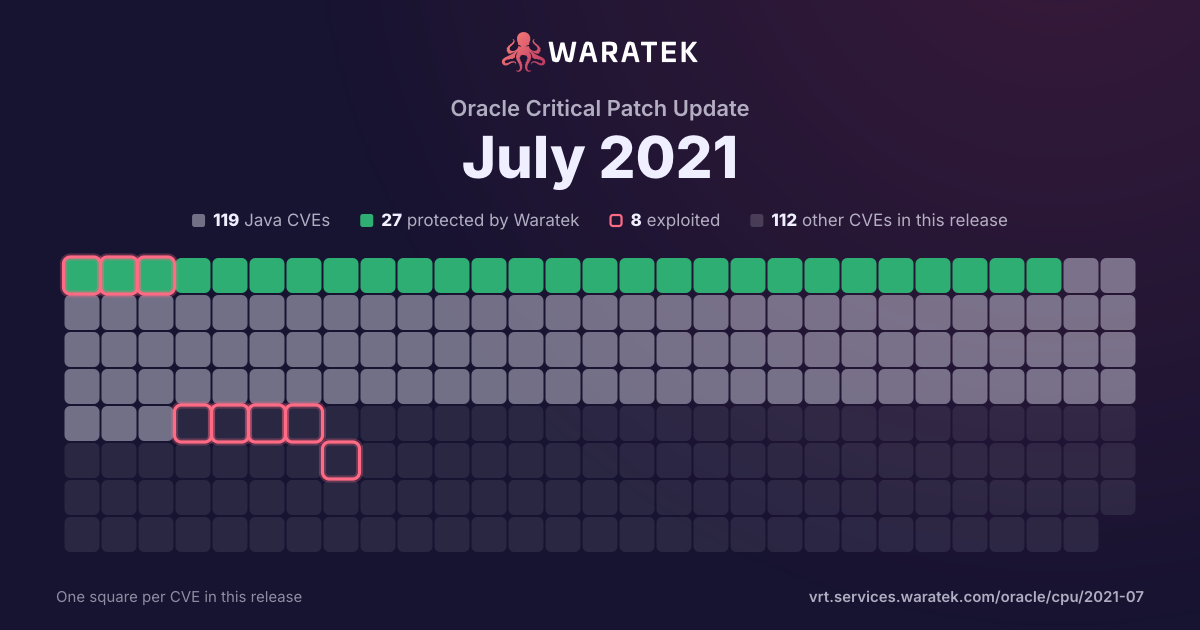
By status
27Protected by Waratek2Mitigation candidate90No exploit published33Outside Waratek scope79Not applicable
8Exploited, marked by the ring
No exploit published. For 70 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 204 matches · 92 in Waratek scope · 0 protected · 5 exploited · 2 CISA KEV · 13 public PoC · 13 EPSS ≥ 0.5
204matches
92in Waratek scope45.1%
0protected0.0%
5exploited2.5%
2CISA KEV1.0%
13public PoC6.4%
13EPSS ≥ 0.56.4%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
2
1.0%
No exploit published
90
44.1%
Outside Waratek scope
33
16.2%
Not applicable
79
38.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
204
100.0%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 128 / quarter
Q2 161
Not applicable1
Medium1
not blocked1
No public exploit1
Q3 160
Q4 160
Q1 170
Q2 172
No exploit published1
Not applicable1
Critical1
High1
not blocked2
No public exploit2
Q3 171
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q4 173
No exploit published1
Outside Waratek scope1
Not applicable1
Critical1
High2
not blocked3
Working exploit published1
No public exploit2
Q1 182
Outside Waratek scope1
Not applicable1
Critical1
Medium1
not blocked2
No public exploit2
Q2 180
Q3 180
Q4 181
Outside Waratek scope1
High1
not blocked1
Working exploit published1
Q1 191
Not applicable1
High1
not blocked1
Exploited1
Q2 191
Outside Waratek scope1
Medium1
not blocked1
Exploited1
Q3 195
No exploit published1
Outside Waratek scope3
Not applicable1
Critical3
High1
Medium1
not blocked5
No public exploit5
Q4 194
No exploit published1
Outside Waratek scope1
Not applicable2
Critical2
High1
Medium1
not blocked4
Proof of concept only1
No public exploit3
Q1 205
No exploit published2
Outside Waratek scope2
Not applicable1
Critical1
High4
not blocked5
Proof of concept only1
No public exploit4
Q2 206
Outside Waratek scope6
High3
Medium3
not blocked6
Exploited2
No public exploit4
Q3 207
Mitigation candidate1
No exploit published3
Not applicable3
Critical1
High3
Medium3
not blocked7
Working exploit published1
No public exploit6
Q4 2018
No exploit published8
Outside Waratek scope7
Not applicable3
High11
Medium6
Low1
not blocked18
Proof of concept only3
No public exploit15
Q1 2116
No exploit published9
Outside Waratek scope5
Not applicable2
Critical1
High8
Medium7
not blocked16
Exploited1
Proof of concept only2
No public exploit13
Q2 213
No exploit published1
Outside Waratek scope2
Critical2
High1
not blocked3
Forecast only1
No public exploit2
Q3 21128
Mitigation candidate1
No exploit published63
Outside Waratek scope2
Not applicable62
Critical7
High48
Medium65
Low8
not blocked128
Proof of concept only1
Forecast only2
No public exploit125
Q3 16Q1 17Q3 17Q1 18Q3 18Q1 19Q3 19Q1 20Q3 20Q1 21Q3 21
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-0762 | Medium | 2017-08-10 | Outside Waratek scope | No public exploit | The Realm implementations in Apache Tomcat versions 9.0.0.M1 to 9.0.0.M9, 8.5.0 to 8.5.4, 8.0.0.RC1 to 8.0.36, 7.0.0 to 7.0.70 and 6.0.0 to 6.0.45 did not process the supplied password if the supplied user name did not exist. This made a timing attack possible to determine valid user names. Note that the default configuration includes the LockOutRealm which makes exploitation of this vulnerability harder. |
| CVE-2017-9735 | High | 2017-06-16 | No exploit published | No public exploit | Jetty through 9.4.x is prone to a timing channel in util/security/Password.java, which makes it easier for remote attackers to obtain access by observing elapsed times before rejection of incorrect passwords. |
| CVE-2017-5461 | Critical | 2017-05-11 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.21.4, 3.22.x through 3.28.x before 3.28.4, 3.29.x before 3.29.5, and 3.30.x before 3.30.1 allows remote attackers to cause a denial of service (out-of-bounds write) or possibly have unspecified other impact by leveraging incorrect base64 operations. |
| CVE-2016-4429 | Medium | 2016-06-10 | Not applicable | No public exploit | Stack-based buffer overflow in the clntudp_call function in sunrpc/clnt_udp.c in the GNU C Library (aka glibc or libc6) allows remote servers to cause a denial of service (crash) or possibly unspecified other impact via a flood of crafted ICMP and UDP packets. |