
Oracle Critical Patch Update July 2021
Released July 2021 · Oracle's advisory ↗ · ← Critical Patch Update, April 2021 · Critical Patch Update, October 2021 →
231 CVEs in this release, one square each
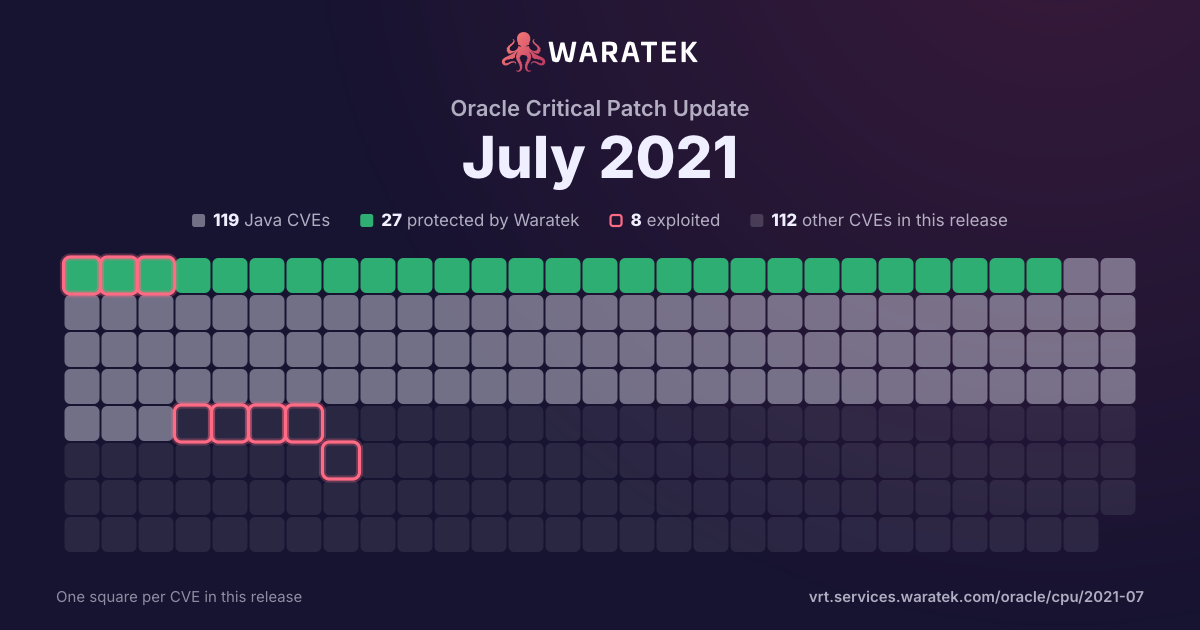
By status
27Protected by Waratek2Mitigation candidate90No exploit published33Outside Waratek scope79Not applicable
8Exploited, marked by the ring
No exploit published. For 70 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 109 matches · 21 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
21
19.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
88
80.7%
blocked by ARMR today
21
19.3%
partly blocked
0
0.0%
not blocked
88
80.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
109
100.0%
split by
peak 77 / year
20151
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
20160
20173
Protected by Waratek1
No exploit published2
High2
Medium1
blocked by ARMR today1
not blocked2
No public exploit3
20180
20195
Protected by Waratek3
No exploit published2
Critical1
High2
Medium2
blocked by ARMR today3
not blocked2
No public exploit5
202023
Protected by Waratek10
No exploit published13
Critical4
High14
Medium4
Low1
blocked by ARMR today10
not blocked13
No public exploit23
202177
Protected by Waratek6
No exploit published71
Critical5
High36
Medium33
Low3
blocked by ARMR today6
not blocked71
No public exploit77
2015201620172018201920202021
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-12415 | Medium | 2019-10-23 | Protected by Waratek | No public exploit | In Apache POI up to 4.1.0, when using the tool XSSFExportToXml to convert user-provided Microsoft Excel documents, a specially crafted document can allow an attacker to read files from the local filesystem or from internal network resources via XML External Entity (XXE) Processing. |
| CVE-2019-2897 | Medium | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Fusion Middleware (component: Analytics Actions). Supported versions that are affected are 12.2.1.3.0 and 12.2.1.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Business Intelligence Enterprise Edition. While the vulnerability is in Oracle Business Intelligence Enterprise Edition, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Business Intelligence Enterprise Edition accessible data as well as unauthorized read access to a subset of Oracle Business Intelligence Enterprise Edition accessible data. CVSS 3.0 Base Score 6.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:N). |
| CVE-2019-12402 | High | 2019-08-30 | No exploit published | No public exploit | The file name encoding algorithm used internally in Apache Commons Compress 1.15 to 1.18 can get into an infinite loop when faced with specially crafted inputs. This can lead to a denial of service attack if an attacker can choose the file names inside of an archive created by Compress. |
| CVE-2019-10086 | High | 2019-08-20 | Protected by Waratek | No public exploit | In Apache Commons Beanutils 1.9.2, a special BeanIntrospector class was added which allows suppressing the ability for an attacker to access the classloader via the class property available on all Java objects. We, however were not using this by default characteristic of the PropertyUtilsBean. |
| CVE-2019-0228 | Critical | 2019-04-17 | Protected by Waratek | No public exploit | Apache PDFBox 2.0.14 does not properly initialize the XML parser, which allows context-dependent attackers to conduct XML External Entity (XXE) attacks via a crafted XFDF. |
| CVE-2012-0881 | High | 2017-10-30 | No exploit published | No public exploit | Apache Xerces2 Java Parser before 2.12.0 allows remote attackers to cause a denial of service (CPU consumption) via a crafted message to an XML service, which triggers hash table collisions. |
| CVE-2017-14735 | Medium | 2017-09-25 | Protected by Waratek | No public exploit | OWASP AntiSamy before 1.5.7 allows XSS via HTML5 entities, as demonstrated by use of : to construct a javascript: URL. |
| CVE-2017-9735 | High | 2017-06-16 | No exploit published | No public exploit | Jetty through 9.4.x is prone to a timing channel in util/security/Password.java, which makes it easier for remote attackers to obtain access by observing elapsed times before rejection of incorrect passwords. |
| CVE-2015-0254 | High | 2015-03-09 | Protected by Waratek | No public exploit | Apache Standard Taglibs before 1.2.3 allows remote attackers to execute arbitrary code or conduct external XML entity (XXE) attacks via a crafted XSLT extension in a (1) <x:parse> or (2) <x:transform> JSTL XML tag. |