
Oracle Critical Patch Update July 2021
Released July 2021 · Oracle's advisory ↗ · ← Critical Patch Update, April 2021 · Critical Patch Update, October 2021 →
231 CVEs in this release, one square each
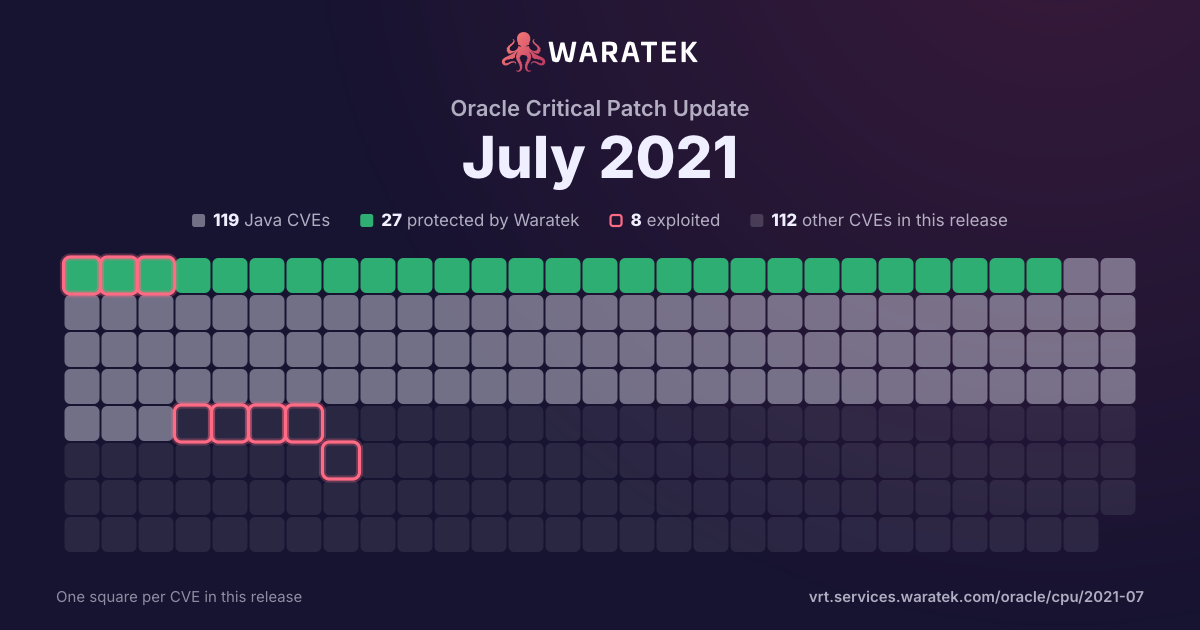
By status
27Protected by Waratek2Mitigation candidate90No exploit published33Outside Waratek scope79Not applicable
8Exploited, marked by the ring
No exploit published. For 70 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 9 matches · 2 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 7 public PoC · 4 EPSS ≥ 0.5
9matches
2in Waratek scope22.2%
1protected11.1%
0exploited0.0%
0CISA KEV0.0%
7public PoC77.8%
4EPSS ≥ 0.544.4%
Protected by Waratek
1
11.1%
Rule in development
0
0.0%
Mitigation candidate
1
11.1%
No exploit published
0
0.0%
Outside Waratek scope
5
55.6%
Not applicable
2
22.2%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
11.1%
partly blocked
0
0.0%
not blocked
8
88.9%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
9
100.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 3 / quarter
Q4 191
Outside Waratek scope1
Critical1
not blocked1
Proof of concept only1
Q1 201
Outside Waratek scope1
High1
not blocked1
Proof of concept only1
Q2 200
Q3 200
Q4 203
Outside Waratek scope1
Not applicable2
High2
Medium1
not blocked3
Proof of concept only3
Q1 212
Outside Waratek scope2
Critical1
High1
not blocked2
Proof of concept only2
Q2 210
Q3 212
Protected by Waratek1
Mitigation candidate1
Critical2
blocked by ARMR today1
not blocked1
Proof of concept only2
Q4 19Q1 20Q2 20Q3 20Q4 20Q1 21Q2 21Q3 21
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2021-2456 | Critical | 2021-07-21 | Mitigation candidate | Proof of concept only | Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Fusion Middleware (component: Analytics Web General). The supported version that is affected is 12.2.1.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Business Intelligence Enterprise Edition. Successful attacks of this vulnerability can result in takeover of Oracle Business Intelligence Enterprise Edition. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2021-2394 | Critical | 2021-07-21 | Protected by Waratek | Proof of concept only | Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Supported versions that are affected are 10.3.6.0.0, 12.1.3.0.0, 12.2.1.3.0, 12.2.1.4.0 and 14.1.1.0.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via T3, IIOP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in takeover of Oracle WebLogic Server. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2021-3345 | High | 2021-01-29 | Outside Waratek scope | Proof of concept only | _gcry_md_block_write in cipher/hash-common.c in Libgcrypt version 1.9.0 has a heap-based buffer overflow when the digest final function sets a large count value. It is recommended to upgrade to 1.9.1 or later. |
| CVE-2021-3177 | Critical | 2021-01-19 | Outside Waratek scope | Proof of concept only | Python 3.x through 3.9.1 has a buffer overflow in PyCArg_repr in _ctypes/callproc.c, which may lead to remote code execution in certain Python applications that accept floating-point numbers as untrusted input, as demonstrated by a 1e300 argument to c_double.from_param. This occurs because sprintf is used unsafely. |
| CVE-2020-8285 | High | 2020-12-14 | Not applicable | Proof of concept only | curl 7.21.0 to and including 7.73.0 is vulnerable to uncontrolled recursion due to a stack overflow issue in FTP wildcard match parsing. |
| CVE-2020-1971 | Medium | 2020-12-08 | Outside Waratek scope | Proof of concept only | The X.509 GeneralName type is a generic type for representing different types of names. One of those name types is known as EDIPartyName. OpenSSL provides a function GENERAL_NAME_cmp which compares different instances of a GENERAL_NAME to see if they are equal or not. This function behaves incorrectly when both GENERAL_NAMEs contain an EDIPARTYNAME. A NULL pointer dereference and a crash may occur leading to a possible denial of service attack. OpenSSL itself uses the GENERAL_NAME_cmp function for two purposes: 1) Comparing CRL distribution point names between an available CRL and a CRL distribution point embedded in an X509 certificate 2) When verifying that a timestamp response token signer matches the timestamp authority name (exposed via the API functions TS_RESP_verify_response and TS_RESP_verify_token) If an attacker can control both items being compared then that attacker could trigger a crash. For example if the attacker can trick a client or server into checking a malicious certificate against a malicious CRL then this may occur. Note that some applications automatically download CRLs based on a URL embedded in a certificate. This checking happens prior to the signatures on the certificate and CRL being verified. OpenSSL's s_server, s_client and verify tools have support for the "-crl_download" option which implements automatic CRL downloading and this attack has been demonstrated to work against those tools. Note that an unrelated bug means that affected versions of OpenSSL cannot parse or construct correct encodings of EDIPARTYNAME. However it is possible to construct a malformed EDIPARTYNAME that OpenSSL's parser will accept and hence trigger this attack. All OpenSSL 1.1.1 and 1.0.2 versions are affected by this issue. Other OpenSSL releases are out of support and have not been checked. Fixed in OpenSSL 1.1.1i (Affected 1.1.1-1.1.1h). Fixed in OpenSSL 1.0.2x (Affected 1.0.2-1.0.2w). |
| CVE-2020-8277 | High | 2020-11-19 | Not applicable | Proof of concept only | A Node.js application that allows an attacker to trigger a DNS request for a host of their choice could trigger a Denial of Service in versions < 15.2.1, < 14.15.1, and < 12.19.1 by getting the application to resolve a DNS record with a larger number of responses. This is fixed in 15.2.1, 14.15.1, and 12.19.1. |
| CVE-2020-5398 | High | 2020-01-17 | Outside Waratek scope | Proof of concept only | In Spring Framework, versions 5.2.x prior to 5.2.3, versions 5.1.x prior to 5.1.13, and versions 5.0.x prior to 5.0.16, an application is vulnerable to a reflected file download (RFD) attack when it sets a "Content-Disposition" header in the response where the filename attribute is derived from user supplied input. |
| CVE-2019-17195 | Critical | 2019-10-15 | Outside Waratek scope | Proof of concept only | Connect2id Nimbus JOSE+JWT before v7.9 can throw various uncaught exceptions while parsing a JWT, which could result in an application crash (potential information disclosure) or a potential authentication bypass. |