
WaratekVRT Sign in

Oracle Critical Patch Update July 2021

Released July 2021 · Oracle's advisory ↗ · ← Critical Patch Update, April 2021 · Critical Patch Update, October 2021 →

231 CVEs in this release, one square each
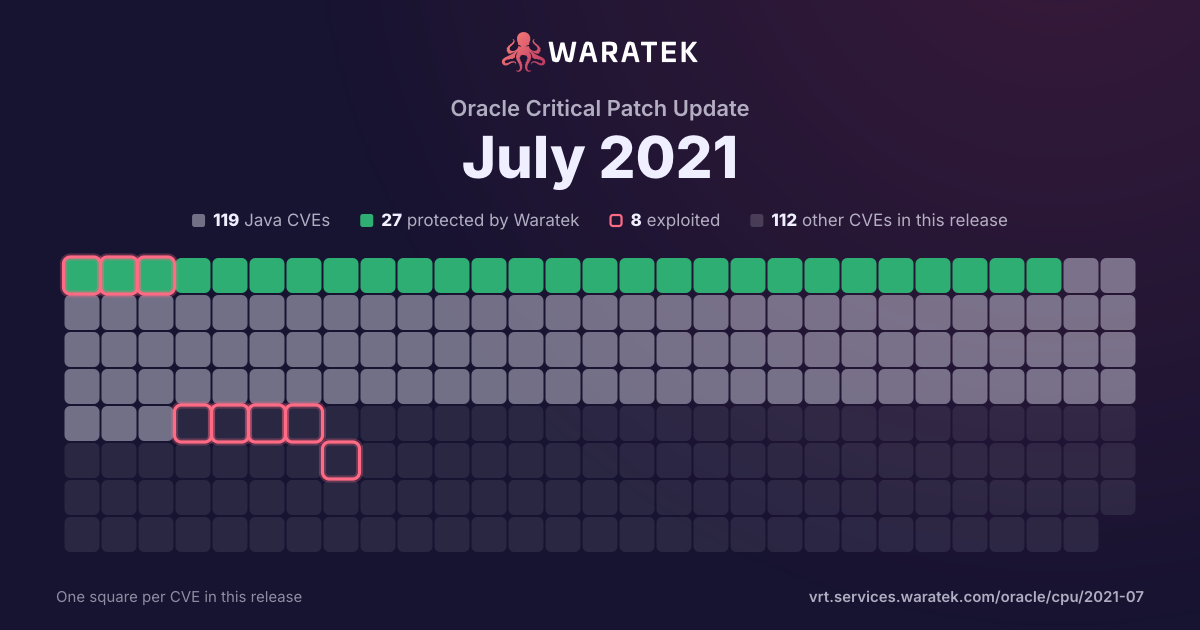
Protected by Waratek, exploitedProtected by Waratek, exploitedProtected by Waratek, exploitedProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekMitigation candidateMitigation candidateNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedOutside Waratek scope, exploitedOutside Waratek scope, exploitedOutside Waratek scope, exploitedOutside Waratek scope, exploitedOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeNot applicable, exploitedNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicable
Share this chart Oracle Critical Patch Update July 2021, one square per CVE: 119 Java CVEs, 27 protected by Waratek, 8 exploited, 112 other CVEs in this release.

Download the image

By status

No exploit published. For 70 of them, Oracle's security advisory is the source of public detail.

Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.

Reset
More filters
Columns
Including CVEs outside Waratek scope✕
Overview 3 matches · 2 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC
3matches 2in Waratek scope66.7% 0protected0.0% 0exploited0.0% 0CISA KEV0.0% 0public PoC0.0%
Protected by Waratek 0 0.0% Rule in development 0 0.0% Mitigation candidate 0 0.0% No exploit published 2 66.7% Outside Waratek scope 1 33.3% Not applicable 0 0.0% Withdrawn CVE 0 0.0%
Critical 0 0.0% High 2 66.7% Medium 1 33.3% Low 0 0.0% None 0 0.0% Unknown 0 0.0%
blocked by ARMR today 0 0.0% partly blocked 0 0.0% not blocked 3 100.0% not established 0 0.0% unrecorded 0 0.0%
Exploited 0 0.0% Working exploit published 0 0.0% Proof of concept only 0 0.0% Forecast only 3 100.0% No public exploit 0 0.0%
split by peak 2 / month
Outside Waratek scope: 1No exploit published: 2 Medium: 1High: 2 not blocked: 3 Forecast only: 3
Jun 21Jul 21
3 matches Sign in to download these CVEs as CSV or JSON, or to follow them in a feed.
CVE Severity Published▾ Status Exploitation Description
CVE-2021-2401 Medium 2021-07-21 No exploit published Forecast only Vulnerability in the Oracle BI Publisher product of Oracle Fusion Middleware (component: E-Business Suite - XDO). Supported versions that are affected are 5.5.0.0.0, 11.1.1.9.0, 12.2.1.3.0 and 12.2.1.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle BI Publisher. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle BI Publisher accessible data. CVSS 3.1 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N).
CVE-2021-2400 High 2021-07-21 No exploit published Forecast only Vulnerability in the Oracle BI Publisher product of Oracle Fusion Middleware (component: E-Business Suite - XDO). Supported versions that are affected are 5.5.0.0.0, 11.1.1.9.0, 12.2.1.3.0 and 12.2.1.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle BI Publisher. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle BI Publisher accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N).
CVE-2021-22901 High 2021-06-11 Outside Waratek scope Forecast only curl 7.75.0 through 7.76.1 suffers from a use-after-free vulnerability resulting in already freed memory being used when a TLS 1.3 session ticket arrives over a connection. A malicious server can use this in rare unfortunate circumstances to potentially reach remote code execution in the client. When libcurl at run-time sets up support for TLS 1.3 session tickets on a connection using OpenSSL, it stores pointers to the transfer in-memory object for later retrieval when a session ticket arrives. If the connection is used by multiple transfers (like with a reused HTTP/1.1 connection or multiplexed HTTP/2 connection) that first transfer object might be freed before the new session is established on that connection and then the function will access a memory buffer that might be freed. When using that memory, libcurl might even call a function pointer in the object, making it possible for a remote code execution if the server could somehow manage to get crafted memory content into the correct place in memory.