
Oracle Critical Patch Update April 2020
Released April 2020 · Oracle's advisory ↗ · ← Critical Patch Update, January 2020 · Critical Patch Update, July 2020 →
300 CVEs in this release, one square each
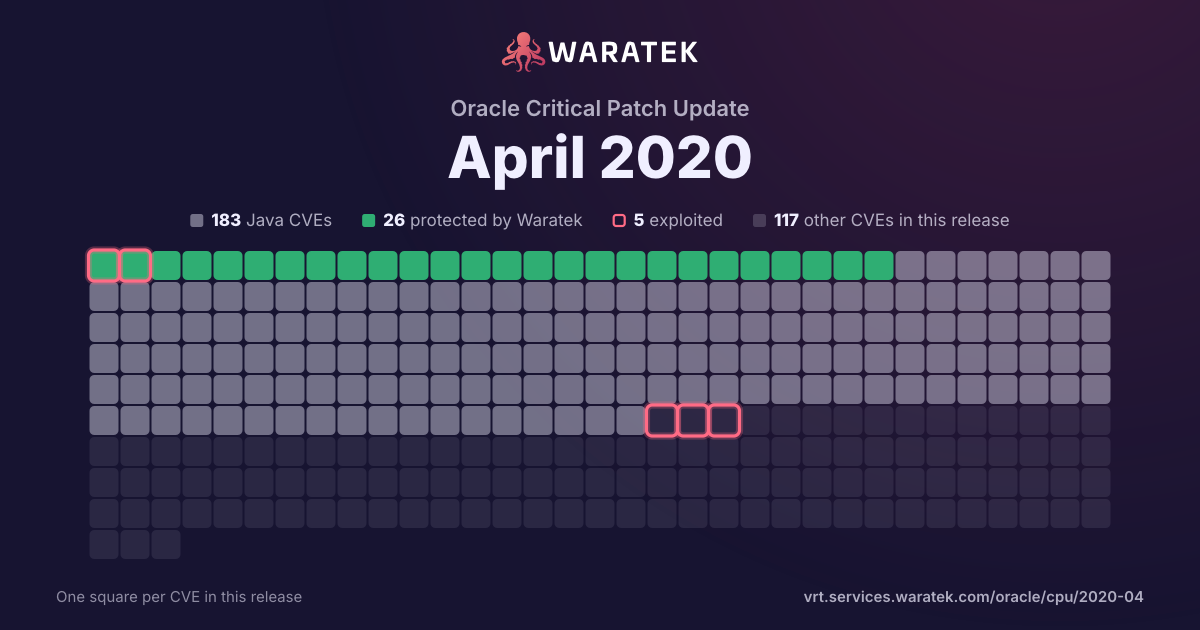
By status
26Protected by Waratek1Mitigation candidate156No exploit published60Outside Waratek scope56Not applicable1Withdrawn CVE
5Exploited, marked by the ring
No exploit published. For 141 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 2 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
2matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
2
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
2
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
2
100.0%
split by
peak 1 / month
Apr 17May 17Jun 17Jul 17Aug 17Sep 17Oct 17Nov 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-5533 | Critical | 2017-11-15 | Not applicable | No public exploit | A vulnerability in the server content cache of TIBCO JasperReports Server, TIBCO JasperReports Server Community Edition, TIBCO JasperReports Server for ActiveMatrix BPM, TIBCO Jaspersoft for AWS with Multi-Tenancy, and TIBCO Jaspersoft Reporting and Analytics for AWS contains a vulnerability which fails to prevent remote access to all the contents of the web application, including key configuration files. Affected releases are TIBCO JasperReports Server 6.4.0, TIBCO JasperReports Server Community Edition 6.4.0, TIBCO JasperReports Server for ActiveMatrix BPM 6.4.0, TIBCO Jaspersoft for AWS with Multi-Tenancy 6.4.0, TIBCO Jaspersoft Reporting and Analytics for AWS 6.4.0. |
| CVE-2016-10328 | Critical | 2017-04-14 | Not applicable | No public exploit | FreeType 2 before 2016-12-16 has an out-of-bounds write caused by a heap-based buffer overflow related to the cff_parser_run function in cff/cffparse.c. |