
Oracle Critical Patch Update April 2020
Released April 2020 · Oracle's advisory ↗ · ← Critical Patch Update, January 2020 · Critical Patch Update, July 2020 →
300 CVEs in this release, one square each
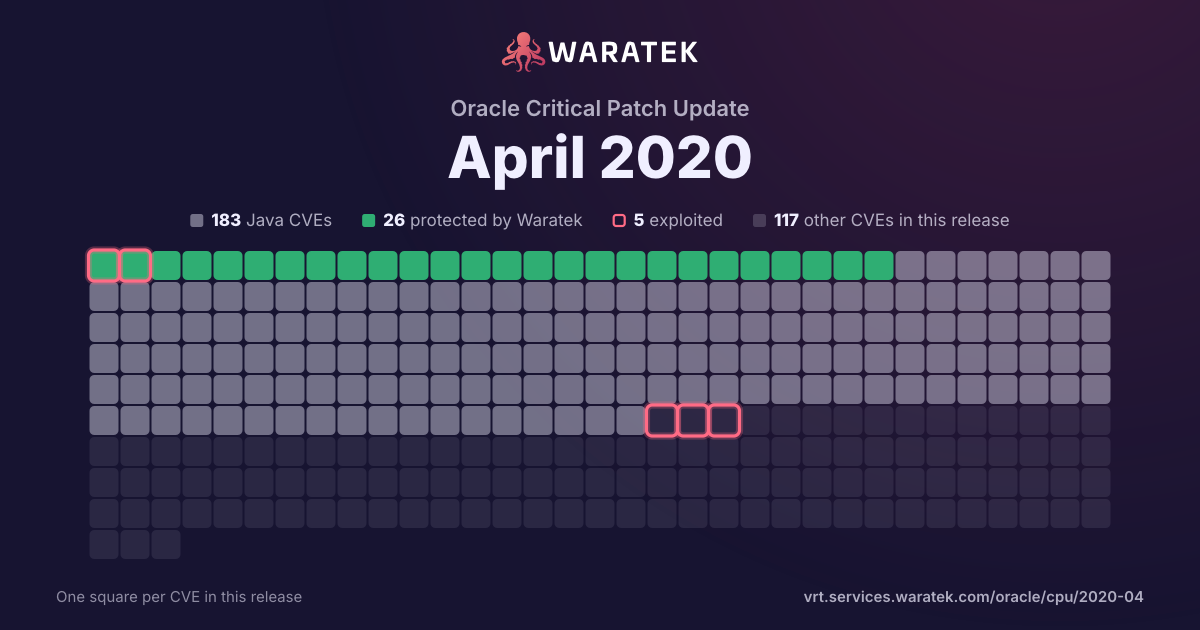
By status
28Protected by Waratek7Mitigation candidate166No exploit published6Outside Waratek scope92Not applicable1Withdrawn CVE
5Exploited, marked by the ring
No exploit published. For 145 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 9 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 1 EPSS ≥ 0.5
9matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
1EPSS ≥ 0.511.1%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
9
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
9
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
1
11.1%
No public exploit
8
88.9%
split by
peak 4 / quarter
Q1 171
Not applicable1
High1
not blocked1
No public exploit1
Q2 171
Not applicable1
Critical1
not blocked1
No public exploit1
Q3 170
Q4 171
Not applicable1
Critical1
not blocked1
No public exploit1
Q1 184
Not applicable4
High3
Medium1
not blocked4
Forecast only1
No public exploit3
Q2 180
Q3 180
Q4 182
Not applicable2
Critical1
Medium1
not blocked2
No public exploit2
Q1 17Q2 17Q3 17Q4 17Q1 18Q2 18Q3 18Q4 18
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-20622 | Medium | 2018-12-31 | Not applicable | No public exploit | JasPer 2.0.14 has a memory leak in base/jas_malloc.c in libjasper.a when "--output-format jp2" is used. |
| CVE-2018-18311 | Critical | 2018-12-07 | Not applicable | No public exploit | Perl before 5.26.3 and 5.28.x before 5.28.1 has a buffer overflow via a crafted regular expression that triggers invalid write operations. |
| CVE-2018-1165 | High | 2018-02-21 | Not applicable | No public exploit | This vulnerability allows local attackers to escalate privileges on vulnerable installations of Joyent SmartOS release-20170803-20170803T064301Z. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The specific flaw exists within the SMB_IOC_SVCENUM IOCTL. The issue results from the lack of proper validation of the length of user-supplied data prior to copying it to a fixed-length, heap-based buffer. An attacker can leverage this vulnerability to execute code under the context of the host OS. Was ZDI-CAN-4983. |
| CVE-2017-5130 | High | 2018-02-07 | Not applicable | No public exploit | An integer overflow in xmlmemory.c in libxml2 before 2.9.5, as used in Google Chrome prior to 62.0.3202.62 and other products, allowed a remote attacker to potentially exploit heap corruption via a crafted XML file. |
| CVE-2017-3160 | High | 2018-02-01 | Not applicable | No public exploit | After the Android platform is added to Cordova the first time, or after a project is created using the build scripts, the scripts will fetch Gradle on the first build. However, since the default URI is not using https, it is vulnerable to a MiTM and the Gradle executable is not safe. The severity of this issue is high due to the fact that the build scripts immediately start a build after Gradle has been fetched. Developers who are concerned about this issue should install version 6.1.2 or higher of Cordova-Android. If developers are unable to install the latest version, this vulnerability can easily be mitigated by setting the CORDOVA_ANDROID_GRADLE_DISTRIBUTION_URL environment variable to https://services.gradle.org/distributions/gradle-2.14.1-all.zip |
| CVE-2018-5712 | Medium | 2018-01-16 | Not applicable | Forecast only | An issue was discovered in PHP before 5.6.33, 7.0.x before 7.0.27, 7.1.x before 7.1.13, and 7.2.x before 7.2.1. There is Reflected XSS on the PHAR 404 error page via the URI of a request for a .phar file. |
| CVE-2017-5533 | Critical | 2017-11-15 | Not applicable | No public exploit | A vulnerability in the server content cache of TIBCO JasperReports Server, TIBCO JasperReports Server Community Edition, TIBCO JasperReports Server for ActiveMatrix BPM, TIBCO Jaspersoft for AWS with Multi-Tenancy, and TIBCO Jaspersoft Reporting and Analytics for AWS contains a vulnerability which fails to prevent remote access to all the contents of the web application, including key configuration files. Affected releases are TIBCO JasperReports Server 6.4.0, TIBCO JasperReports Server Community Edition 6.4.0, TIBCO JasperReports Server for ActiveMatrix BPM 6.4.0, TIBCO Jaspersoft for AWS with Multi-Tenancy 6.4.0, TIBCO Jaspersoft Reporting and Analytics for AWS 6.4.0. |
| CVE-2016-10328 | Critical | 2017-04-14 | Not applicable | No public exploit | FreeType 2 before 2016-12-16 has an out-of-bounds write caused by a heap-based buffer overflow related to the cff_parser_run function in cff/cffparse.c. |
| CVE-2016-10251 | High | 2017-03-15 | Not applicable | No public exploit | Integer overflow in the jpc_pi_nextcprl function in jpc_t2cod.c in JasPer before 1.900.20 allows remote attackers to have unspecified impact via a crafted file, which triggers use of an uninitialized value. |