
Oracle Critical Patch Update April 2020
Released April 2020 · Oracle's advisory ↗ · ← Critical Patch Update, January 2020 · Critical Patch Update, July 2020 →
300 CVEs in this release, one square each
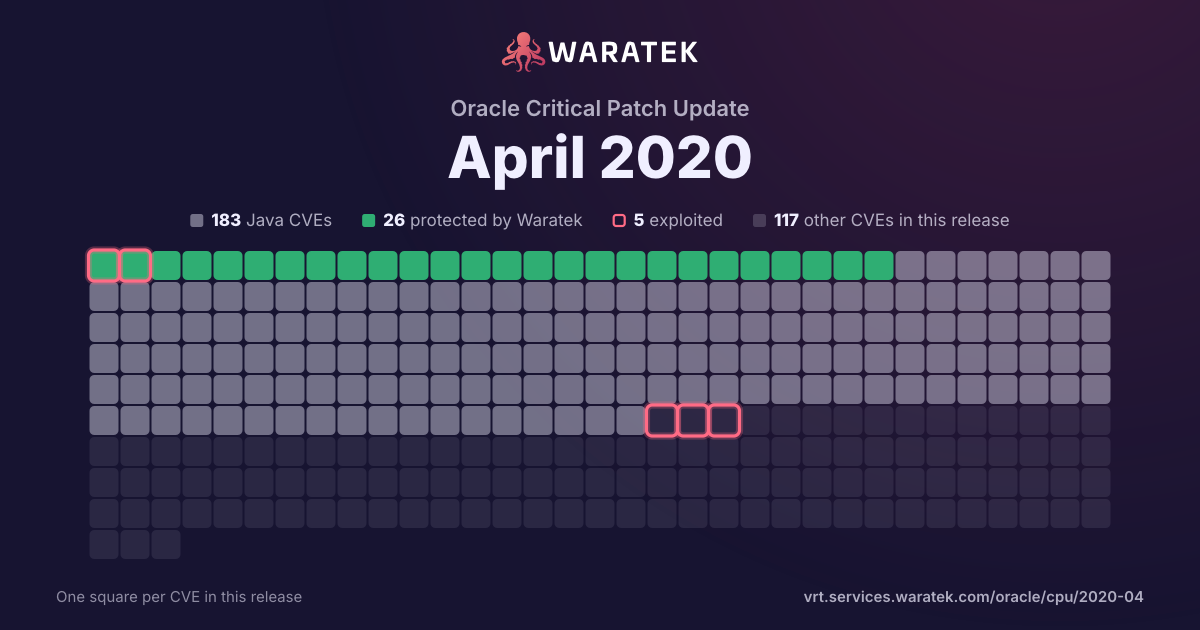
By status
28Protected by Waratek7Mitigation candidate166No exploit published6Outside Waratek scope92Not applicable1Withdrawn CVE
5Exploited, marked by the ring
No exploit published. For 145 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 9 matches · 7 in Waratek scope · 2 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
9matches
7in Waratek scope77.8%
2protected22.2%
0exploited0.0%
0CISA KEV0.0%
1public PoC11.1%
0EPSS ≥ 0.50.0%
Protected by Waratek
2
22.2%
Rule in development
0
0.0%
Mitigation candidate
1
11.1%
No exploit published
4
44.4%
Outside Waratek scope
0
0.0%
Not applicable
2
22.2%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
22.2%
partly blocked
0
0.0%
not blocked
7
77.8%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
11.1%
Forecast only
0
0.0%
No public exploit
8
88.9%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-12415 | Medium | 2019-10-23 | Protected by Waratek | No public exploit | In Apache POI up to 4.1.0, when using the tool XSSFExportToXml to convert user-provided Microsoft Excel documents, a specially crafted document can allow an attacker to read files from the local filesystem or from internal network resources via XML External Entity (XXE) Processing. |
| CVE-2019-18197 | High | 2019-10-18 | Not applicable | No public exploit | In xsltCopyText in transform.c in libxslt 1.1.33, a pointer variable isn't reset under certain circumstances. If the relevant memory area happened to be freed and reused in a certain way, a bounds check could fail and memory outside a buffer could be written to, or uninitialized data could be disclosed. |
| CVE-2019-2904 | Critical | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Oracle JDeveloper and ADF product of Oracle Fusion Middleware (component: ADF Faces). Supported versions that are affected are 11.1.1.9.0, 12.1.3.0.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle JDeveloper and ADF. Successful attacks of this vulnerability can result in takeover of Oracle JDeveloper and ADF. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-2899 | Low | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Oracle JDeveloper and ADF product of Oracle Fusion Middleware (component: OAM). Supported versions that are affected are 11.1.1.9.0, 11.1.2.4.0, 12.1.3.0.0 and 12.2.1.3.0. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle JDeveloper and ADF. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle JDeveloper and ADF accessible data. CVSS 3.0 Base Score 2.4 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:N/A:N). |
| CVE-2019-17195 | Critical | 2019-10-15 | Mitigation candidate | Proof of concept only | Connect2id Nimbus JOSE+JWT before v7.9 can throw various uncaught exceptions while parsing a JWT, which could result in an application crash (potential information disclosure) or a potential authentication bypass. |
| CVE-2019-17359 | High | 2019-10-08 | No exploit published | No public exploit | The ASN.1 parser in Bouncy Castle Crypto (aka BC Java) 1.63 can trigger a large attempted memory allocation, and resultant OutOfMemoryError error, via crafted ASN.1 data. This is fixed in 1.64. |
| CVE-2019-15163 | High | 2019-10-03 | Not applicable | No public exploit | rpcapd/daemon.c in libpcap before 1.9.1 allows attackers to cause a denial of service (NULL pointer dereference and daemon crash) if a crypt() call fails. |
| CVE-2019-17091 | Medium | 2019-10-02 | Protected by Waratek | No public exploit | faces/context/PartialViewContextImpl.java in Eclipse Mojarra, as used in Mojarra for Eclipse EE4J before 2.3.10 and Mojarra JavaServer Faces before 2.2.20, allows Reflected XSS because a client window field is mishandled. |
| CVE-2019-16943 | Critical | 2019-10-01 | No exploit published | No public exploit | A Polymorphic Typing issue was discovered in FasterXML jackson-databind 2.0.0 through 2.9.10. When Default Typing is enabled (either globally or for a specific property) for an externally exposed JSON endpoint and the service has the p6spy (3.8.6) jar in the classpath, and an attacker can find an RMI service endpoint to access, it is possible to make the service execute a malicious payload. This issue exists because of com.p6spy.engine.spy.P6DataSource mishandling. |