
Oracle Critical Patch Update April 2020
Released April 2020 · Oracle's advisory ↗ · ← Critical Patch Update, January 2020 · Critical Patch Update, July 2020 →
300 CVEs in this release, one square each
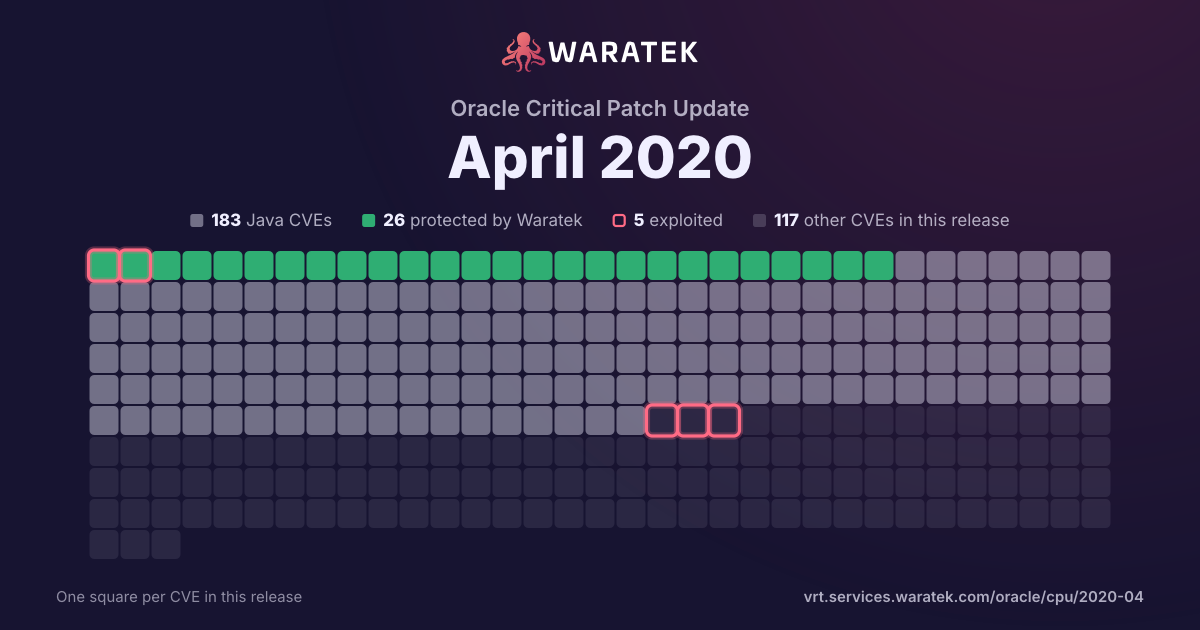
By status
28Protected by Waratek7Mitigation candidate166No exploit published6Outside Waratek scope92Not applicable1Withdrawn CVE
5Exploited, marked by the ring
No exploit published. For 145 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 2 matches · 1 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
50.0%
Outside Waratek scope
0
0.0%
Not applicable
1
50.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
2
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
2
100.0%
No public exploit
0
0.0%
split by
peak 1 / month
Feb 18Apr 18Jun 18Aug 18Oct 18Dec 18Feb 19Apr 19Jun 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-10072 | High | 2019-06-21 | No exploit published | Forecast only | The fix for CVE-2019-0199 was incomplete and did not address HTTP/2 connection window exhaustion on write in Apache Tomcat versions 9.0.0.M1 to 9.0.19 and 8.5.0 to 8.5.40 . By not sending WINDOW_UPDATE messages for the connection window (stream 0) clients were able to cause server-side threads to block eventually leading to thread exhaustion and a DoS. |
| CVE-2018-5712 | Medium | 2018-01-16 | Not applicable | Forecast only | An issue was discovered in PHP before 5.6.33, 7.0.x before 7.0.27, 7.1.x before 7.1.13, and 7.2.x before 7.2.1. There is Reflected XSS on the PHAR 404 error page via the URI of a request for a .phar file. |