
Oracle Critical Patch Update January 2020
Released January 2020 · Oracle's advisory ↗ · ← Critical Patch Update, October 2019 · Critical Patch Update, April 2020 →
255 CVEs in this release, one square each
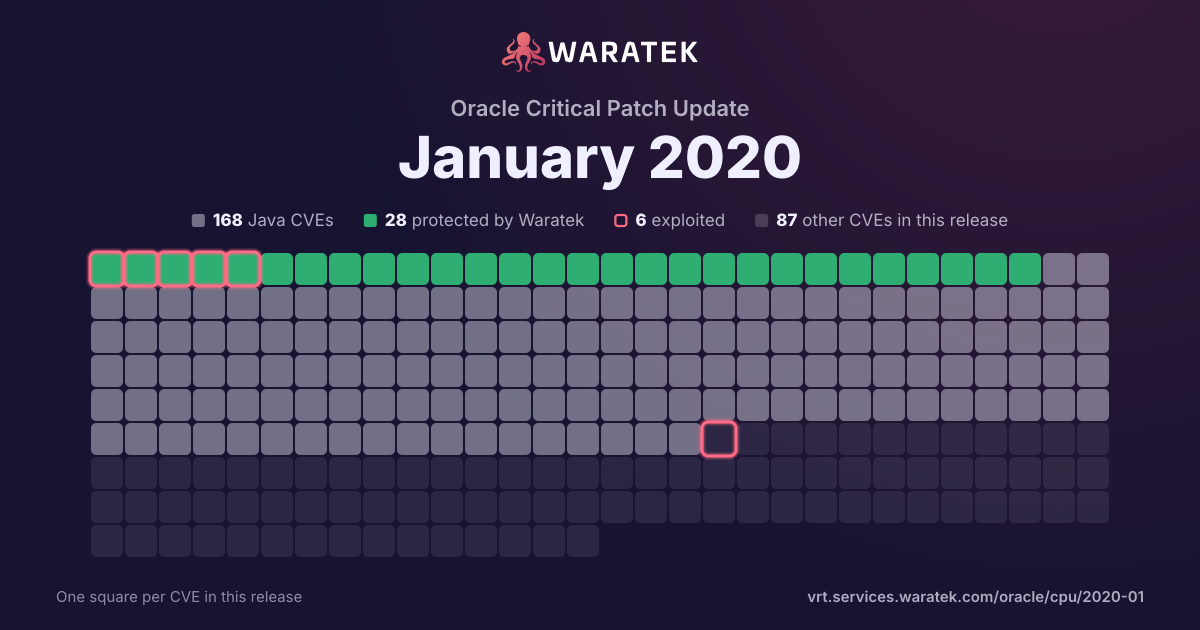
By status
29Protected by Waratek3Mitigation candidate145No exploit published9Outside Waratek scope69Not applicable
6Exploited, marked by the ring
No exploit published. For 135 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 3 in Waratek scope · 2 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
4matches
3in Waratek scope75.0%
2protected50.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC25.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
2
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
25.0%
Outside Waratek scope
0
0.0%
Not applicable
1
25.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
50.0%
partly blocked
0
0.0%
not blocked
2
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
25.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
3
75.0%
split by
peak 1 / year
20121
No exploit published1
Medium1
not blocked1
No public exploit1
20130
20141
Protected by Waratek1
Medium1
blocked by ARMR today1
Working exploit published1
20150
20160
20171
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
20181
Not applicable1
Medium1
not blocked1
No public exploit1
2012201320142015201620172018
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-0734 | Medium | 2018-10-30 | Not applicable | No public exploit | The OpenSSL DSA signature algorithm has been shown to be vulnerable to a timing side channel attack. An attacker could use variations in the signing algorithm to recover the private key. Fixed in OpenSSL 1.1.1a (Affected 1.1.1). Fixed in OpenSSL 1.1.0j (Affected 1.1.0-1.1.0i). Fixed in OpenSSL 1.0.2q (Affected 1.0.2-1.0.2p). |
| CVE-2017-14735 | Medium | 2017-09-25 | Protected by Waratek | No public exploit | OWASP AntiSamy before 1.5.7 allows XSS via HTML5 entities, as demonstrated by use of : to construct a javascript: URL. |
| CVE-2014-3004 | Medium | 2014-06-11 | Protected by Waratek | Working exploit published | The default configuration for the Xerces SAX Parser in Castor before 1.3.3 allows context-dependent attackers to conduct XML External Entity (XXE) attacks via a crafted XML document. |
| CVE-2012-1695 | Medium | 2012-05-03 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle JRockit component in Oracle Fusion Middleware 28.2.2 and earlier, and JDK/JRE 5 and 6 27.7.1 and earlier, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |