
Oracle Critical Patch Update January 2020
Released January 2020 · Oracle's advisory ↗ · ← Critical Patch Update, October 2019 · Critical Patch Update, April 2020 →
255 CVEs in this release, one square each
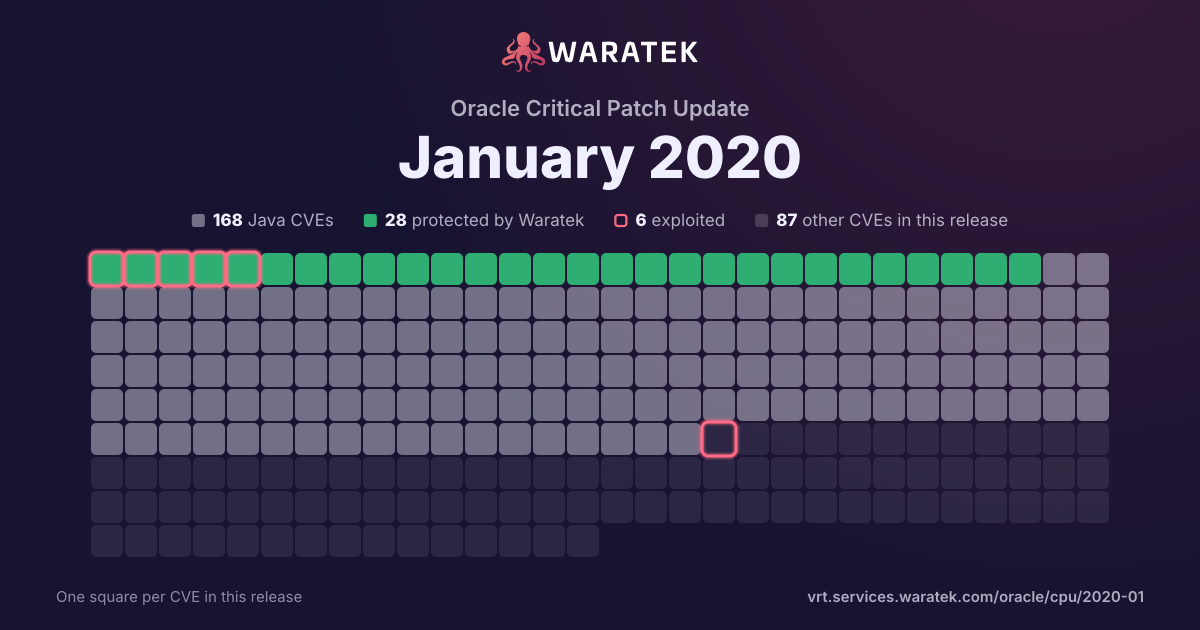
By status
28Protected by Waratek140No exploit published35Outside Waratek scope52Not applicable
6Exploited, marked by the ring
No exploit published. For 132 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 4 in Waratek scope · 4 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
5matches
4in Waratek scope80.0%
4protected80.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC20.0%
1EPSS ≥ 0.520.0%
Protected by Waratek
4
80.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
1
20.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
4
80.0%
partly blocked
0
0.0%
not blocked
1
20.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
20.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
4
80.0%
split by
peak 1 / month
Apr 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Working exploit published1
May 170
Jun 171
Not applicable1
High1
not blocked1
No public exploit1
Jul 171
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Aug 170
Sep 171
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
Oct 170
Nov 170
Dec 171
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Apr 17May 17Jun 17Jul 17Aug 17Sep 17Oct 17Nov 17Dec 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-15708 | Critical | 2017-12-11 | Protected by Waratek | No public exploit | In Apache Synapse, by default no authentication is required for Java Remote Method Invocation (RMI). So Apache Synapse 3.0.1 or all previous releases (3.0.0, 2.1.0, 2.0.0, 1.2, 1.1.2, 1.1.1) allows remote code execution attacks that can be performed by injecting specially crafted serialized objects. And the presence of Apache Commons Collections 3.2.1 (commons-collections-3.2.1.jar) or previous versions in Synapse distribution makes this exploitable. To mitigate the issue, we need to limit RMI access to trusted users only. Further upgrading to 3.0.1 version will eliminate the risk of having said Commons Collection version. In Synapse 3.0.1, Commons Collection has been updated to 3.2.2 version. |
| CVE-2017-14735 | Medium | 2017-09-25 | Protected by Waratek | No public exploit | OWASP AntiSamy before 1.5.7 allows XSS via HTML5 entities, as demonstrated by use of : to construct a javascript: URL. |
| CVE-2016-4000 | Critical | 2017-07-06 | Protected by Waratek | No public exploit | Jython before 2.7.1rc1 allows attackers to execute arbitrary code via a crafted serialized PyFunction object. |
| CVE-2017-1000376 | High | 2017-06-19 | Not applicable | No public exploit | libffi requests an executable stack allowing attackers to more easily trigger arbitrary code execution by overwriting the stack. Please note that libffi is used by a number of other libraries. It was previously stated that this affects libffi version 3.2.1 but this appears to be incorrect. libffi prior to version 3.1 on 32 bit x86 systems was vulnerable, and upstream is believed to have fixed this issue in version 3.1. |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |