
Oracle Critical Patch Update January 2020
Released January 2020 · Oracle's advisory ↗ · ← Critical Patch Update, October 2019 · Critical Patch Update, April 2020 →
255 CVEs in this release, one square each
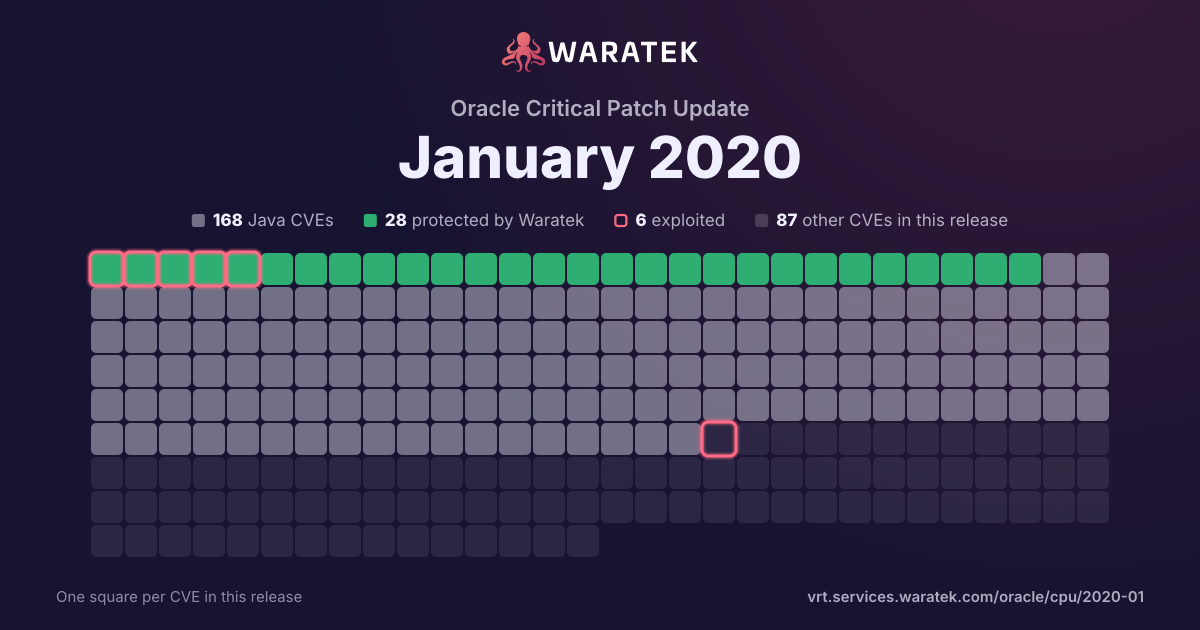
By status
28Protected by Waratek140No exploit published35Outside Waratek scope52Not applicable
6Exploited, marked by the ring
No exploit published. For 132 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 1 match · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV
1match
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
1
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
1
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
100.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-11477 | High | 2019-06-19 | Not applicable | Proof of concept only | Jonathan Looney discovered that the TCP_SKB_CB(skb)->tcp_gso_segs value was subject to an integer overflow in the Linux kernel when handling TCP Selective Acknowledgments (SACKs). A remote attacker could use this to cause a denial of service. This has been fixed in stable kernel releases 4.4.182, 4.9.182, 4.14.127, 4.19.52, 5.1.11, and is fixed in commit 3b4929f65b0d8249f19a50245cd88ed1a2f78cff. |