
Oracle Critical Patch Update January 2020
Released January 2020 · Oracle's advisory ↗ · ← Critical Patch Update, October 2019 · Critical Patch Update, April 2020 →
255 CVEs in this release, one square each
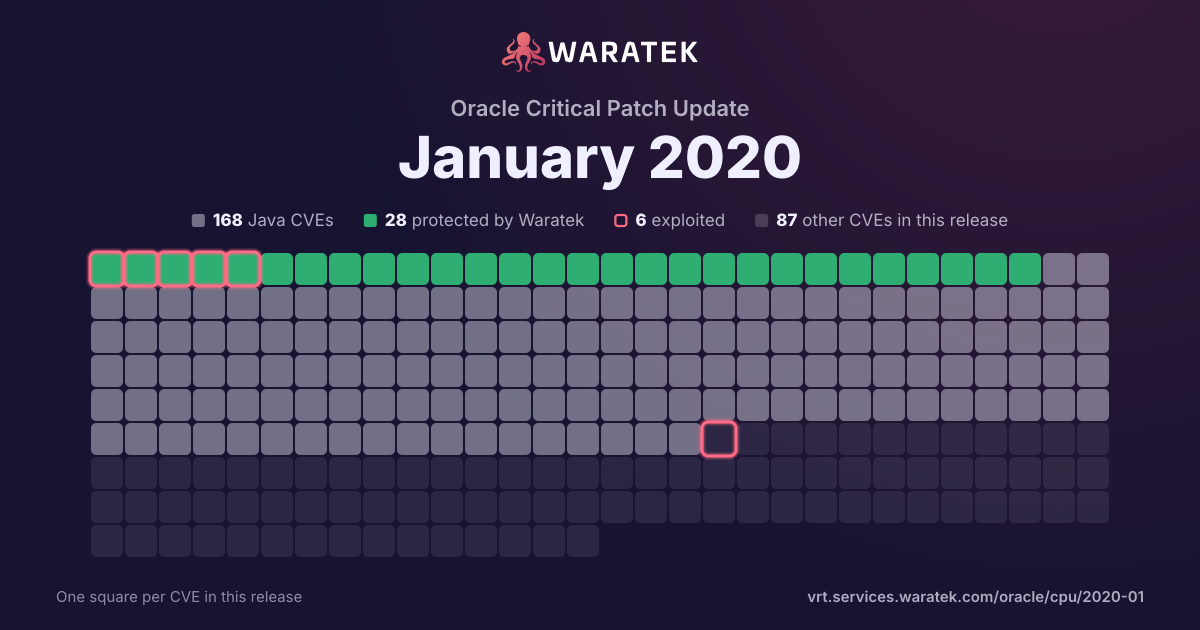
By status
29Protected by Waratek3Mitigation candidate145No exploit published9Outside Waratek scope69Not applicable
6Exploited, marked by the ring
No exploit published. For 135 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 205 matches · 143 in Waratek scope · 11 protected · 2 exploited · 2 CISA KEV · 4 public PoC · 2 EPSS ≥ 0.5
205matches
143in Waratek scope69.8%
11protected5.4%
2exploited1.0%
2CISA KEV1.0%
4public PoC2.0%
2EPSS ≥ 0.51.0%
Protected by Waratek
11
5.4%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
132
64.4%
Outside Waratek scope
9
4.4%
Not applicable
53
25.9%
Withdrawn CVE
0
0.0%
blocked by ARMR today
11
5.4%
partly blocked
0
0.0%
not blocked
194
94.6%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 203 / quarter
Q1 20203
Protected by Waratek10
No exploit published132
Outside Waratek scope9
Not applicable52
Critical5
High39
Medium145
Low14
blocked by ARMR today10
not blocked193
Exploited2
Proof of concept only1
No public exploit200
Q2 200
Q3 200
Q4 200
Q1 210
Q2 211
Protected by Waratek1
Medium1
blocked by ARMR today1
Working exploit published1
Q3 210
Q4 210
Q1 220
Q2 220
Q3 220
Q4 221
Not applicable1
High1
not blocked1
No public exploit1
Q1 20Q2 20Q3 20Q4 20Q1 21Q2 21Q3 21Q4 21Q1 22Q2 22Q3 22Q4 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2020-2516 | Low | 2020-01-15 | Outside Waratek scope | No public exploit | Vulnerability in the Core RDBMS component of Oracle Database Server. Supported versions that are affected are 12.1.0.2, 12.2.0.1, 18c and 19c. Easily exploitable vulnerability allows high privileged attacker having Create Materialized View, Create Table privilege with network access via OracleNet to compromise Core RDBMS. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Core RDBMS accessible data. CVSS 3.0 Base Score 2.4 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:N/I:L/A:N). |
| CVE-2020-2515 | Medium | 2020-01-15 | Outside Waratek scope | No public exploit | Vulnerability in the Database Gateway for ODBC component of Oracle Database Server. Supported versions that are affected are 11.2.0.4, 12.1.0.2, 12.2.0.1, 18c and 19c. Difficult to exploit vulnerability allows low privileged attacker having Create Session privilege with network access via OracleNet to compromise Database Gateway for ODBC. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Database Gateway for ODBC accessible data as well as unauthorized read access to a subset of Database Gateway for ODBC accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Database Gateway for ODBC. CVSS 3.0 Base Score 5.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:L/A:L). |
| CVE-2020-2512 | Medium | 2020-01-15 | Outside Waratek scope | No public exploit | Vulnerability in the Database Gateway for ODBC component of Oracle Database Server. Supported versions that are affected are 11.2.0.4, 12.1.0.2, 12.2.0.1, 18c and 19c. Difficult to exploit vulnerability allows unauthenticated attacker with network access via OracleNet to compromise Database Gateway for ODBC. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Database Gateway for ODBC. CVSS 3.0 Base Score 5.9 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2020-2511 | High | 2020-01-15 | Outside Waratek scope | No public exploit | Vulnerability in the Core RDBMS component of Oracle Database Server. Supported versions that are affected are 12.1.0.2, 12.2.0.1, 18c and 19c. Easily exploitable vulnerability allows low privileged attacker having Create Session privilege with network access via OracleNet to compromise Core RDBMS. While the vulnerability is in Core RDBMS, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Core RDBMS. CVSS 3.0 Base Score 7.7 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:N/I:N/A:H). |
| CVE-2020-2510 | High | 2020-01-15 | Outside Waratek scope | No public exploit | Vulnerability in the Core RDBMS component of Oracle Database Server. Supported versions that are affected are 11.2.0.4, 12.1.0.2, 12.2.0.1, 18c and 19c. Difficult to exploit vulnerability allows unauthenticated attacker with network access via OracleNet to compromise Core RDBMS. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Core RDBMS. CVSS 3.0 Base Score 7.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |