
Oracle Critical Patch Update January 2020
Released January 2020 · Oracle's advisory ↗ · ← Critical Patch Update, October 2019 · Critical Patch Update, April 2020 →
255 CVEs in this release, one square each
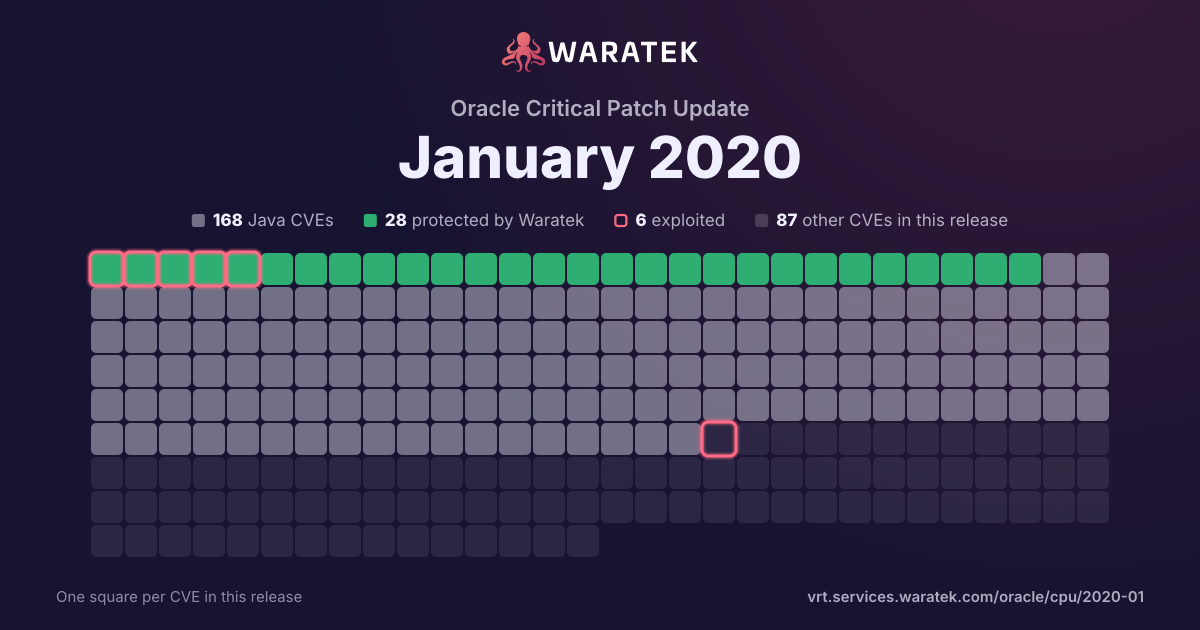
By status
28Protected by Waratek140No exploit published35Outside Waratek scope52Not applicable
6Exploited, marked by the ring
No exploit published. For 132 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 3 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
3
60.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
40.0%
blocked by ARMR today
3
60.0%
partly blocked
0
0.0%
not blocked
2
40.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
20.0%
Proof of concept only
1
20.0%
Forecast only
0
0.0%
No public exploit
3
60.0%
split by
peak 2 / year
20121
No exploit published1
Medium1
not blocked1
No public exploit1
20130
20141
Protected by Waratek1
Medium1
blocked by ARMR today1
Working exploit published1
20150
20160
20171
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
20180
20192
Protected by Waratek1
No exploit published1
Medium2
blocked by ARMR today1
not blocked1
Proof of concept only1
No public exploit1
20122013201420152016201720182019
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-12814 | Medium | 2019-06-19 | Protected by Waratek | Proof of concept only | A Polymorphic Typing issue was discovered in FasterXML jackson-databind 2.x through 2.9.9. When Default Typing is enabled (either globally or for a specific property) for an externally exposed JSON endpoint and the service has JDOM 1.x or 2.x jar in the classpath, an attacker can send a specifically crafted JSON message that allows them to read arbitrary local files on the server. |
| CVE-2019-10247 | Medium | 2019-04-22 | No exploit published | No public exploit | In Eclipse Jetty version 7.x, 8.x, 9.2.27 and older, 9.3.26 and older, and 9.4.16 and older, the server running on any OS and Jetty version combination will reveal the configured fully qualified directory base resource location on the output of the 404 error for not finding a Context that matches the requested path. The default server behavior on jetty-distribution and jetty-home will include at the end of the Handler tree a DefaultHandler, which is responsible for reporting this 404 error, it presents the various configured contexts as HTML for users to click through to. This produced HTML includes output that contains the configured fully qualified directory base resource location for each context. |
| CVE-2017-14735 | Medium | 2017-09-25 | Protected by Waratek | No public exploit | OWASP AntiSamy before 1.5.7 allows XSS via HTML5 entities, as demonstrated by use of : to construct a javascript: URL. |
| CVE-2014-3004 | Medium | 2014-06-11 | Protected by Waratek | Working exploit published | The default configuration for the Xerces SAX Parser in Castor before 1.3.3 allows context-dependent attackers to conduct XML External Entity (XXE) attacks via a crafted XML document. |
| CVE-2012-1695 | Medium | 2012-05-03 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle JRockit component in Oracle Fusion Middleware 28.2.2 and earlier, and JDK/JRE 5 and 6 27.7.1 and earlier, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |