
Oracle Critical Patch Update October 2019
Released October 2019 · Oracle's advisory ↗ · ← Critical Patch Update, July 2019 · Critical Patch Update, January 2020 →
180 CVEs in this release, one square each
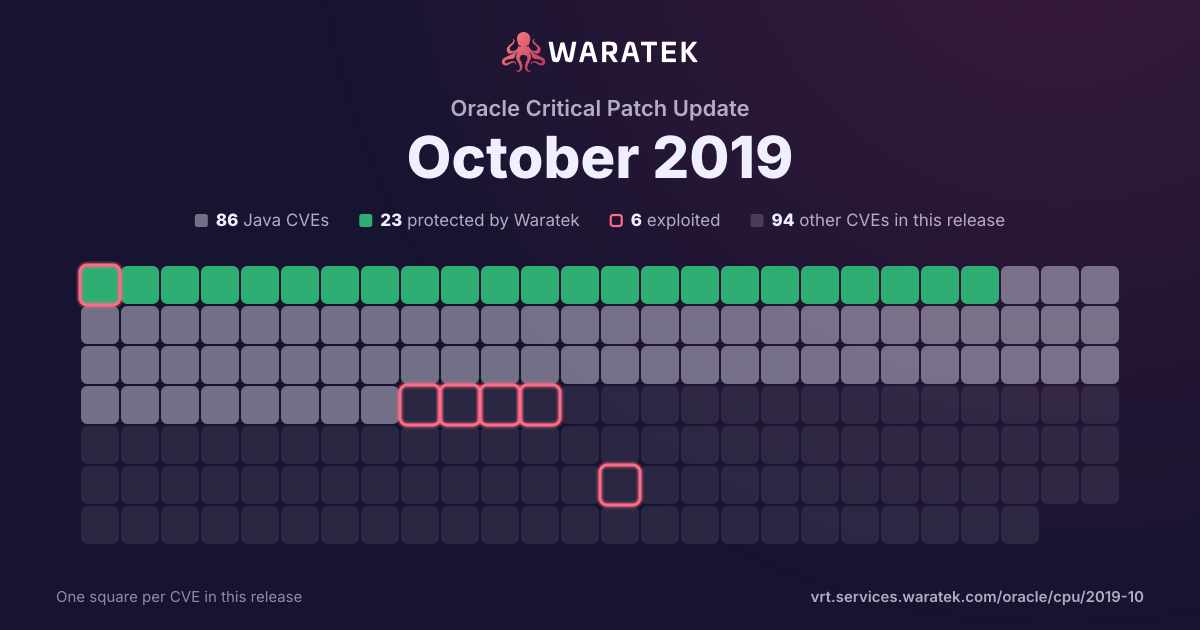
By status
24Protected by Waratek5Mitigation candidate65No exploit published17Outside Waratek scope69Not applicable
6Exploited, marked by the ring
No exploit published. For 56 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 6 in Waratek scope · 6 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
8matches
6in Waratek scope75.0%
6protected75.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC12.5%
1EPSS ≥ 0.512.5%
Protected by Waratek
6
75.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
2
25.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
6
75.0%
partly blocked
0
0.0%
not blocked
2
25.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
12.5%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
7
87.5%
split by
peak 2 / quarter
Q2 161
Not applicable1
Critical1
not blocked1
No public exploit1
Q3 160
Q4 161
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q1 170
Q2 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Working exploit published1
Q3 171
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q4 170
Q1 182
Protected by Waratek1
Not applicable1
Critical2
blocked by ARMR today1
not blocked1
No public exploit2
Q2 180
Q3 180
Q4 180
Q1 192
Protected by Waratek2
Critical2
blocked by ARMR today2
No public exploit2
Q2 16Q3 16Q4 16Q1 17Q2 17Q3 17Q4 17Q1 18Q2 18Q3 18Q4 18Q1 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-19362 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.8 might allow attackers to have unspecified impact by leveraging failure to block the jboss-common-core class from polymorphic deserialization. |
| CVE-2018-14721 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.7 might allow remote attackers to conduct server-side request forgery (SSRF) attacks by leveraging failure to block the axis2-jaxws class from polymorphic deserialization. |
| CVE-2018-1000007 | Critical | 2018-01-24 | Not applicable | No public exploit | libcurl 7.1 through 7.57.0 might accidentally leak authentication data to third parties. When asked to send custom headers in its HTTP requests, libcurl will send that set of headers first to the host in the initial URL but also, if asked to follow redirects and a 30X HTTP response code is returned, to the host mentioned in URL in the `Location:` response header value. Sending the same set of headers to subsequent hosts is in particular a problem for applications that pass on custom `Authorization:` headers, as this header often contains privacy sensitive information or data that could allow others to impersonate the libcurl-using client's request. |
| CVE-2016-6814 | Critical | 2018-01-18 | Protected by Waratek | No public exploit | When an application with unsupported Codehaus versions of Groovy from 1.7.0 to 2.4.3, Apache Groovy 2.4.4 to 2.4.7 on classpath uses standard Java serialization mechanisms, e.g. to communicate between servers or to store local data, it was possible for an attacker to bake a special serialized object that will execute code directly when deserialized. All applications which rely on serialization and do not isolate the code which deserializes objects were subject to this vulnerability. |
| CVE-2016-4000 | Critical | 2017-07-06 | Protected by Waratek | No public exploit | Jython before 2.7.1rc1 allows attackers to execute arbitrary code via a crafted serialized PyFunction object. |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |
| CVE-2016-1000031 | Critical | 2016-10-25 | Protected by Waratek | No public exploit | Apache Commons FileUpload before 1.3.3 DiskFileItem File Manipulation Remote Code Execution |
| CVE-2016-0729 | Critical | 2016-04-07 | Not applicable | No public exploit | Multiple buffer overflows in (1) internal/XMLReader.cpp, (2) util/XMLURL.cpp, and (3) util/XMLUri.cpp in the XML Parser library in Apache Xerces-C before 3.1.3 allow remote attackers to cause a denial of service (segmentation fault or memory corruption) or possibly execute arbitrary code via a crafted document. |