
WaratekVRT Sign in

Oracle Critical Patch Update October 2019

Released October 2019 · Oracle's advisory ↗ · ← Critical Patch Update, July 2019 · Critical Patch Update, January 2020 →

180 CVEs in this release, one square each
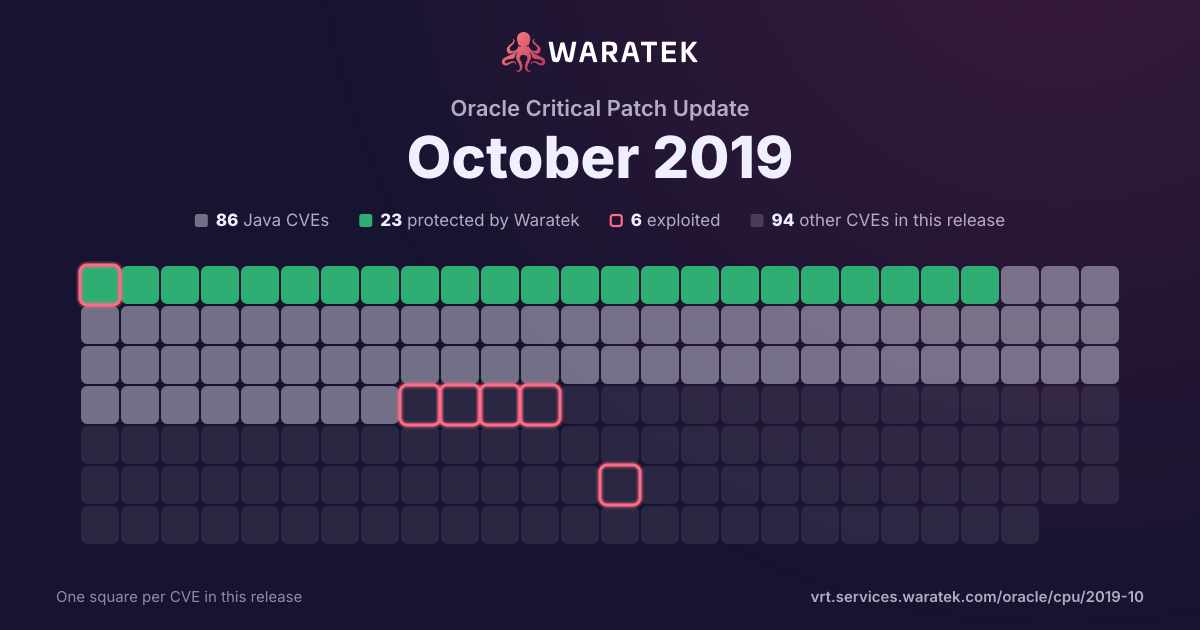
Protected by Waratek, exploitedProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekMitigation candidate, exploitedMitigation candidate, exploitedMitigation candidate, exploitedMitigation candidateMitigation candidateNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeNot applicable, exploitedNot applicable, exploitedNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicable
Share this chart Oracle Critical Patch Update October 2019, one square per CVE: 94 Java CVEs, 24 protected by Waratek, 6 exploited, 86 other CVEs in this release.

Download the image

By status

No exploit published. For 56 of them, Oracle's security advisory is the source of public detail.

Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.

Reset
More filters (1)
Columns
Including CVEs outside Waratek scope✕Published to 2018-02-28✕
Overview 3 matches · 1 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
3matches 1in Waratek scope33.3% 0protected0.0% 0exploited0.0% 0CISA KEV0.0% 0public PoC0.0% 0EPSS ≥ 0.50.0%
Protected by Waratek 0 0.0% Rule in development 0 0.0% Mitigation candidate 0 0.0% No exploit published 1 33.3% Outside Waratek scope 0 0.0% Not applicable 2 66.7% Withdrawn CVE 0 0.0%
Critical 0 0.0% High 3 100.0% Medium 0 0.0% Low 0 0.0% None 0 0.0% Unknown 0 0.0%
blocked by ARMR today 0 0.0% partly blocked 0 0.0% not blocked 3 100.0% not established 0 0.0% unrecorded 0 0.0%
Exploited 0 0.0% Working exploit published 0 0.0% Proof of concept only 0 0.0% Forecast only 0 0.0% No public exploit 3 100.0%
split by peak 1 / month
Feb 17Mar 17Apr 17May 17Jun 17Jul 17Aug 17Sep 17Oct 17Nov 17Dec 17Jan 18
3 matches Sign in to download these CVEs as CSV or JSON, or to follow them in a feed.
CVE Severity Published▾ Status Exploitation Description
CVE-2017-12626 High 2018-01-29 No exploit published No public exploit Apache POI in versions prior to release 3.17 are vulnerable to Denial of Service Attacks: 1) Infinite Loops while parsing crafted WMF, EMF, MSG and macros (POI bugs 61338 and 61294), and 2) Out of Memory Exceptions while parsing crafted DOC, PPT and XLS (POI bugs 52372 and 61295).
CVE-2015-5180 High 2017-06-27 Not applicable No public exploit res_query in libresolv in glibc before 2.25 allows remote attackers to cause a denial of service (NULL pointer dereference and process crash).
CVE-2017-6056 High 2017-02-17 Not applicable No public exploit It was discovered that a programming error in the processing of HTTPS requests in the Apache Tomcat servlet and JSP engine may result in denial of service via an infinite loop. The denial of service is easily achievable as a consequence of backporting a CVE-2016-6816 fix but not backporting the fix for Tomcat bug 57544. Distributions affected by this backporting issue include Debian (before 7.0.56-3+deb8u8 and 8.0.14-1+deb8u7 in jessie) and Ubuntu.