
Oracle Critical Patch Update October 2019
Released October 2019 · Oracle's advisory ↗ · ← Critical Patch Update, July 2019 · Critical Patch Update, January 2020 →
180 CVEs in this release, one square each
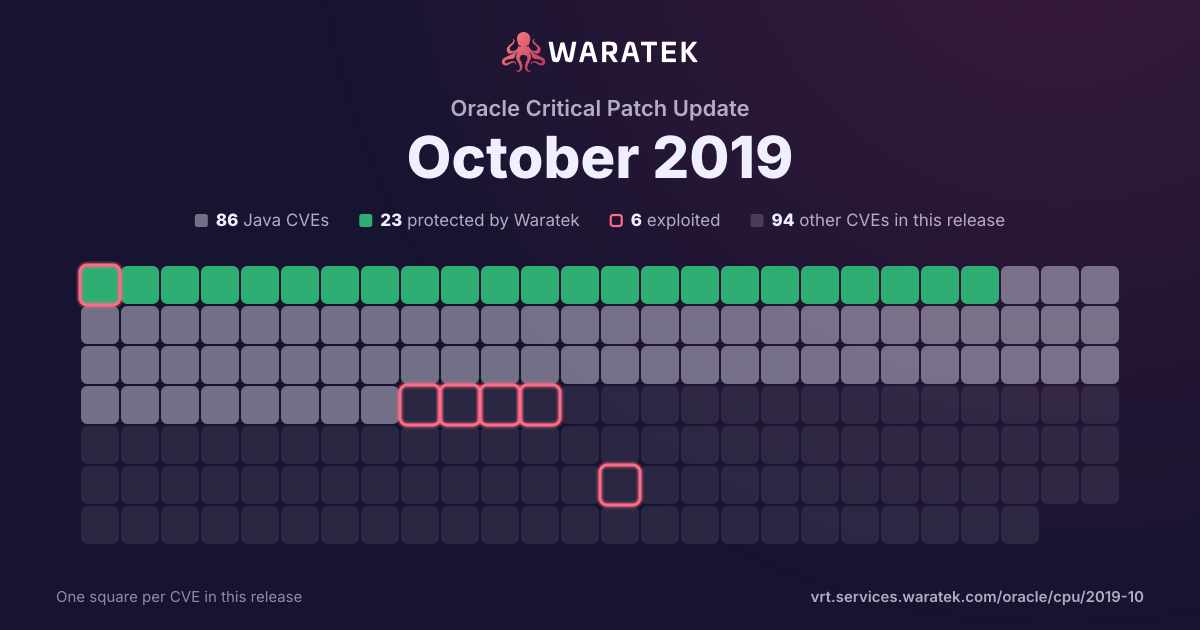
By status
24Protected by Waratek5Mitigation candidate65No exploit published17Outside Waratek scope69Not applicable
6Exploited, marked by the ring
No exploit published. For 56 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 4 in Waratek scope · 1 protected · 3 exploited · 1 CISA KEV · 3 public PoC · 3 EPSS ≥ 0.5
5matches
4in Waratek scope80.0%
1protected20.0%
3exploited60.0%
1CISA KEV20.0%
3public PoC60.0%
3EPSS ≥ 0.560.0%
Protected by Waratek
1
20.0%
Rule in development
0
0.0%
Mitigation candidate
2
40.0%
No exploit published
1
20.0%
Outside Waratek scope
0
0.0%
Not applicable
1
20.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
20.0%
partly blocked
0
0.0%
not blocked
4
80.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
60.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
2
40.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-10247 | Medium | 2019-04-22 | No exploit published | No public exploit | In Eclipse Jetty version 7.x, 8.x, 9.2.27 and older, 9.3.26 and older, and 9.4.16 and older, the server running on any OS and Jetty version combination will reveal the configured fully qualified directory base resource location on the output of the 404 error for not finding a Context that matches the requested path. The default server behavior on jetty-distribution and jetty-home will include at the end of the Handler tree a DefaultHandler, which is responsible for reporting this 404 error, it presents the various configured contexts as HTML for users to click through to. This produced HTML includes output that contains the configured fully qualified directory base resource location for each context. |
| CVE-2019-11358 | Medium | 2019-04-20 | Mitigation candidate | Exploited | jQuery before 3.4.0, as used in Drupal, Backdrop CMS, and other products, mishandles jQuery.extend(true, {}, ...) because of Object.prototype pollution. If an unsanitized source object contained an enumerable __proto__ property, it could extend the native Object.prototype. |
| CVE-2019-0232 | High | 2019-04-15 | Protected by Waratek | Exploited | When running on Windows with enableCmdLineArguments enabled, the CGI Servlet in Apache Tomcat 9.0.0.M1 to 9.0.17, 8.5.0 to 8.5.39 and 7.0.0 to 7.0.93 is vulnerable to Remote Code Execution due to a bug in the way the JRE passes command line arguments to Windows. The CGI Servlet is disabled by default. The CGI option enableCmdLineArguments is disable by default in Tomcat 9.0.x (and will be disabled by default in all versions in response to this vulnerability). For a detailed explanation of the JRE behaviour, see Markus Wulftange's blog (https://codewhitesec.blogspot.com/2016/02/java-and-command-line-injections-in-windows.html) and this archived MSDN blog (https://web.archive.org/web/20161228144344/https://blogs.msdn.microsoft.com/twistylittlepassagesallalike/2011/04/23/everyone-quotes-command-line-arguments-the-wrong-way/). |
| CVE-2019-11068 | Critical | 2019-04-10 | Not applicable | No public exploit | libxslt through 1.1.33 allows bypass of a protection mechanism because callers of xsltCheckRead and xsltCheckWrite permit access even upon receiving a -1 error code. xsltCheckRead can return -1 for a crafted URL that is not actually invalid and is subsequently loaded. |
| CVE-2019-0211 | High | 2019-04-08 | Mitigation candidate | Exploited | In Apache HTTP Server 2.4 releases 2.4.17 to 2.4.38, with MPM event, worker or prefork, code executing in less-privileged child processes or threads (including scripts executed by an in-process scripting interpreter) could execute arbitrary code with the privileges of the parent process (usually root) by manipulating the scoreboard. Non-Unix systems are not affected. |