
Oracle Critical Patch Update October 2019
Released October 2019 · Oracle's advisory ↗ · ← Critical Patch Update, July 2019 · Critical Patch Update, January 2020 →
180 CVEs in this release, one square each
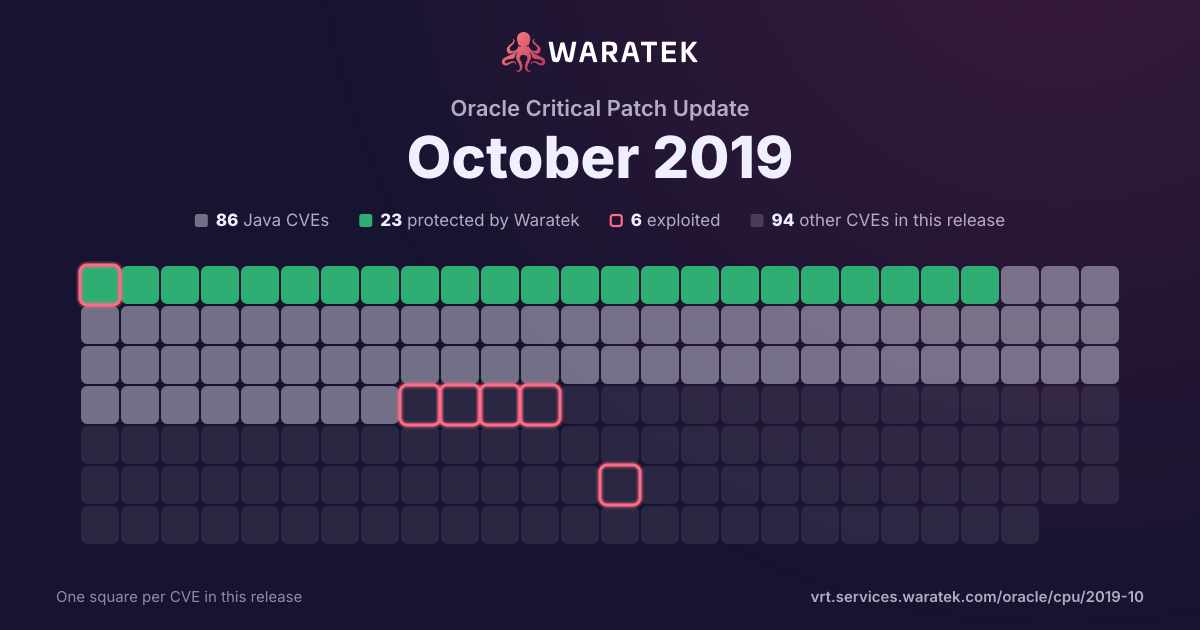
By status
24Protected by Waratek5Mitigation candidate65No exploit published17Outside Waratek scope69Not applicable
6Exploited, marked by the ring
No exploit published. For 56 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 9 matches · 5 in Waratek scope · 3 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
9matches
5in Waratek scope55.6%
3protected33.3%
0exploited0.0%
0CISA KEV0.0%
1public PoC11.1%
0EPSS ≥ 0.50.0%
Protected by Waratek
3
33.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
22.2%
Outside Waratek scope
0
0.0%
Not applicable
4
44.4%
Withdrawn CVE
0
0.0%
blocked by ARMR today
3
33.3%
partly blocked
0
0.0%
not blocked
6
66.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
11.1%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
8
88.9%
split by
peak 3 / month
Jan 192
Protected by Waratek2
Critical2
blocked by ARMR today2
No public exploit2
Feb 190
Mar 191
Not applicable1
Critical1
not blocked1
No public exploit1
Apr 191
Not applicable1
Critical1
not blocked1
No public exploit1
May 191
Not applicable1
Critical1
not blocked1
No public exploit1
Jun 190
Jul 191
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Aug 190
Sep 190
Oct 193
No exploit published2
Not applicable1
Critical3
not blocked3
Working exploit published1
No public exploit2
Jan 19Feb 19Mar 19Apr 19May 19Jun 19Jul 19Aug 19Sep 19Oct 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-3025 | Critical | 2019-10-16 | Not applicable | Working exploit published | Vulnerability in the Oracle Hospitality RES 3700 component of Oracle Food and Beverage Applications. The supported version that is affected is 5.7. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Hospitality RES 3700. While the vulnerability is in Oracle Hospitality RES 3700, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Oracle Hospitality RES 3700. CVSS 3.0 Base Score 9.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2019-3020 | Critical | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Primavera P6 Enterprise Project Portfolio Management product of Oracle Construction and Engineering (component: Web Access). Supported versions that are affected are 15.1.0-15.2.18, 16.1.0-16.2.18, 17.1.0-17.12.14 and 18.1.0-18.8.11. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Primavera P6 Enterprise Project Portfolio Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Primavera P6 Enterprise Project Portfolio Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Primavera P6 Enterprise Project Portfolio Management accessible data as well as unauthorized access to critical data or complete access to all Primavera P6 Enterprise Project Portfolio Management accessible data. CVSS 3.0 Base Score 9.3 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:H/A:N). |
| CVE-2019-2904 | Critical | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Oracle JDeveloper and ADF product of Oracle Fusion Middleware (component: ADF Faces). Supported versions that are affected are 11.1.1.9.0, 12.1.3.0.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle JDeveloper and ADF. Successful attacks of this vulnerability can result in takeover of Oracle JDeveloper and ADF. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-14379 | Critical | 2019-07-29 | Protected by Waratek | No public exploit | SubTypeValidator.java in FasterXML jackson-databind before 2.9.9.2 mishandles default typing when ehcache is used (because of net.sf.ehcache.transaction.manager.DefaultTransactionManagerLookup), leading to remote code execution. |
| CVE-2019-8457 | Critical | 2019-05-30 | Not applicable | No public exploit | SQLite3 from 3.6.0 to and including 3.27.2 is vulnerable to heap out-of-bound read in the rtreenode() function when handling invalid rtree tables. |
| CVE-2019-11068 | Critical | 2019-04-10 | Not applicable | No public exploit | libxslt through 1.1.33 allows bypass of a protection mechanism because callers of xsltCheckRead and xsltCheckWrite permit access even upon receiving a -1 error code. xsltCheckRead can return -1 for a crafted URL that is not actually invalid and is subsequently loaded. |
| CVE-2019-3862 | Critical | 2019-03-21 | Not applicable | No public exploit | An out of bounds read flaw was discovered in libssh2 before 1.8.1 in the way SSH_MSG_CHANNEL_REQUEST packets with an exit status message and no payload are parsed. A remote attacker who compromises a SSH server may be able to cause a Denial of Service or read data in the client memory. |
| CVE-2018-19362 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.8 might allow attackers to have unspecified impact by leveraging failure to block the jboss-common-core class from polymorphic deserialization. |
| CVE-2018-14721 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.7 might allow remote attackers to conduct server-side request forgery (SSRF) attacks by leveraging failure to block the axis2-jaxws class from polymorphic deserialization. |