
WaratekVRT Sign in

Oracle Critical Patch Update October 2019

Released October 2019 · Oracle's advisory ↗ · ← Critical Patch Update, July 2019 · Critical Patch Update, January 2020 →

180 CVEs in this release, one square each
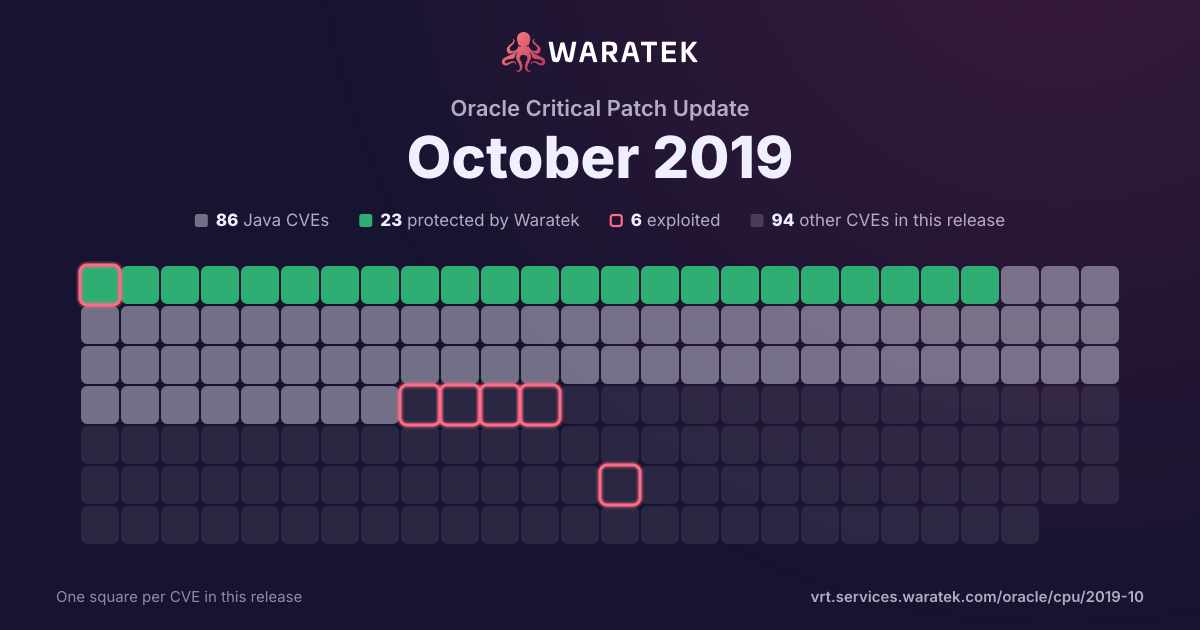
Protected by Waratek, exploitedProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekMitigation candidate, exploitedMitigation candidate, exploitedMitigation candidate, exploitedMitigation candidateMitigation candidateNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeNot applicable, exploitedNot applicable, exploitedNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicable
Share this chart Oracle Critical Patch Update October 2019, one square per CVE: 94 Java CVEs, 24 protected by Waratek, 6 exploited, 86 other CVEs in this release.

Download the image

By status

No exploit published. For 56 of them, Oracle's security advisory is the source of public detail.

Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.

Reset
More filters (1)
Columns
Including CVEs outside Waratek scope✕Published to 2019-01-31✕
Overview 2 matches · 1 in Waratek scope · 0 protected · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
2matches 1in Waratek scope50.0% 0protected0.0% 0CISA KEV0.0% 1public PoC50.0% 0EPSS ≥ 0.50.0%
Protected by Waratek 0 0.0% Rule in development 0 0.0% Mitigation candidate 1 50.0% No exploit published 0 0.0% Outside Waratek scope 0 0.0% Not applicable 1 50.0% Withdrawn CVE 0 0.0%
Critical 0 0.0% High 0 0.0% Medium 2 100.0% Low 0 0.0% None 0 0.0% Unknown 0 0.0%
blocked by ARMR today 0 0.0% partly blocked 0 0.0% not blocked 2 100.0% not established 0 0.0% unrecorded 0 0.0%
Exploited 2 100.0% Working exploit published 0 0.0% Proof of concept only 0 0.0% Forecast only 0 0.0% No public exploit 0 0.0%
split by peak 1 / month
Jan 18Mar 18May 18Jul 18Sep 18Nov 18Jan 19
2 matches Sign in to download these CVEs as CSV or JSON, or to follow them in a feed.
CVE Severity Published▾ Status Exploitation Description
CVE-2019-6109 Medium 2019-01-31 Not applicable Exploited An issue was discovered in OpenSSH 7.9. Due to missing character encoding in the progress display, a malicious server (or Man-in-The-Middle attacker) can employ crafted object names to manipulate the client output, e.g., by using ANSI control codes to hide additional files being transferred. This affects refresh_progress_meter() in progressmeter.c.
CVE-2015-9251 Medium 2018-01-18 Mitigation candidate Exploited jQuery before 3.0.0 is vulnerable to Cross-site Scripting (XSS) attacks when a cross-domain Ajax request is performed without the dataType option, causing text/javascript responses to be executed.