
Oracle Critical Patch Update October 2019
Released October 2019 · Oracle's advisory ↗ · ← Critical Patch Update, July 2019 · Critical Patch Update, January 2020 →
180 CVEs in this release, one square each
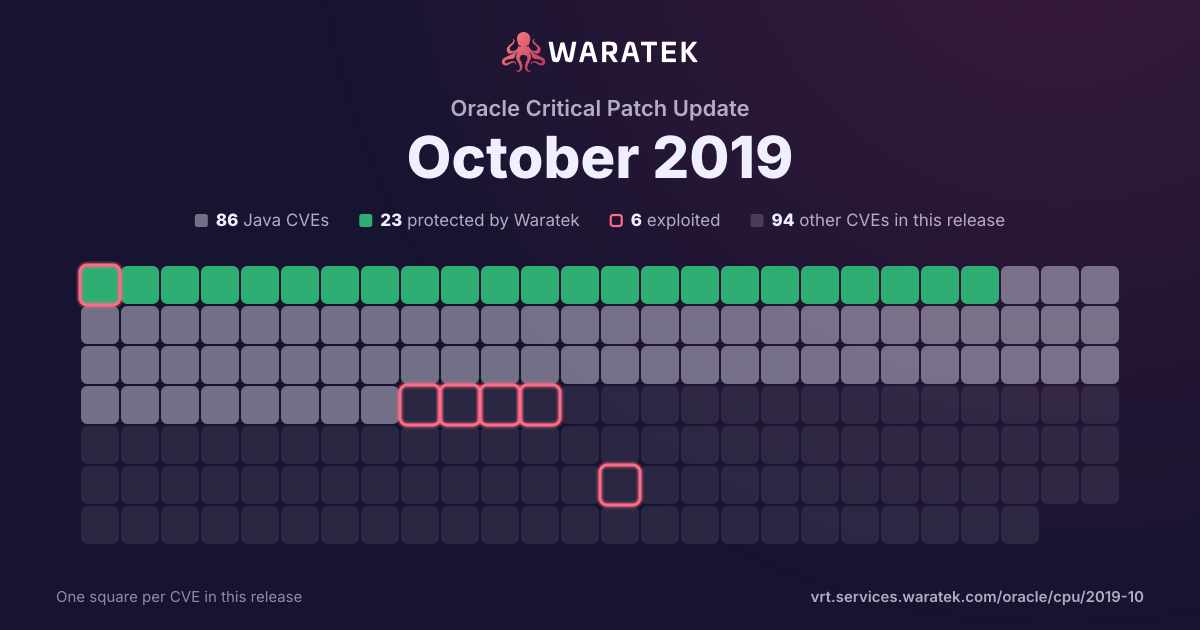
By status
23Protected by Waratek63No exploit published57Outside Waratek scope37Not applicable
6Exploited, marked by the ring
No exploit published. For 56 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 15 matches · 8 in Waratek scope · 6 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 1 EPSS ≥ 0.5
15matches
8in Waratek scope53.3%
6protected40.0%
0exploited0.0%
0CISA KEV0.0%
2public PoC13.3%
1EPSS ≥ 0.56.7%
Protected by Waratek
6
40.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
13.3%
Outside Waratek scope
1
6.7%
Not applicable
6
40.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
6
40.0%
partly blocked
0
0.0%
not blocked
9
60.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
2
13.3%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
13
86.7%
split by
peak 3 / quarter
Q2 161
Not applicable1
Critical1
not blocked1
No public exploit1
Q3 160
Q4 161
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q1 170
Q2 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Working exploit published1
Q3 171
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q4 170
Q1 182
Outside Waratek scope1
Not applicable1
Critical2
not blocked2
No public exploit2
Q2 180
Q3 180
Q4 180
Q1 193
Protected by Waratek2
Not applicable1
Critical3
blocked by ARMR today2
not blocked1
No public exploit3
Q2 192
Not applicable2
Critical2
not blocked2
No public exploit2
Q3 191
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q4 193
No exploit published2
Not applicable1
Critical3
not blocked3
Working exploit published1
No public exploit2
Q2 16Q4 16Q2 17Q4 17Q2 18Q4 18Q2 19Q4 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-3025 | Critical | 2019-10-16 | Not applicable | Working exploit published | Vulnerability in the Oracle Hospitality RES 3700 component of Oracle Food and Beverage Applications. The supported version that is affected is 5.7. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Hospitality RES 3700. While the vulnerability is in Oracle Hospitality RES 3700, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Oracle Hospitality RES 3700. CVSS 3.0 Base Score 9.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2019-3020 | Critical | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Primavera P6 Enterprise Project Portfolio Management product of Oracle Construction and Engineering (component: Web Access). Supported versions that are affected are 15.1.0-15.2.18, 16.1.0-16.2.18, 17.1.0-17.12.14 and 18.1.0-18.8.11. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Primavera P6 Enterprise Project Portfolio Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Primavera P6 Enterprise Project Portfolio Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Primavera P6 Enterprise Project Portfolio Management accessible data as well as unauthorized access to critical data or complete access to all Primavera P6 Enterprise Project Portfolio Management accessible data. CVSS 3.0 Base Score 9.3 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:H/A:N). |
| CVE-2019-2904 | Critical | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Oracle JDeveloper and ADF product of Oracle Fusion Middleware (component: ADF Faces). Supported versions that are affected are 11.1.1.9.0, 12.1.3.0.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle JDeveloper and ADF. Successful attacks of this vulnerability can result in takeover of Oracle JDeveloper and ADF. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-14379 | Critical | 2019-07-29 | Protected by Waratek | No public exploit | SubTypeValidator.java in FasterXML jackson-databind before 2.9.9.2 mishandles default typing when ehcache is used (because of net.sf.ehcache.transaction.manager.DefaultTransactionManagerLookup), leading to remote code execution. |
| CVE-2019-8457 | Critical | 2019-05-30 | Not applicable | No public exploit | SQLite3 from 3.6.0 to and including 3.27.2 is vulnerable to heap out-of-bound read in the rtreenode() function when handling invalid rtree tables. |
| CVE-2019-11068 | Critical | 2019-04-10 | Not applicable | No public exploit | libxslt through 1.1.33 allows bypass of a protection mechanism because callers of xsltCheckRead and xsltCheckWrite permit access even upon receiving a -1 error code. xsltCheckRead can return -1 for a crafted URL that is not actually invalid and is subsequently loaded. |
| CVE-2019-3862 | Critical | 2019-03-21 | Not applicable | No public exploit | An out of bounds read flaw was discovered in libssh2 before 1.8.1 in the way SSH_MSG_CHANNEL_REQUEST packets with an exit status message and no payload are parsed. A remote attacker who compromises a SSH server may be able to cause a Denial of Service or read data in the client memory. |
| CVE-2018-19362 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.8 might allow attackers to have unspecified impact by leveraging failure to block the jboss-common-core class from polymorphic deserialization. |
| CVE-2018-14721 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.7 might allow remote attackers to conduct server-side request forgery (SSRF) attacks by leveraging failure to block the axis2-jaxws class from polymorphic deserialization. |
| CVE-2018-1000007 | Critical | 2018-01-24 | Not applicable | No public exploit | libcurl 7.1 through 7.57.0 might accidentally leak authentication data to third parties. When asked to send custom headers in its HTTP requests, libcurl will send that set of headers first to the host in the initial URL but also, if asked to follow redirects and a 30X HTTP response code is returned, to the host mentioned in URL in the `Location:` response header value. Sending the same set of headers to subsequent hosts is in particular a problem for applications that pass on custom `Authorization:` headers, as this header often contains privacy sensitive information or data that could allow others to impersonate the libcurl-using client's request. |
| CVE-2016-6814 | Critical | 2018-01-18 | Outside Waratek scope | No public exploit | When an application with unsupported Codehaus versions of Groovy from 1.7.0 to 2.4.3, Apache Groovy 2.4.4 to 2.4.7 on classpath uses standard Java serialization mechanisms, e.g. to communicate between servers or to store local data, it was possible for an attacker to bake a special serialized object that will execute code directly when deserialized. All applications which rely on serialization and do not isolate the code which deserializes objects were subject to this vulnerability. |
| CVE-2016-4000 | Critical | 2017-07-06 | Protected by Waratek | No public exploit | Jython before 2.7.1rc1 allows attackers to execute arbitrary code via a crafted serialized PyFunction object. |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |
| CVE-2016-1000031 | Critical | 2016-10-25 | Protected by Waratek | No public exploit | Apache Commons FileUpload before 1.3.3 DiskFileItem File Manipulation Remote Code Execution |
| CVE-2016-0729 | Critical | 2016-04-07 | Not applicable | No public exploit | Multiple buffer overflows in (1) internal/XMLReader.cpp, (2) util/XMLURL.cpp, and (3) util/XMLUri.cpp in the XML Parser library in Apache Xerces-C before 3.1.3 allow remote attackers to cause a denial of service (segmentation fault or memory corruption) or possibly execute arbitrary code via a crafted document. |