
Oracle Critical Patch Update July 2019
Released July 2019 · Oracle's advisory ↗ · ← Critical Patch Update, April 2019 · Critical Patch Update, October 2019 →
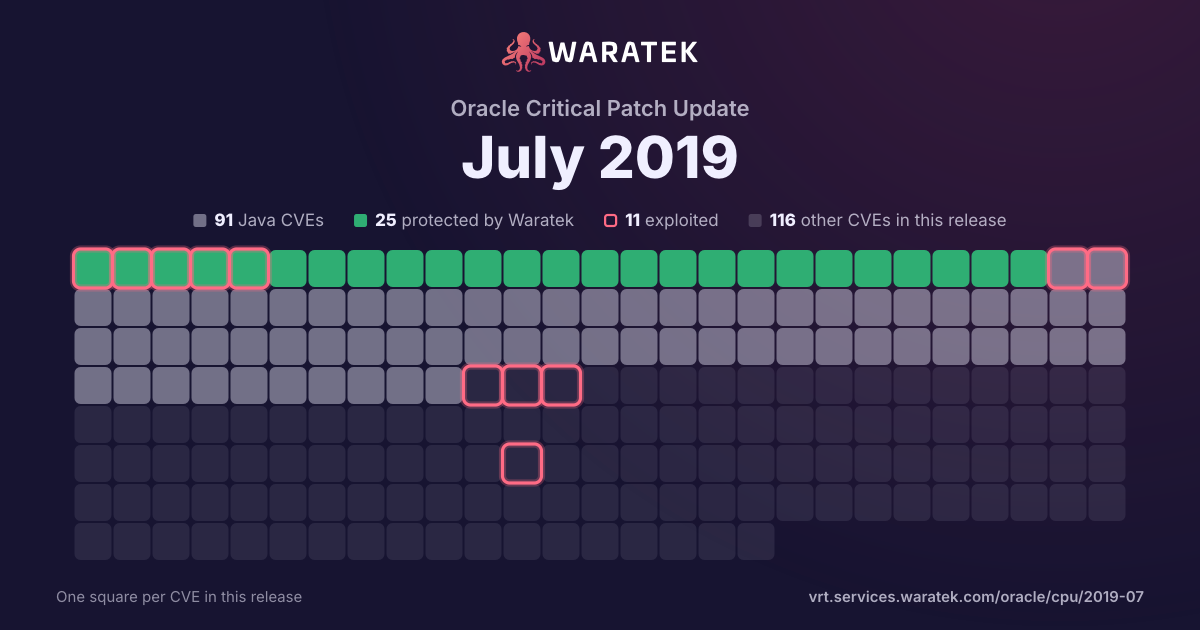
207 CVEs in this release, one square each
By status
25Protected by Waratek2Mitigation candidate64No exploit published55Outside Waratek scope61Not applicable
11Exploited, marked by the ring
No exploit published. For 58 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 1 match · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
1match
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
1
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
1
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
1
100.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-5597 | Critical | 2019-05-15 | Not applicable | No public exploit | In FreeBSD 11.3-PRERELEASE and 12.0-STABLE before r347591, 11.2-RELEASE before 11.2-RELEASE-p10, and 12.0-RELEASE before 12.0-RELEASE-p4, a bug in the pf IPv6 fragment reassembly logic incorrectly uses the last extension header offset from the last received packet instead of the first packet allowing maliciously crafted IPv6 packets to cause a crash or potentially bypass the packet filter. |