
Oracle Critical Patch Update July 2019
Released July 2019 · Oracle's advisory ↗ · ← Critical Patch Update, April 2019 · Critical Patch Update, October 2019 →
207 CVEs in this release, one square each
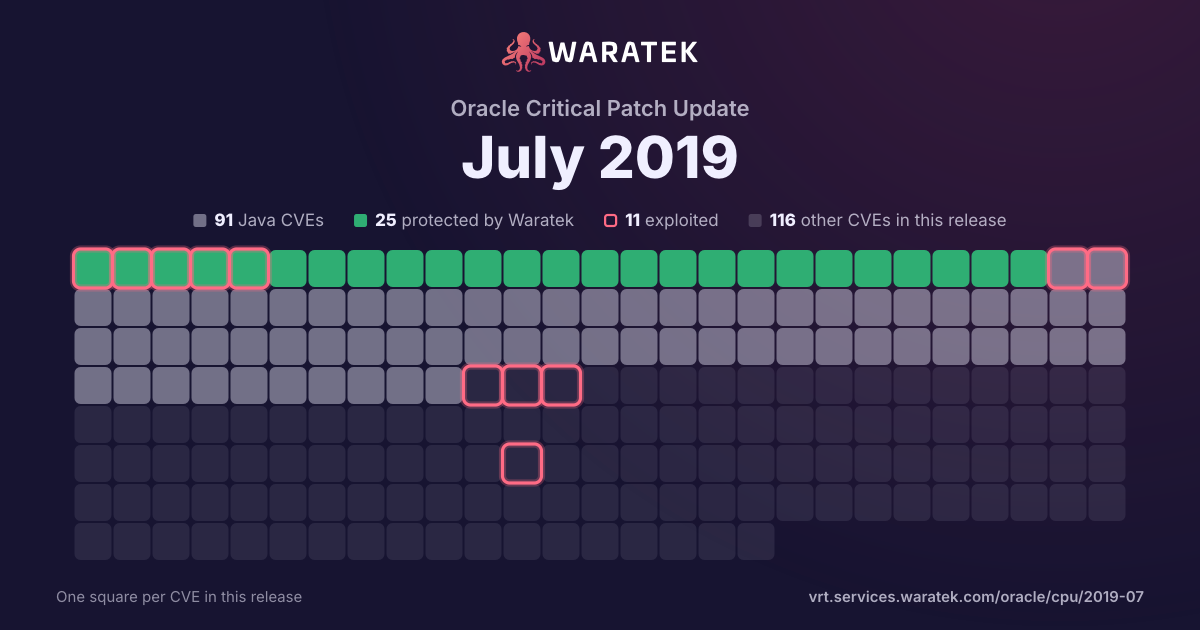
By status
25Protected by Waratek2Mitigation candidate64No exploit published55Outside Waratek scope61Not applicable
11Exploited, marked by the ring
No exploit published. For 58 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 9 matches · 3 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
9matches
3in Waratek scope33.3%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
3
33.3%
Outside Waratek scope
5
55.6%
Not applicable
1
11.1%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
9
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
9
100.0%
split by
peak 3 / quarter
Q1 182
Outside Waratek scope2
Critical2
not blocked2
No public exploit2
Q2 180
Q3 181
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q4 181
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q1 191
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q2 191
Not applicable1
Critical1
not blocked1
No public exploit1
Q3 193
No exploit published3
Critical3
not blocked3
No public exploit3
Q1 18Q2 18Q3 18Q4 18Q1 19Q2 19Q3 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-2856 | Critical | 2019-07-23 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Application Container - JavaEE). Supported versions that are affected is 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via T3 to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in takeover of Oracle WebLogic Server. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-2828 | Critical | 2019-07-23 | No exploit published | No public exploit | Vulnerability in the Oracle Field Service component of Oracle E-Business Suite (subcomponent: Wireless). Supported versions that are affected are 12.1.1 - 12.1.3 and 12.2.3 - 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Field Service. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Field Service, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Oracle Field Service. CVSS 3.0 Base Score 9.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2019-2775 | Critical | 2019-07-23 | No exploit published | No public exploit | Vulnerability in the Oracle Payments component of Oracle E-Business Suite (subcomponent: File Transmission). Supported versions that are affected are 12.1.1 - 12.1.3 and 12.2.3 - 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Payments. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Payments accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Payments. CVSS 3.0 Base Score 9.1 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:H/A:H). |
| CVE-2019-5597 | Critical | 2019-05-15 | Not applicable | No public exploit | In FreeBSD 11.3-PRERELEASE and 12.0-STABLE before r347591, 11.2-RELEASE before 11.2-RELEASE-p10, and 12.0-RELEASE before 12.0-RELEASE-p4, a bug in the pf IPv6 fragment reassembly logic incorrectly uses the last extension header offset from the last received packet instead of the first packet allowing maliciously crafted IPv6 packets to cause a crash or potentially bypass the packet filter. |
| CVE-2019-3822 | Critical | 2019-02-06 | Outside Waratek scope | No public exploit | libcurl versions from 7.36.0 to before 7.64.0 are vulnerable to a stack-based buffer overflow. The function creating an outgoing NTLM type-3 header (`lib/vauth/ntlm.c:Curl_auth_create_ntlm_type3_message()`), generates the request HTTP header contents based on previously received data. The check that exists to prevent the local buffer from getting overflowed is implemented wrongly (using unsigned math) and as such it does not prevent the overflow from happening. This output data can grow larger than the local buffer if very large 'nt response' data is extracted from a previous NTLMv2 header provided by the malicious or broken HTTP server. Such a 'large value' needs to be around 1000 bytes or more. The actual payload data copied to the target buffer comes from the NTLMv2 type-2 response header. |
| CVE-2018-18311 | Critical | 2018-12-07 | Outside Waratek scope | No public exploit | Perl before 5.26.3 and 5.28.x before 5.28.1 has a buffer overflow via a crafted regular expression that triggers invalid write operations. |
| CVE-2018-11058 | Critical | 2018-09-14 | Outside Waratek scope | No public exploit | RSA BSAFE Micro Edition Suite, versions prior to 4.0.11 (in 4.0.x) and prior to 4.1.6 (in 4.1.x), and RSA BSAFE Crypto-C Micro Edition, version prior to 4.0.5.3 (in 4.0.x) contain a Buffer Over-Read vulnerability when parsing ASN.1 data. A remote attacker could use maliciously constructed ASN.1 data that would result in such issue. |
| CVE-2018-1000120 | Critical | 2018-03-14 | Outside Waratek scope | No public exploit | A buffer overflow exists in curl 7.12.3 to and including curl 7.58.0 in the FTP URL handling that allows an attacker to cause a denial of service or worse. |
| CVE-2016-6814 | Critical | 2018-01-18 | Outside Waratek scope | No public exploit | When an application with unsupported Codehaus versions of Groovy from 1.7.0 to 2.4.3, Apache Groovy 2.4.4 to 2.4.7 on classpath uses standard Java serialization mechanisms, e.g. to communicate between servers or to store local data, it was possible for an attacker to bake a special serialized object that will execute code directly when deserialized. All applications which rely on serialization and do not isolate the code which deserializes objects were subject to this vulnerability. |