
Oracle Critical Patch Update July 2019
Released July 2019 · Oracle's advisory ↗ · ← Critical Patch Update, April 2019 · Critical Patch Update, October 2019 →
207 CVEs in this release, one square each
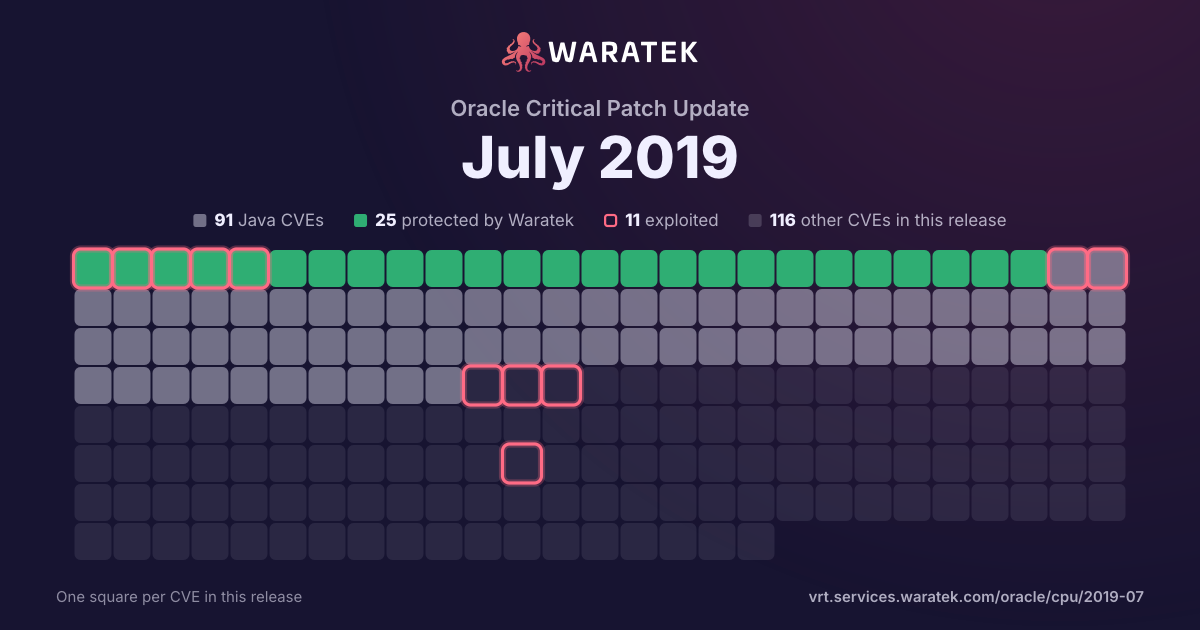
By status
26Protected by Waratek8Mitigation candidate69No exploit published9Outside Waratek scope95Not applicable
11Exploited, marked by the ring
No exploit published. For 59 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 0 protected · 5 exploited · 1 CISA KEV · 7 public PoC · 4 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
8
100.0%
No exploit published
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
7
87.5%
not established
1
12.5%
unrecorded
0
0.0%
Exploited
5
62.5%
Working exploit published
2
25.0%
Proof of concept only
1
12.5%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 3 / quarter
Q1 183
Mitigation candidate3
Medium3
not blocked3
Exploited1
Working exploit published1
Proof of concept only1
Q2 180
Q3 180
Q4 181
Mitigation candidate1
Medium1
not blocked1
Working exploit published1
Q1 190
Q2 192
Mitigation candidate2
High1
Medium1
not blocked2
Exploited2
Q3 192
Mitigation candidate2
High2
not blocked1
not established1
Exploited2
Q1 18Q2 18Q3 18Q4 18Q1 19Q2 19Q3 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-2768 | High | 2019-07-23 | Mitigation candidate | Exploited | Vulnerability in the BI Publisher (formerly XML Publisher) component of Oracle Fusion Middleware (subcomponent: BI Publisher Security). The supported version that is affected is 11.1.1.9.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher (formerly XML Publisher). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher (formerly XML Publisher) accessible data. CVSS 3.0 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2019-2767 | High | 2019-07-23 | Mitigation candidate | Exploited | Vulnerability in the BI Publisher (formerly XML Publisher) component of Oracle Fusion Middleware (subcomponent: BI Publisher Security). The supported version that is affected are 11.1.1.9.0, 12.2.1.3.0 and 12.2.1.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher (formerly XML Publisher). While the vulnerability is in BI Publisher (formerly XML Publisher), attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of BI Publisher (formerly XML Publisher) accessible data as well as unauthorized read access to a subset of BI Publisher (formerly XML Publisher) accessible data. CVSS 3.0 Base Score 7.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:L/I:L/A:N). |
| CVE-2019-11358 | Medium | 2019-04-20 | Mitigation candidate | Exploited | jQuery before 3.4.0, as used in Drupal, Backdrop CMS, and other products, mishandles jQuery.extend(true, {}, ...) because of Object.prototype pollution. If an unsanitized source object contained an enumerable __proto__ property, it could extend the native Object.prototype. |
| CVE-2019-0211 | High | 2019-04-08 | Mitigation candidate | Exploited | In Apache HTTP Server 2.4 releases 2.4.17 to 2.4.38, with MPM event, worker or prefork, code executing in less-privileged child processes or threads (including scripts executed by an in-process scripting interpreter) could execute arbitrary code with the privileges of the parent process (usually root) by manipulating the scoreboard. Non-Unix systems are not affected. |
| CVE-2018-11784 | Medium | 2018-10-04 | Mitigation candidate | Working exploit published | When the default servlet in Apache Tomcat versions 9.0.0.M1 to 9.0.11, 8.5.0 to 8.5.33 and 7.0.23 to 7.0.90 returned a redirect to a directory (e.g. redirecting to '/foo/' when the user requested '/foo') a specially crafted URL could be used to cause the redirect to be generated to any URI of the attackers choice. |
| CVE-2018-1305 | Medium | 2018-02-23 | Mitigation candidate | Proof of concept only | Security constraints defined by annotations of Servlets in Apache Tomcat 9.0.0.M1 to 9.0.4, 8.5.0 to 8.5.27, 8.0.0.RC1 to 8.0.49 and 7.0.0 to 7.0.84 were only applied once a Servlet had been loaded. Because security constraints defined in this way apply to the URL pattern and any URLs below that point, it was possible - depending on the order Servlets were loaded - for some security constraints not to be applied. This could have exposed resources to users who were not authorised to access them. |
| CVE-2015-9251 | Medium | 2018-01-18 | Mitigation candidate | Exploited | jQuery before 3.0.0 is vulnerable to Cross-site Scripting (XSS) attacks when a cross-domain Ajax request is performed without the dataType option, causing text/javascript responses to be executed. |
| CVE-2017-5715 | Medium | 2018-01-04 | Mitigation candidate | Working exploit published | Systems with microprocessors utilizing speculative execution and indirect branch prediction may allow unauthorized disclosure of information to an attacker with local user access via a side-channel analysis. |